How Hotels Measure Real Cost Per Booking by Channel
Calculate true hotel cost per booking across OTA, direct, GDS & WhatsApp. Step-by-step formula, Riyadh example & ways to cut distribution costs in Saudi Arabia....
Quick answer: A hotel IT manager selects the right system by validating three things together: technical conformity with ZATCA Phase 2 (XML invoice format, cryptographic stamp, QR code, real-time integration with the Fatoora platform), information security and guest data protection aligned with Saudi Arabia's Personal Data Protection Law and the National Cybersecurity Authority controls, and hospitality-specific operational fit covering folios, deposits, credit notes, group billing and corporate ledgers. A system that satisfies only two of the three is a deferred risk, not a good deal.
The role of the hotel IT manager in Saudi Arabia has changed faster than most job descriptions have. It is no longer about patching the Wi-Fi, resetting front-desk passwords and keeping the printers alive. It now sits at the intersection of three high-stakes domains: tax compliance, cybersecurity, and guest experience. One weak decision on a hotel property management system (PMS) can surface months later as a tax penalty, a guest data breach, or a full stop on check-ins during your busiest night of the year.
As e-invoicing for hotels in Saudi Arabia expands wave after wave, the practical question facing IT leaders in Riyadh, Jeddah, Makkah, Dammam, Khobar and AlUla is direct: how do I choose a hotel system that is genuinely secure and ZATCA-compliant without disrupting daily operations or doubling my cost base? This guide answers that question with measurable criteria rather than vendor slogans.
The phrase "ZATCA-compliant" appears in almost every vendor pitch deck in the Kingdom. In practice, compliance is not a label a supplier grants itself. It is a defined set of technical requirements a system must demonstrate first in the sandbox environment and then in production.
Phase 1, the Generation phase, began on 4 December 2021. It required businesses to issue and store invoices electronically in a structured format, with no direct connection to the tax authority's systems. Phase 2, the Integration phase, launched its first wave on 1 January 2023 and changed the rules entirely. The system must now connect directly to the Fatoora platform through APIs. Standard tax invoices are cleared in real time before they are handed to the buyer, while simplified invoices must be reported within 24 hours of issuance.
Enforcement rolls out in waves based on VAT-taxable revenue, and ZATCA notifies targeted taxpayers well ahead of their integration date. The revenue threshold has fallen steadily with each wave. Wave 24 targeted businesses exceeding SAR 375,000 in taxable revenue in 2022, 2023 or 2024, with an integration deadline of 30 June 2026. Wave 25 lowered the bar to SAR 187,500 across 2022 to 2025, with integration starting 1 February 2027. The direction is unmistakable: small and mid-sized hotels, serviced apartments and boutique resorts are no longer outside the scope. They are inside it.
Tip: Do not wait for the ZATCA notification to start. The window between notification and your integration date gets consumed entirely by procurement, configuration and training. Begin technical evaluation at least six months earlier, and reserve four full weeks of that period purely for testing hospitality-specific invoice scenarios.
This is where the most expensive mistakes happen. Many hotels buy an e-invoicing solution built for shops and restaurants, then discover it does not understand hospitality logic. A hotel invoice is not a single point-of-sale transaction. It is an open account that stretches across days and changes constantly.
A system that passes a ZATCA test on a simple retail sale can fail completely on its first extended stay with a split folio and a post-departure credit note. Test the system against your hardest scenarios, never your easiest ones.
On paper, tax compliance belongs to the finance director and system selection belongs to ownership. Operationally, that is not how it works. The finance director defines what must appear on the invoice. The IT manager guarantees the system can actually produce it, transmit it, store it and protect it. When integration breaks at 11 PM on a Thursday, nobody else gets the call.
The IT manager's real scope in this file includes: evaluating the vendor's technical architecture, reviewing service level agreements, designing role-based access control, managing backup and recovery, verifying where data is hosted, ensuring business continuity when connectivity to Fatoora drops, and documenting all of it for future audit.
Use this as a live evaluation tool during the vendor demo. Ask for proof on screen, not a promise on a slide.
Note: Compliance is not a permanent certificate. ZATCA specifications are updated periodically, and a vendor without a disciplined release cycle will leave you behind the standard within a year. Ask directly: how many times did you ship a regulatory update in the last 12 months, and what was the average time from specification change to production release?
Tax compliance gets attention because it has a deadline and a fine. Hotel data security gets ignored until the incident happens. The irony is that a hotel holds one of the most sensitive data combinations in any industry: full name, national ID or passport number, nationality, mobile number, email, arrival and departure dates, stay preferences and payment details. A breach here does not only cost money. It damages guest trust and property reputation in a market where reviews travel instantly.
Reality check: The most common vulnerability in Saudi hotels is not an exotic exploit. It is one shared front-desk account used by four staff members, with the password written on a sticky note under the keyboard. No firewall fixes that. Eliminate shared accounts before you buy a single new security tool.
Many properties in the Kingdom still run a system installed on a server in the back office. The table below compares the two models specifically through the lens of compliance and security, not features.
| Criterion | Legacy on-premise system | Modern compliant cloud PMS |
|---|---|---|
| ZATCA specification updates | Manual, requires an engineer visit and downtime | Central and automatic across all properties |
| Fatoora integration | Usually via an extra third-party middleware layer | Native inside the billing cycle |
| Backup reliability | Depends on staff discipline | Automated and geographically redundant |
| Fire, theft or hardware failure | Potential total data loss | No impact on data availability |
| Multi-property management | Separate installations, fragmented reporting | Single dashboard, consolidated reporting |
| Access control and audit | Often basic, logs easy to overwrite | Granular roles, immutable logs, MFA |
| Cost model | High upfront capital plus maintenance | Predictable operating subscription |
| Offline operation | Runs locally but cannot report to ZATCA | Temporary local mode with automatic sync |
The conclusion is not that cloud always wins. It is that the decisive difference is who carries the burden of regulatory change. In the on-premise model, your internal team carries it. In the cloud model, the vendor carries it, provided the vendor is a hospitality specialist operating in the Saudi market rather than a generic software company that bolted on a hotel module.
The majority of revenue comes from corporate and government contracts, which means standard tax invoices requiring real-time clearance and valid VAT registration numbers. The recurring failure here is entering the buyer VAT number manually at checkout, producing rejected or incorrect invoices. The fix is structural: bind the VAT number to the company profile once, with automatic format validation at entry and a block on checkout if the field is missing.
Exceptional operational density: hundreds of check-ins and check-outs compressed into a few hours, with large groups arriving through tour operators. The system must support group and batch invoicing, split billing between operator and pilgrim, and hold performance under load. A few seconds of latency per invoice multiplies into a lobby queue that takes hours to clear.
Long stays, monthly contracts and instalment payments. The challenge is correct tax treatment of recurring invoices and auto-renewals, plus the ability to issue a clean credit note when a contract terminates early. Generic retail invoicing tools rarely handle recurring hospitality billing without manual workarounds.
Revenue is spread across restaurants, activities, tours and equipment rental. Every outlet is an independent point of sale that must flow into a unified guest folio under the same tax treatment. Disconnected POS terminals are the single most common cause of month-end mismatches between operational reports and tax filings.
Evidence from the field: When Fandaqah teams review rejected or non-compliant invoices across hotel properties, three causes dominate: incomplete buyer tax data on corporate invoices, date and time formatting errors, and broken invoice sequencing after a backup restore. All three are configuration failures rather than software failures, and all three are preventable with mandatory validation at the point of data entry.
Tourism and hospitality are central pillars of Saudi Vision 2030. As giga-projects come online and room inventory expands across the Kingdom, pressure on hotel technology infrastructure increases rather than eases. The trends a hotel IT manager should be preparing for now:
The practical implication is straightforward. The system you choose today will not be judged only on whether it meets today's requirements. It will be judged on whether it can absorb requirements that have not been published yet. Adaptability matters more than the current feature list.
Phase 2 integration is enforced in waves based on VAT-taxable revenue, and ZATCA notifies targeted taxpayers in advance. With thresholds dropping to SAR 187,500 in the twenty-fifth wave, most hotel businesses are either already in scope or approaching it. The definitive source is the notification issued to your specific establishment through the Fatoora portal.
A simplified invoice is typically issued to an individual guest and must be reported to ZATCA within 24 hours of issuance. A standard tax invoice is issued to legal entities such as corporates and travel agencies, requires the buyer's details and VAT registration number, and must be cleared by ZATCA in real time before it is delivered to the buyer.
Technically yes, but it creates a gap between where the transaction originates, at the front desk and the outlets, and where the invoice is issued. That gap is usually filled with manual export and import, which is the largest single source of errors and the weakest point in any audit trail. Direct PMS-to-invoicing integration costs less over a three-year horizon in almost every case we see.
The system should continue issuing invoices locally with correct storage and sequencing, then transmit them automatically once connectivity is restored within the permitted window. Ask the vendor to demonstrate this scenario live during evaluation rather than describing it in a document.
In-Kingdom hosting is strongly preferred because it simplifies PDPL compliance and reduces cross-border transfer complexity. Request written disclosure from the vendor covering data centre locations, backup locations, and any third-party sub-processors handling guest data.
It depends on property size and the cleanliness of legacy data. Typical ranges run from around two weeks for a small property to six to eight weeks for a multi-property group. The longest phase is rarely installation. It is cleaning historical data and training the teams who will use the system every day.
A full inventory: which systems are running, where data is stored, who has access, and exactly how an invoice is produced step by step today. You cannot evaluate alternatives before documenting the current state, because most gaps surface in that inventory rather than in vendor demonstrations.
No. Compliance and security overlap but are not the same. ZATCA requirements address invoice integrity, tamper resistance and reporting. They do not cover phishing resistance, endpoint protection, network segmentation, vendor risk or breach response. A fully compliant hotel can still suffer a serious guest data breach.
Choosing a secure and ZATCA-compliant hotel system is not a compliance project with an end date. It is an infrastructure decision that will shape your property's operations for years. Any IT manager who treats it as a temporary exercise will be repeating the entire process within two years at a higher cost and under more pressure.
The winning formula is simple to state and demanding to execute: a system that proves compliance in practice rather than on paper, protects guest data in line with Saudi regulatory frameworks, understands hospitality logic from the open folio through to credit notes, and is backed by a vendor capable of keeping pace with regulatory change. Vendors meeting all four deserve serious evaluation. Vendors meeting some of them will show you their real cost later, not in the quotation.
Ready to assess your hotel's compliance readiness? At Fandaqah.com we help hotel IT managers across the Kingdom audit their current systems, close compliance and security gaps, and migrate to a hotel management platform built for ZATCA e-invoicing and the realities of Saudi hospitality operations. Book a free demo at Fandaqah.com and receive the complete compliance checklist for your property.
Tags: ZATCA-compliant hotel systems, hotel property management system, e-invoicing for hotels Saudi Arabia, ZATCA Phase 2 integration, Fatoora platform integration, hotel data security, guest data protection, PDPL compliance, NCA Essential Cybersecurity Controls, PCI DSS hotels, hotel IT manager, cloud PMS Saudi Arabia, hospitality technology, Saudi Vision 2030, Fandaqah
This content is provided for general guidance only and does not constitute tax or legal advice. Always refer to the official guidance published by the Zakat, Tax and Customs Authority and other competent Saudi regulators to confirm the requirements that apply to your establishment.
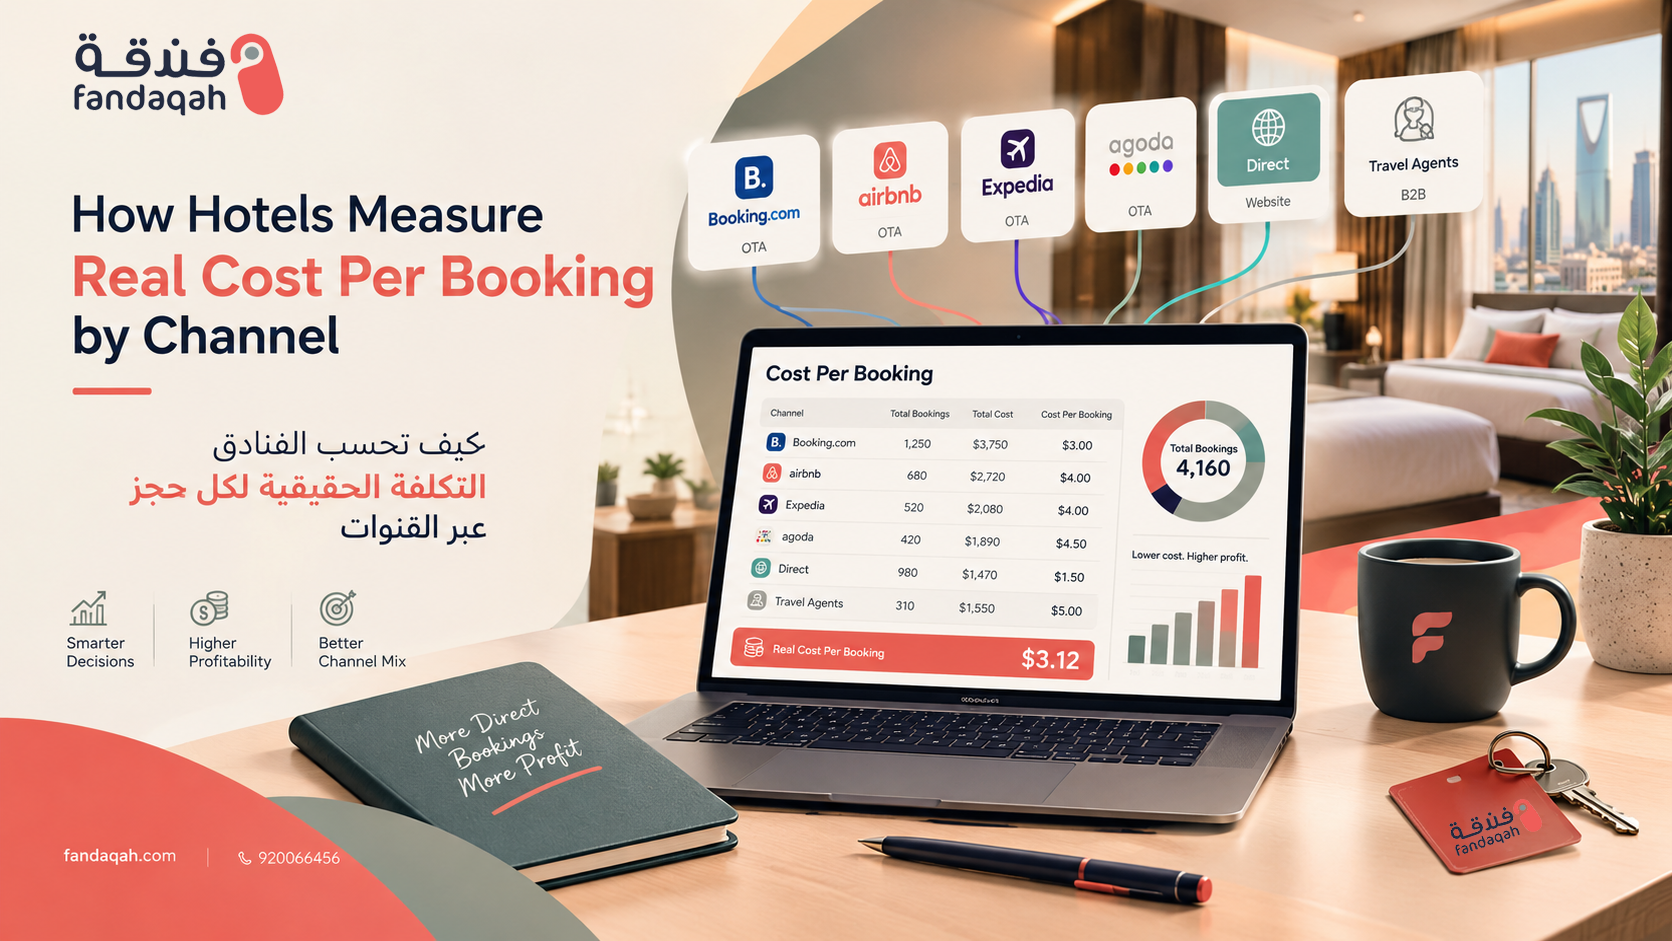
Calculate true hotel cost per booking across OTA, direct, GDS & WhatsApp. Step-by-step formula, Riyadh example & ways to cut distribution costs in Saudi Arabia....
How WhatsApp hotel booking, AI assistants & in-chat payments turn guest chats into direct reservations. Build a commission-free channel for Saudi hotels....
Learn how to calculate the true cost of a hotel stay in Saudi Arabia. Discover when breakfast and parking are worth it, how to get room upgrades, and when flexible rates save you money....
Learn how Saudi hotel groups standardize rates, operations and reporting across properties with a multi-property PMS, shared KPIs and scalable processes....
Discover the practical signs a growing hotel group has outgrown separate systems and should switch to a multi-property PMS for better control, reporting, and scale in Saudi Arabia....
Learn how multi-property hotels in Saudi Arabia stop duplicate guest and reservation records with a centralized PMS, smart matching, channel sync, and data governance....
Complete guide to hotel food & beverage manager duties, food cost control, menu engineering, and how POS–PMS integration cuts waste and boosts profit in Saudi hotels....
Discover how a hotel PMS eliminates double bookings, wrong room assignments, and billing mistakes in Saudi hotels. ZATCA-compliant, real-time, and built for Vision 2030....
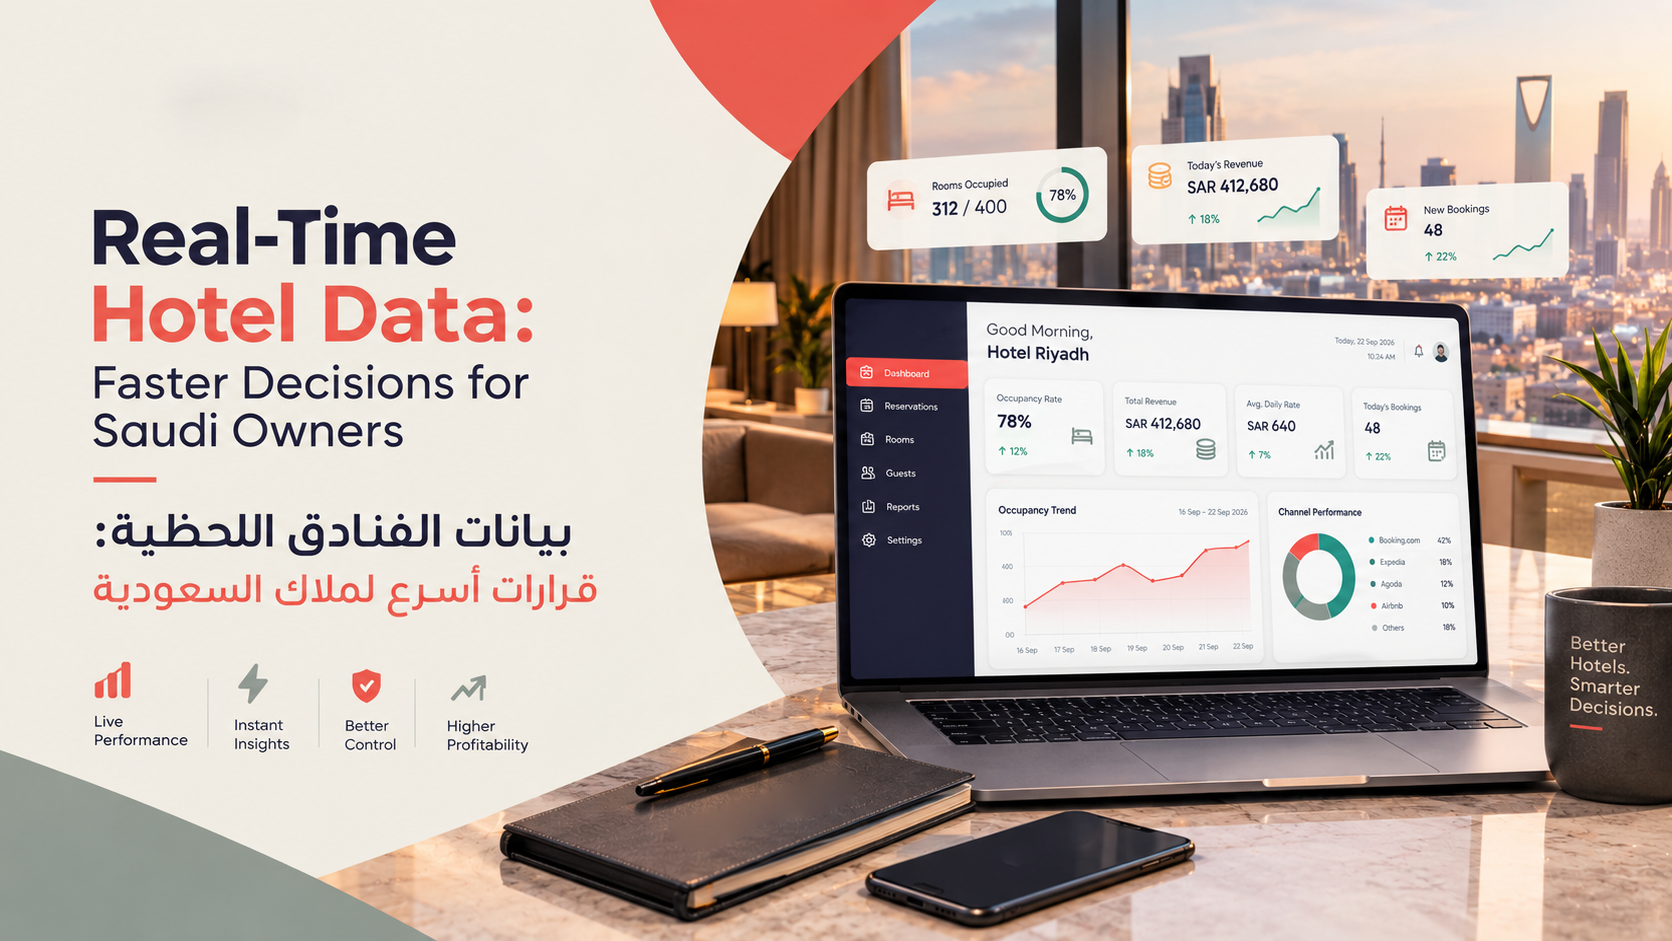
Discover how real-time hotel data helps owners boost RevPAR 5–15%, react to demand in minutes, and stay competitive in Saudi Arabia’s Vision 2030 tourism boom....
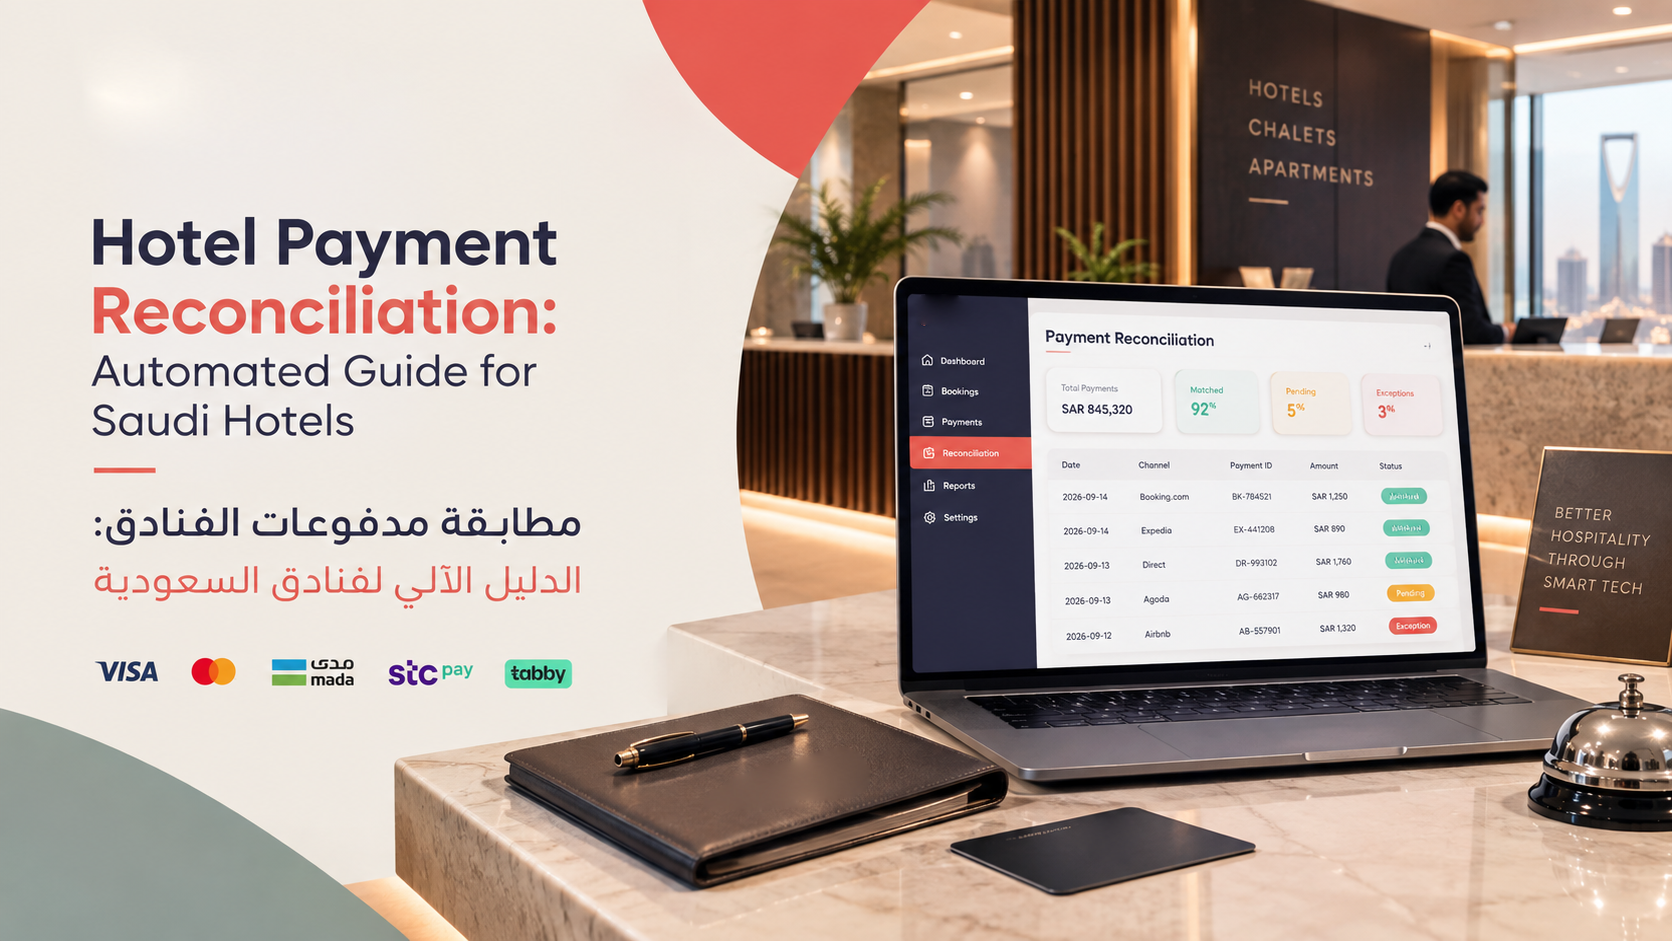
Learn how automated hotel payment reconciliation matches reservations, payments & invoices in real time. Recover revenue, cut time 80–90% & stay ZATCA-ready....
Complete 2026 guide: which payment methods Saudi hotels must offer — Mada, Visa/Mastercard, Apple Pay, Tabby & Tamara — to boost direct bookings and margins....
Learn how Saudi hotel owners can build a single source of truth for property performance. Cut reporting time 70–90%, track RevPAR, ADR & occupancy in real time....
Complete guide to automating hotel night audit in Saudi Arabia: room & tax posting, no-shows, ZATCA Fatoora e-invoicing, payment reconciliation & continuous close....
Discover proven strategies for Saudi hotels to protect revenue in low occupancy: dynamic pricing, RevPAR & TRevPAR focus, direct bookings, ancillary income, staycations & Vision 2030 insights....
A hotel management system (PMS) cuts queues on Saudi National Day 2026 with pre-check-in, auto room assignment, live housekeeping, channel sync and instant e-invoices. Shorter waits, zero overbookings...
Connected hotel technology creates a seamless guest journey for Saudi National Day 2026. Link PMS, booking engine, POS, mobile keys & more—enter data once, zero friction from search to review....
12 proven strategies to increase direct hotel bookings in Saudi Arabia. Grow commission-free revenue with booking engines, WhatsApp, Google Free Booking Links & more in 2026....
Learn proven strategies to reduce OTA commissions, boost direct bookings, and increase hotel profits in Saudi Arabia. Practical tips for Riyadh, Jeddah, Makkah & more in 2026....
How Fandaqah integrates HyperPay, mada, Visa, Apple Pay, Tamara and Tabby for secure direct hotel payments in Saudi Arabia — with ZATCA invoicing built in....
Practical guide to MOT-compliant hotel PMS in Saudi Arabia. Cover NTMP reporting, guest registration, Baladi licences, ZATCA invoicing and how Fandaqah helps....
The 10 essential daily hotel reports every general manager should review before 10 a.m.: flash, night audit, ADR & RevPAR, pace, room status, and more — with red flags to watch....
Discover how a hotel PMS cuts front-desk check-in and billing errors with live room status, channel sync, auto POS posting, and ZATCA e-invoicing for Saudi properties....
How hotel sales managers in Saudi Arabia win corporate rate agreements and MICE contracts. Practical RFP tips, smart pricing, account targeting and sales KPIs....
Discover the hotel food and beverage manager’s real duties, key KPIs (food cost %, average check, waste), and how POS-PMS integration cuts costs and raises profit in Saudi hotels....
Learn what a hotel revenue manager does daily, the KPIs that matter (RevPAR, ADR, GOPPAR), and 8 practical ways to use a PMS to raise profits in the Saudi market....
Design a frictionless guest journey in 7 stages. Map friction points, apply 5 principles, cut check-in time, and connect bookings to billing with one PMS. Practical guide for Saudi hotels and serviced...
Turn PMS data into personalized stays for repeat guests. 5-step framework: unify profiles, segment, tag preferences, activate at 3 moments, and measure results. Built for Saudi hotels & serviced apart...
Is your hotel battling rising chargebacks? Discover why chargebacks are eating into hotel revenue and learn essential strategies to prevent, dispute, and protect your bottom line from fraudulent claim...
By 2030, hotel payment landscapes will be unrecognizable. Explore how biometrics, digital wallets, and blockchain are set to redefine the guest experience, moving beyond traditional cards and cash for...
Prevent payment collection errors and streamline your hotel's end-of-day operations. Discover expert strategies, technology solutions, and best practices to ensure accurate financial reconciliation an...
Unlock hotel success with key performance indicators. Learn the essential metrics like RevPAR, ADR, Occupancy, GOPPAR, and more that every hotel manager needs to master for profitability and growth....
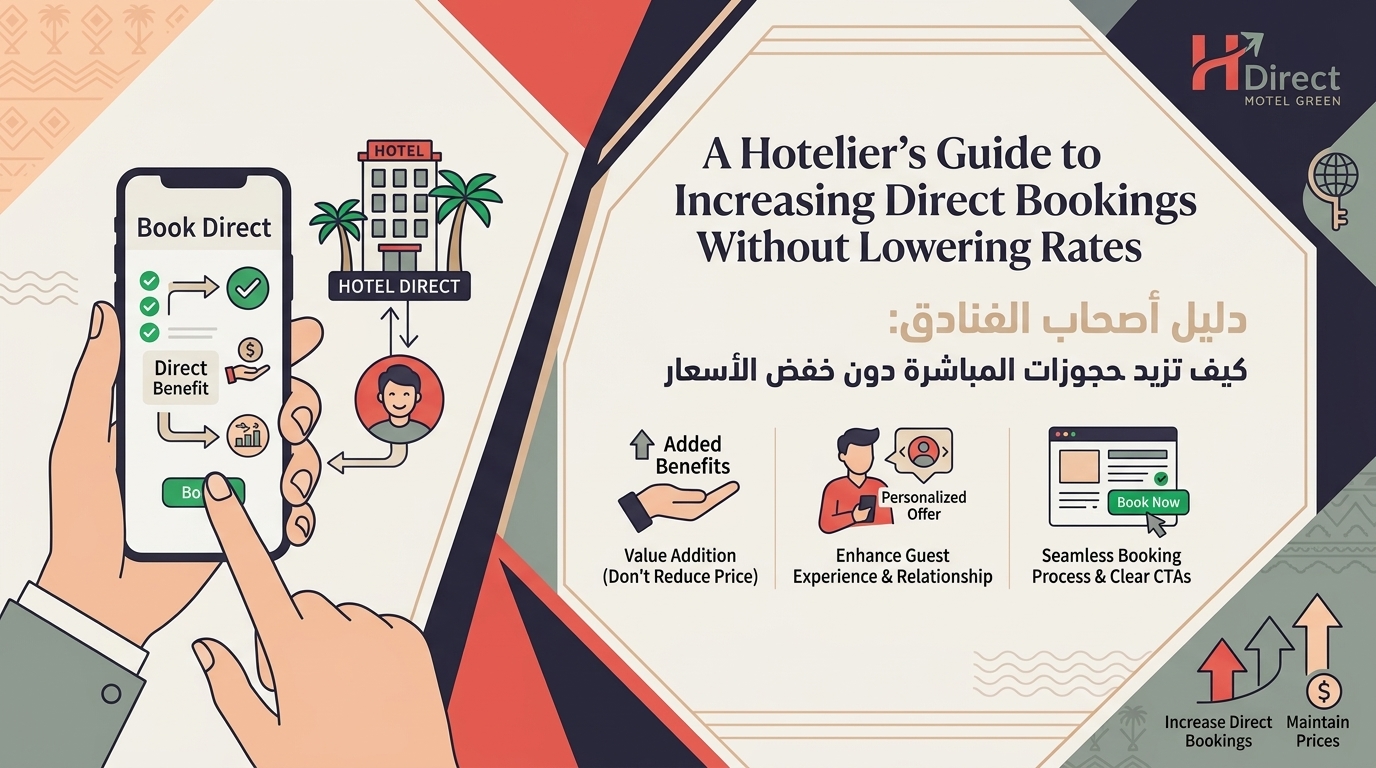
Unlock the secrets to boosting your hotel's direct bookings. This expert guide provides actionable strategies, from enhancing your online presence to personalizing guest experiences, all without compr...
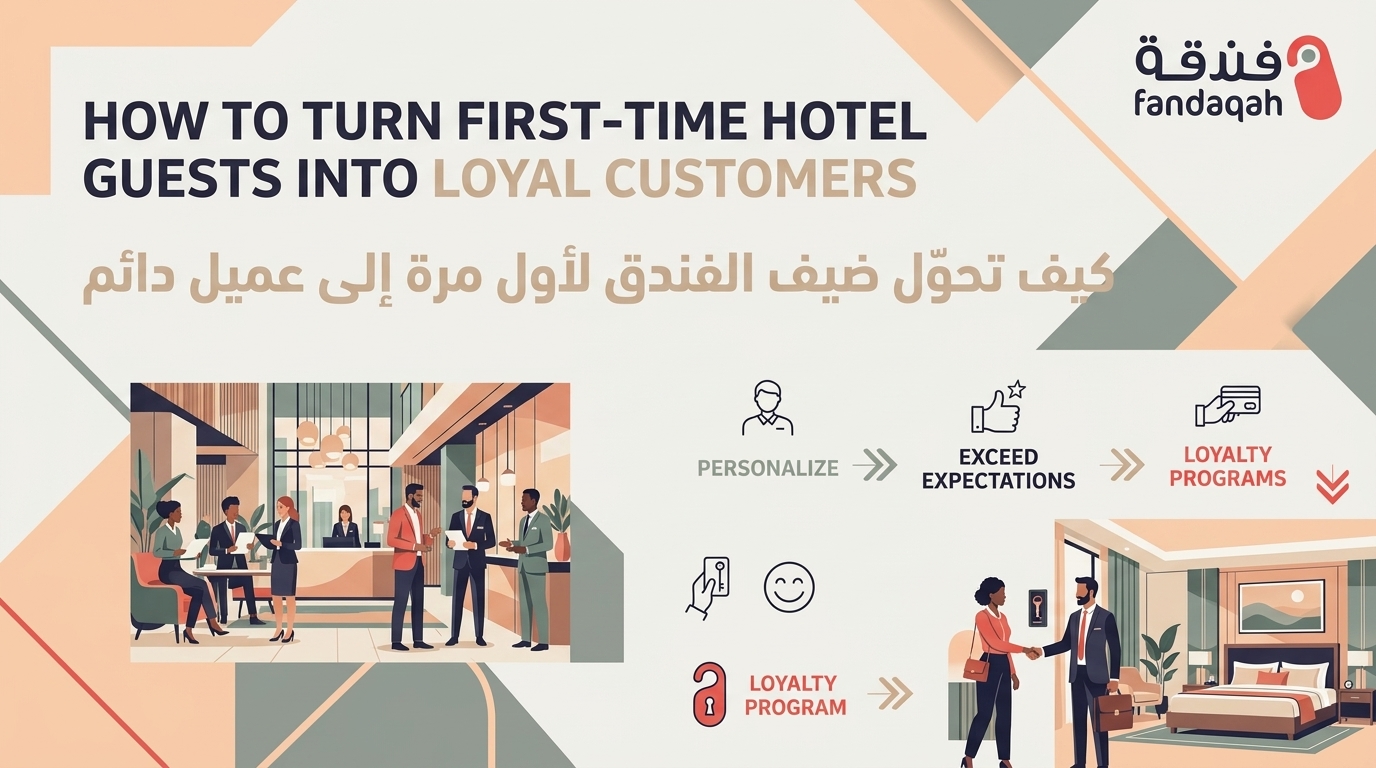
Unlock the secrets to transforming first-time hotel guests into lifelong advocates. Discover actionable strategies for exceptional service, personalized experiences, and powerful loyalty programs that...
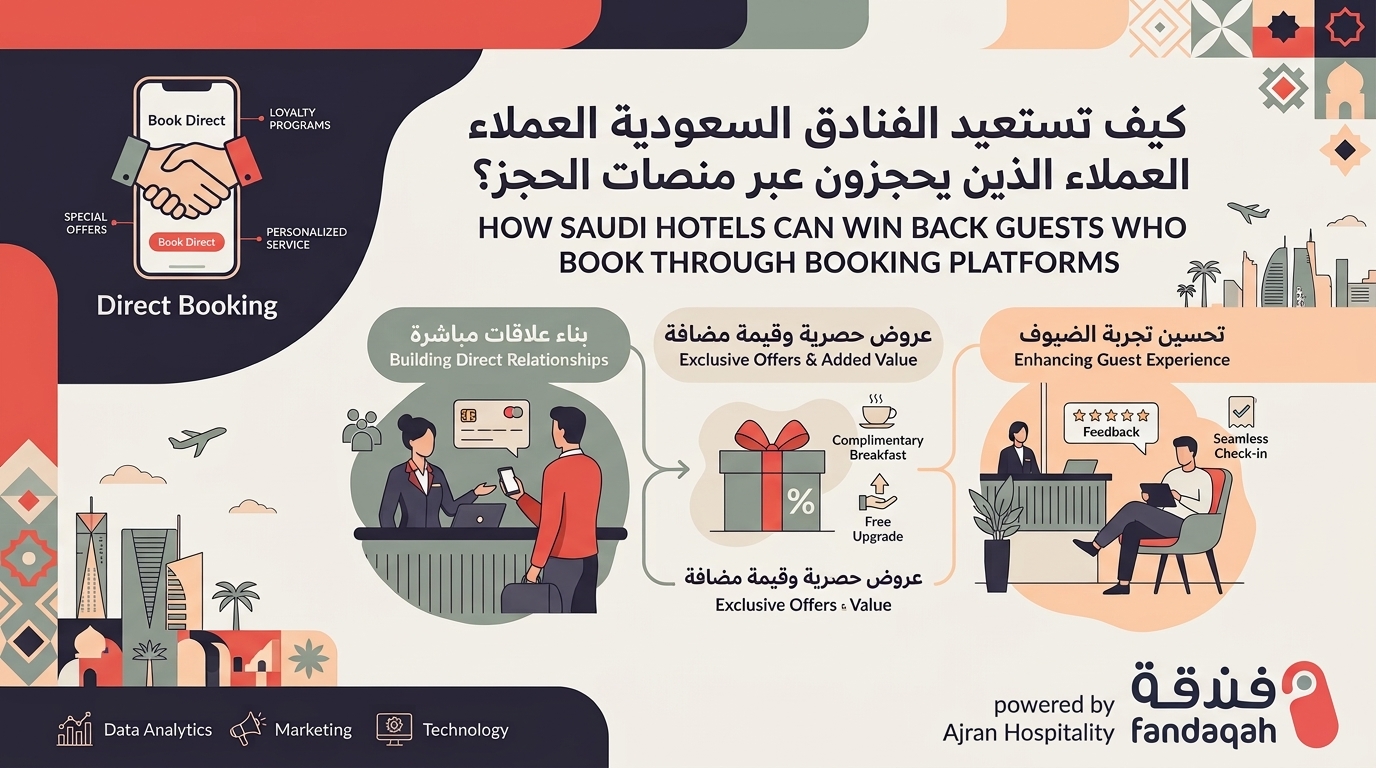
Saudi hotels can reclaim direct bookings from OTAs. Discover expert strategies to enhance guest loyalty, personalize experiences, optimize your online presence, and drive repeat business directly to y...
Discover why hotel guests will increasingly choose WhatsApp over traditional phone calls by 2026. Explore the convenience, efficiency, and personalized communication driving this digital shift in hosp...
Uncover the top reasons guests abandon hotel bookings before payment and learn expert strategies to reduce cart abandonment, boost conversions, and maximize revenue....
Prepare for the future of hospitality in Saudi Arabia. Discover the top 10 trends poised to shape hotel revenue in 2027, from AI integration to sustainable tourism, and learn how to optimize your stra...
Unlock the untapped revenue potential hidden within your hotel rooms. Discover expert strategies, from personalized upsells to smart technology, to maximize profitability and guest satisfaction withou...
Uncover the unique motivations behind Saudi guests' hotel reviews and the cultural nuances that drive virality. Learn how hospitality businesses can leverage these insights for unparalleled guest enga...
Explore the transformative impact of Instagrammable design on Saudi Arabia's burgeoning hospitality sector. Discover how aesthetics, technology, and cultural narratives are driving unprecedented growt...
Explore the future of hospitality in Saudi Arabia. Discover how AI, robotics, and hyper-personalization will transform Saudi hotels by 2030, offering unparalleled luxury and efficiency. ...
Maximize your hotel's profitability. Discover the strategic moments to raise your room rates and crucial times when lowering prices can be a costly mistake. Learn to optimize your pricing strategy fo...
Saudi Arabia's ambitious mega-projects like NEOM, Red Sea Project, and Qiddiya are set to revolutionize global tourism and hotel booking. Discover how these futuristic developments will reshape travel...
Maximize summer hotel revenue in Saudi Arabia with dynamic pricing, family packages, staffing tips & operations best practices. Align with Vision 2030 for higher RevPAR and guest satisfaction....
Master Umrah seasonal occupancy with dynamic pricing, packages, loyalty programs & Fandaqah.com. Strategies to boost RevPAR in Ramadan peaks and fill rooms in low seasons....
Unlock the power of guest data to craft unforgettable, personalized hotel experiences. Learn strategies to collect, analyze, and apply insights for enhanced loyalty and revenue. ...
Unlock the power of domestic tourism in Saudi Arabia. Discover expert strategies for hotels to transform local guests into loyal, repeat customers, driving sustainable growth in this dynamic market. ...
Unlock the secrets to converting TikTok views into bookings for Saudi hotels. Discover expert strategies, content types, and measurement techniques to maximize your social media ROI in the Kingdom's d...
Explore how AI is revolutionizing hotel guest experiences in Saudi Arabia. From personalized service to smart rooms, discover the future of hospitality in the Kingdom. ...
Learn how to manage AlUla hotel bookings in this emerging cultural destination. Best times, prices, accommodation types & tips for Hegra, Winter at Tantora. Compare on Fandaqah.com....
Discover how The Red Sea Project, AMAALA & Sindalah prepare Saudi hotels for global luxury standards. Sustainability, AI tech, Vision 2030 & top resorts reviewed on Fandaqah.com....
Discover effective Saudi National Day hotel offers, staycation packages, and campaigns. Boost occupancy with family deals, luxury experiences, and Vision 2030-aligned promotions across Riyadh, Jeddah ...
Proven strategies to boost weekend occupancy in Saudi secondary cities. Packages, social media, local partnerships & Vision 2030 tips for hotels in Abha, Taif, AlUla & more....
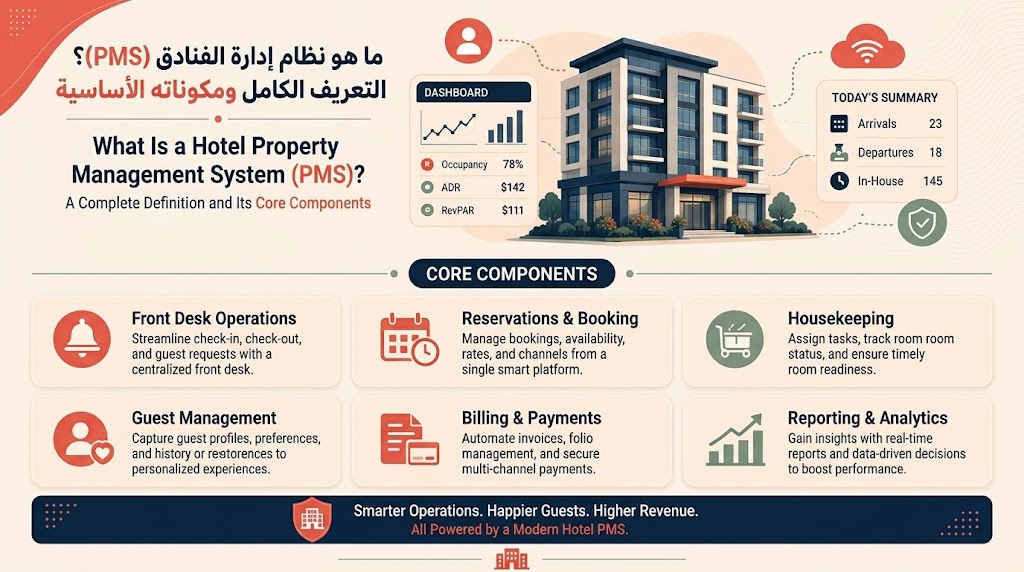
A Hotel PMS is the central software for managing reservations, rooms, guests, check-in/out, billing & reporting. Learn core components, benefits & how Saudi hotels can choose the right system....
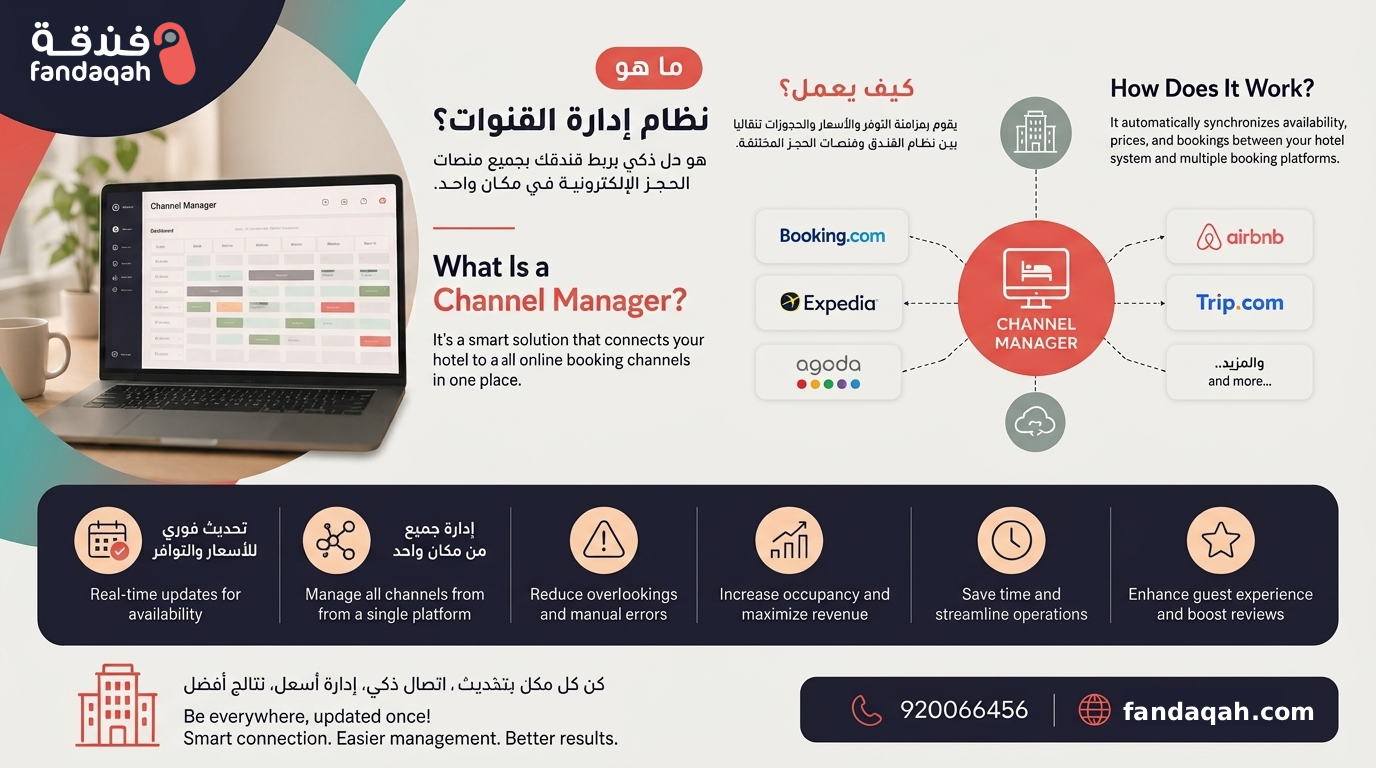
A hotel Channel Manager syncs rates, availability & reservations across OTAs from one place. Learn how it cuts overbooking risk, saves time & boosts distribution for Saudi hotels....
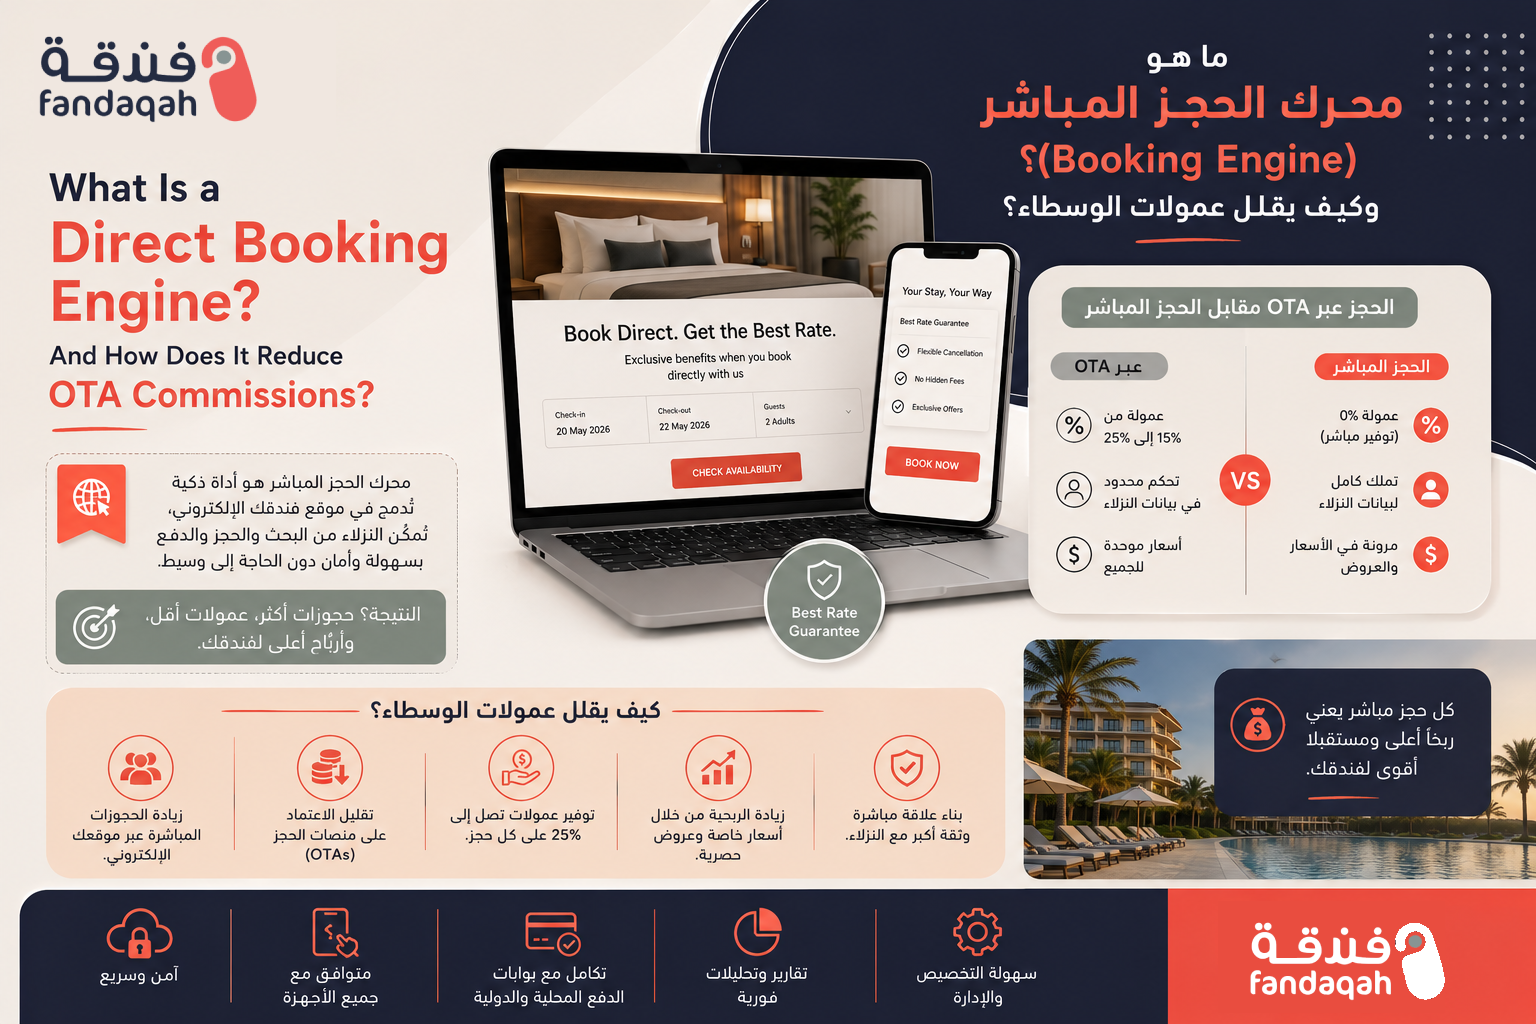
Learn what a direct booking engine is and how Saudi hotels can use it to cut OTA commissions by 15–25%, own guest data, boost direct revenue, and improve profitability under Vision 2030....
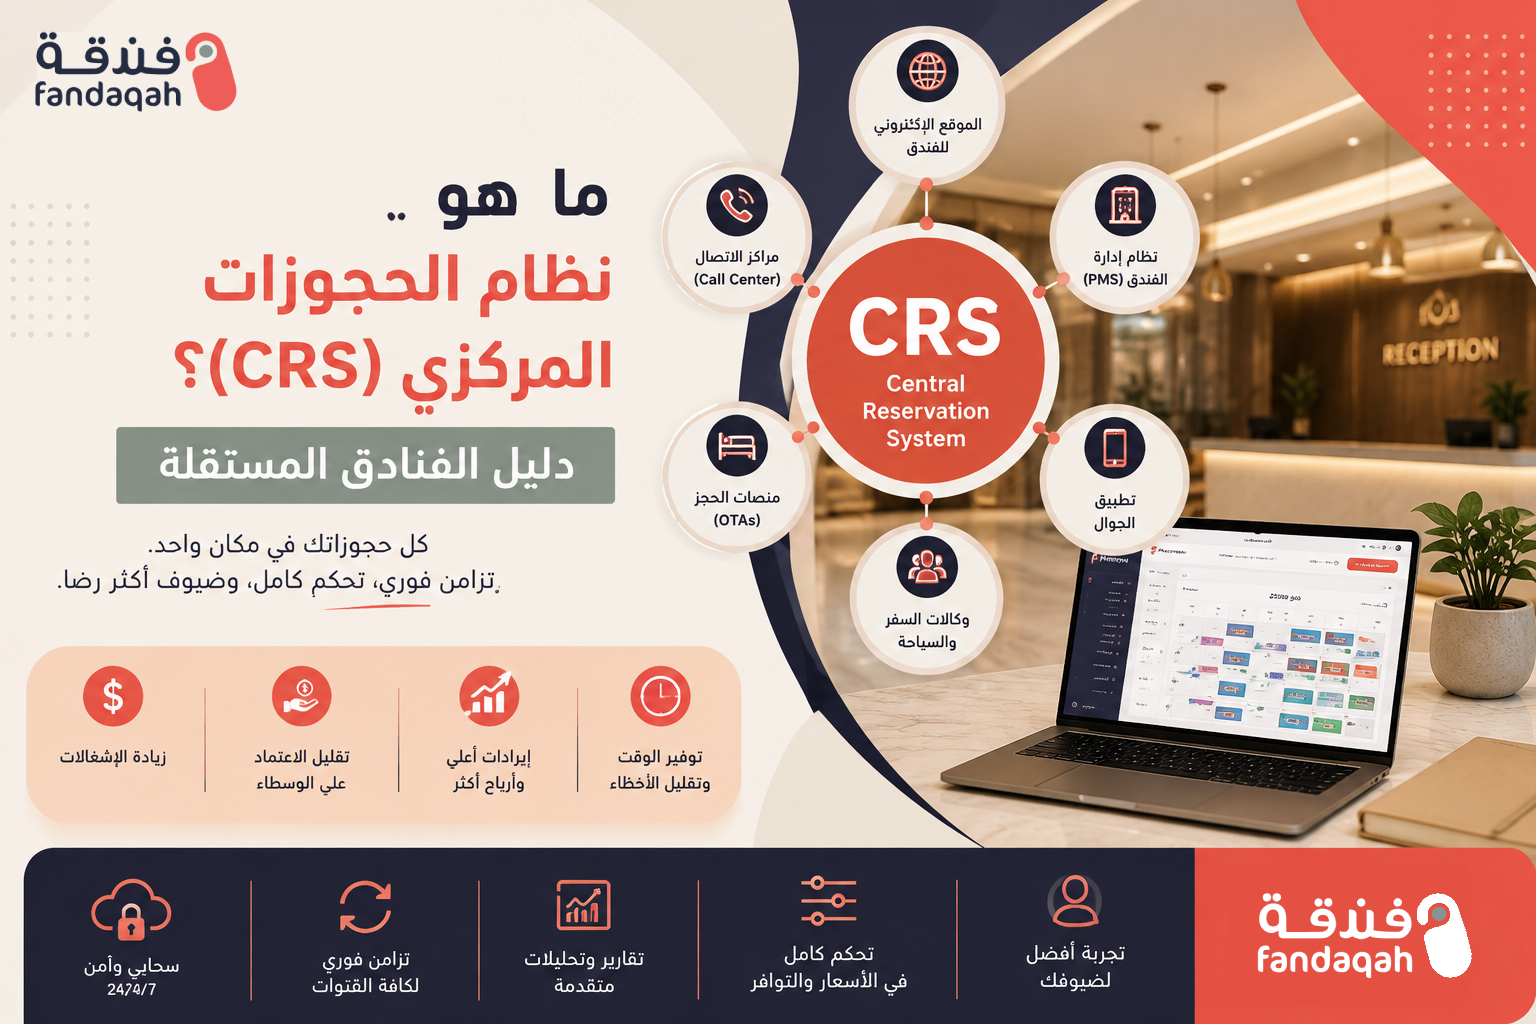
Discover what a Central Reservation System (CRS) is and how independent hotels in Saudi Arabia can use it to prevent overbookings, boost direct bookings, and maximize revenue under Vision 2030....
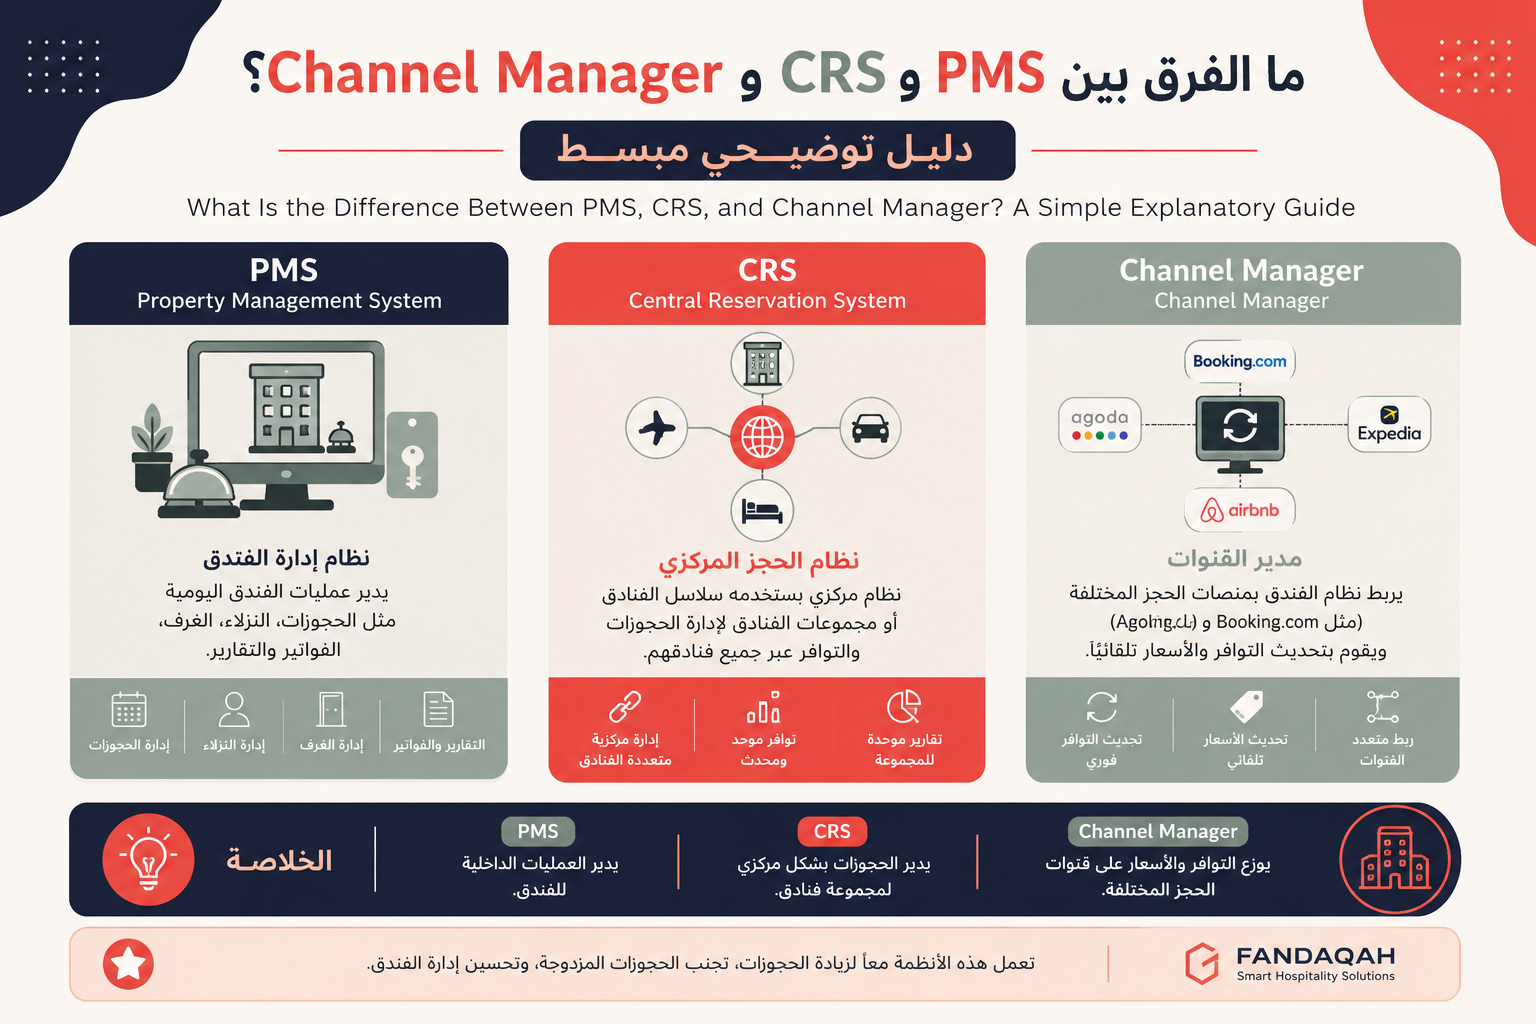
Clear differences between PMS, CRS, and Channel Manager explained. Learn which systems Saudi hotels need for operations, central bookings, and OTA distribution....
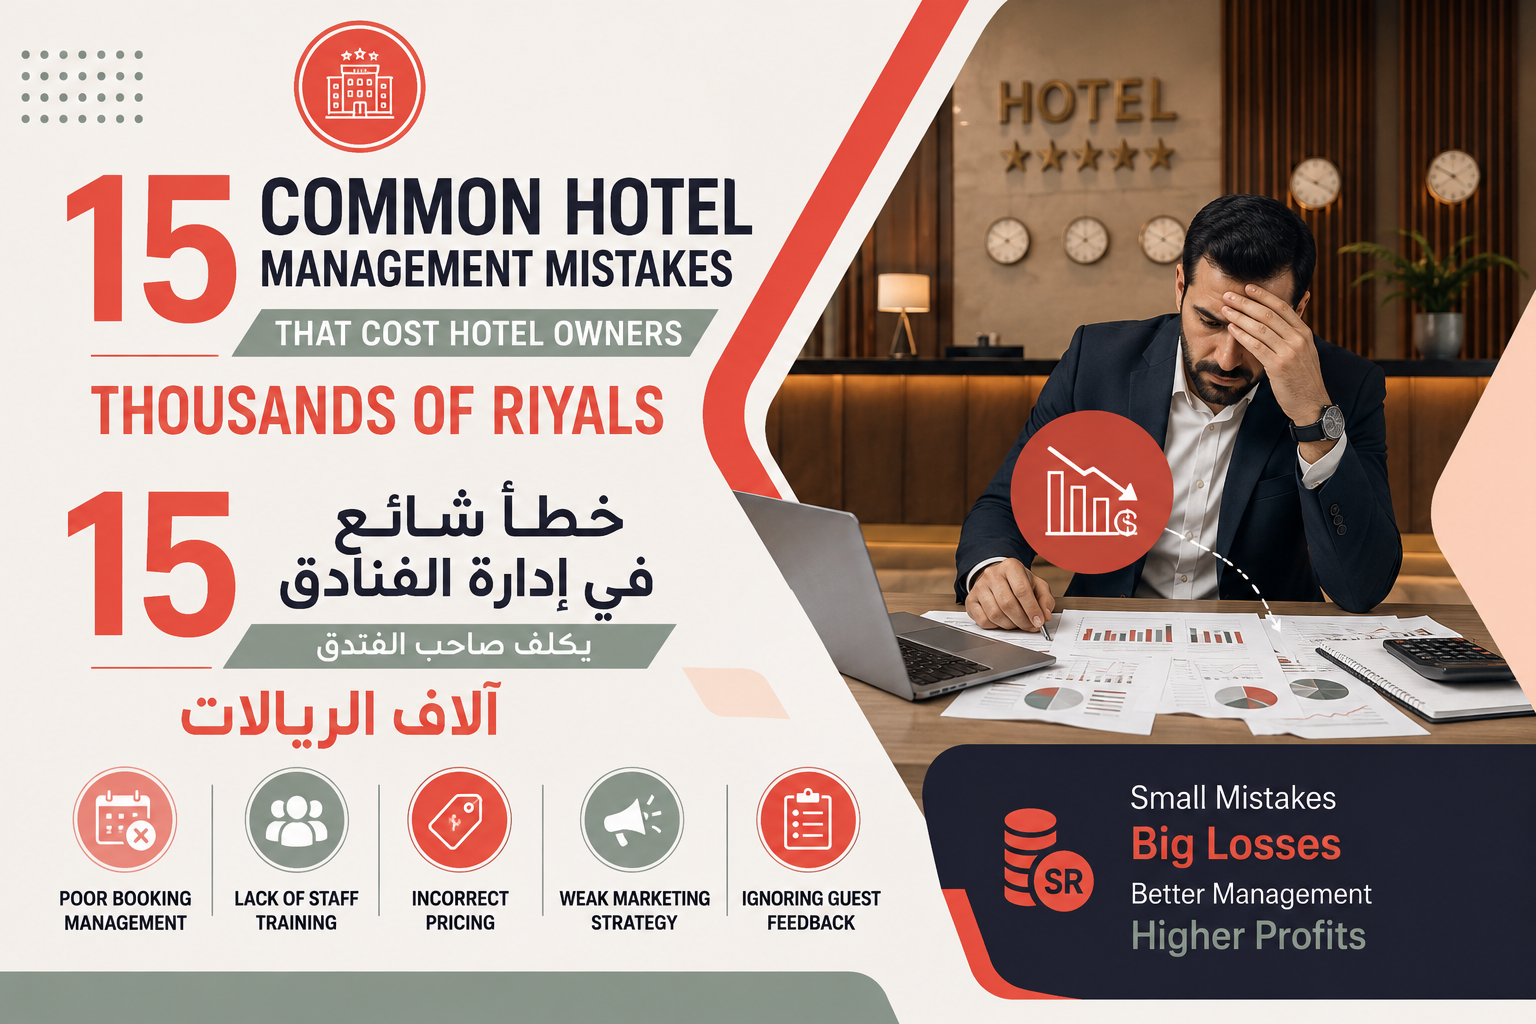
Discover the 15 most common hotel management mistakes draining Saudi hotel revenue. Practical fixes for booking systems, pricing, staff training, reviews & Vision 2030 alignment....
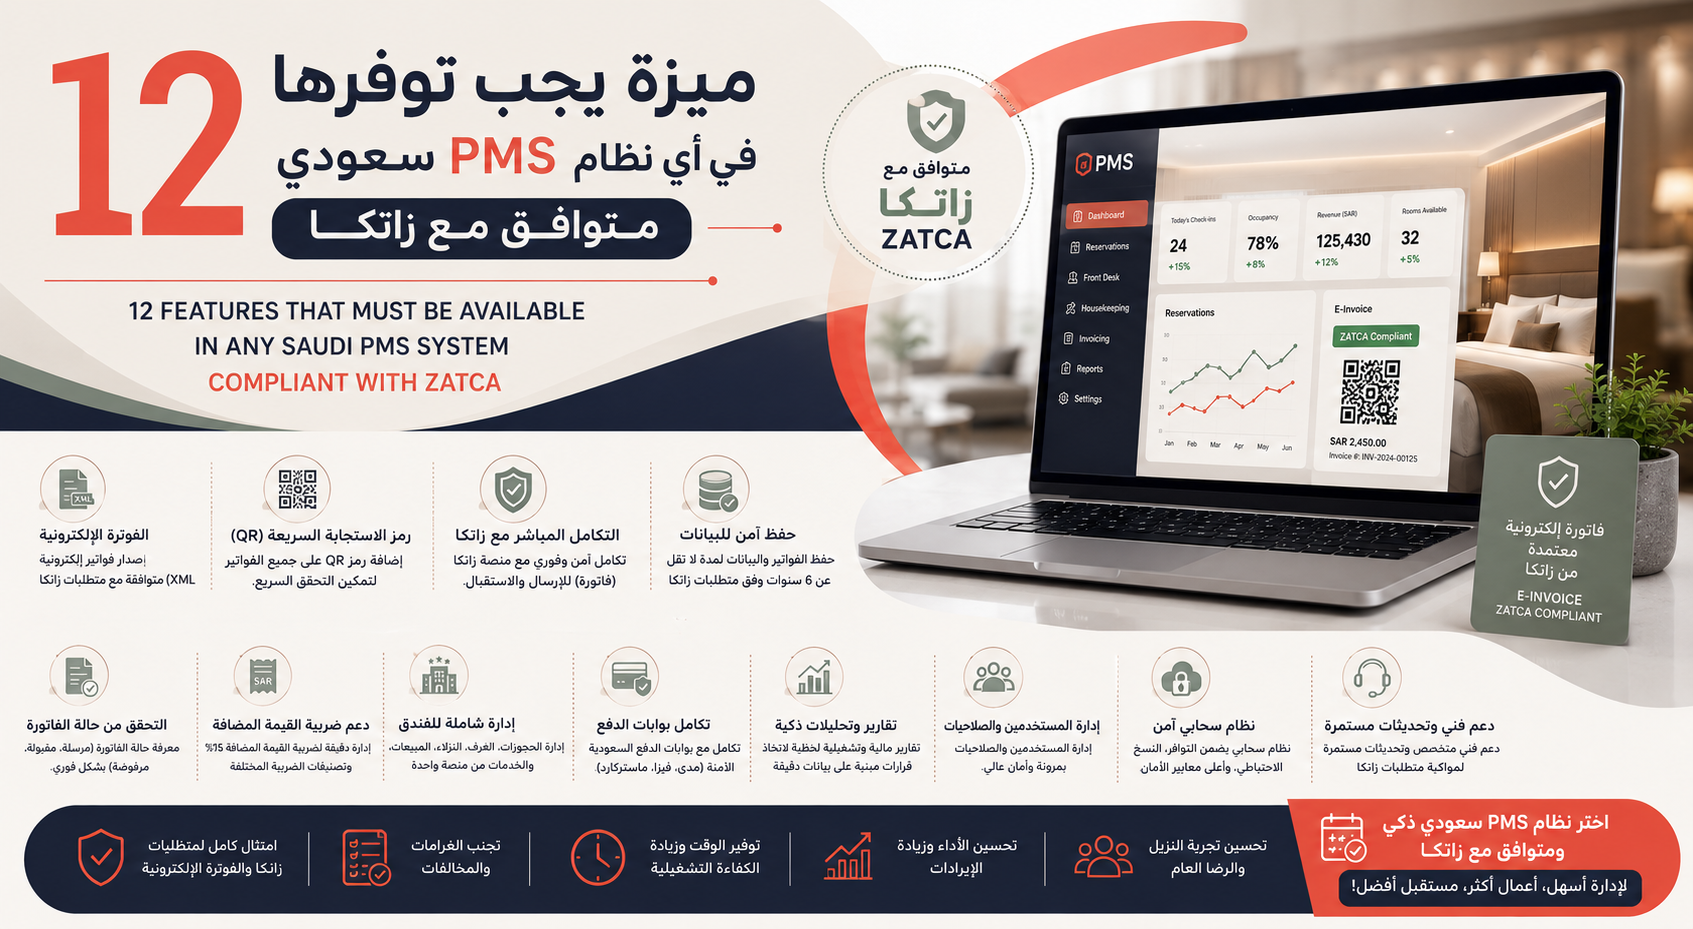
Discover the 12 essential features every Saudi property management system needs for full ZATCA e-invoicing compliance, Fatoora & Ejar integration, and seamless operations....
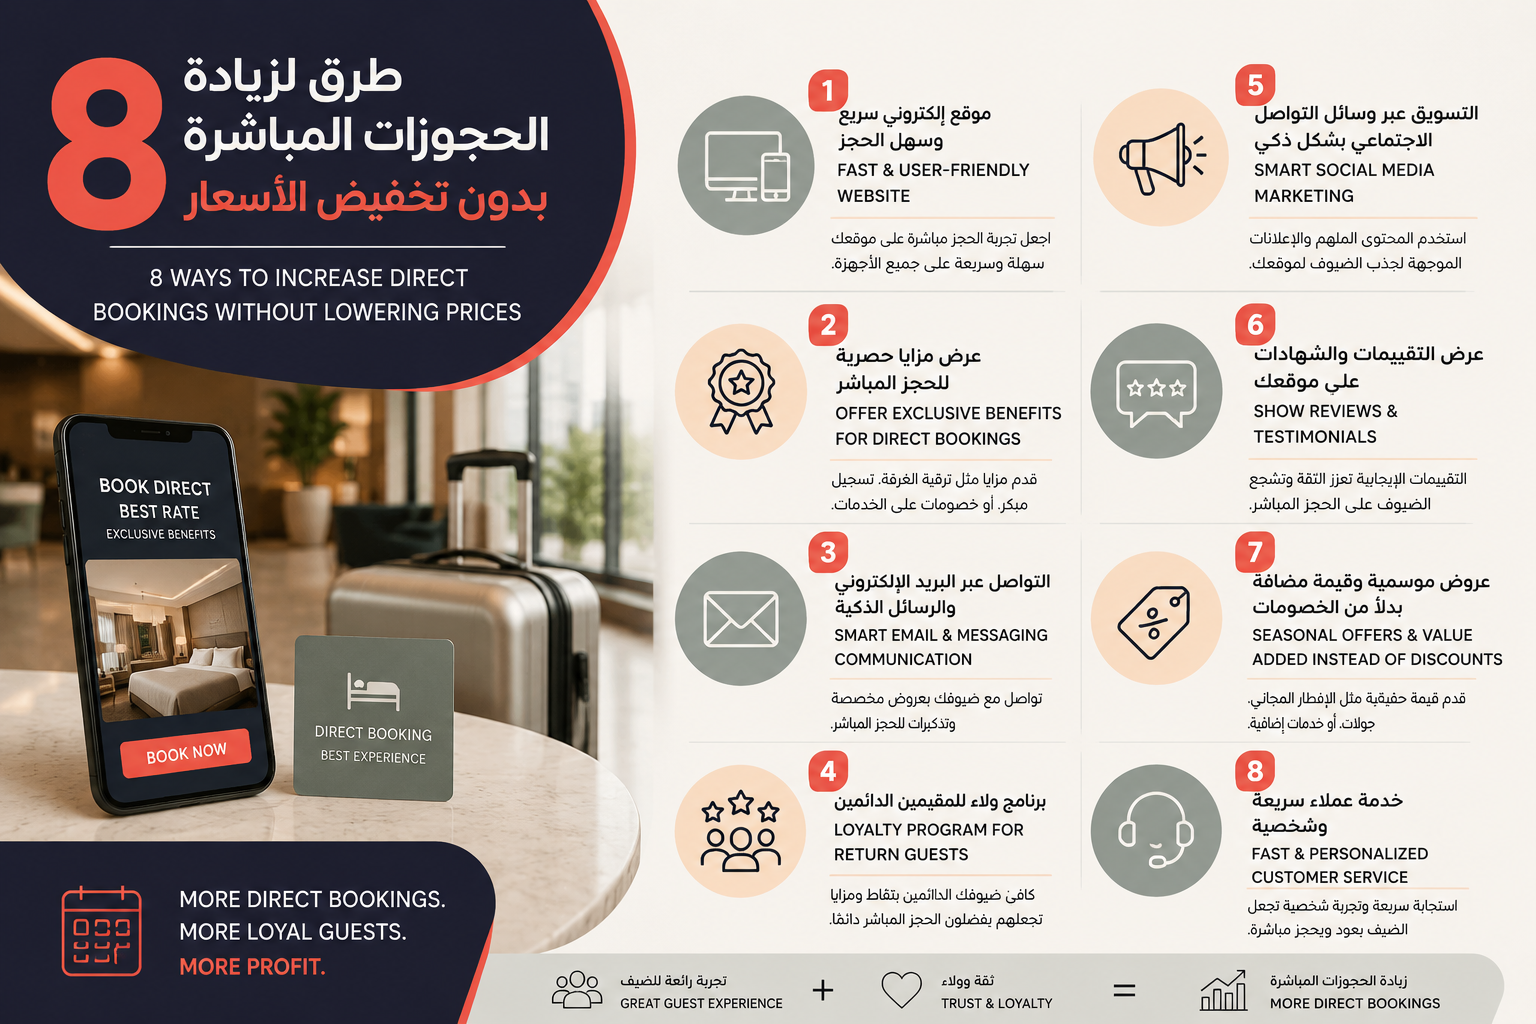
Discover 8 proven strategies for Saudi hotels to increase direct bookings without lowering prices. Optimize your booking engine, loyalty programs & more aligned with Vision 2030....
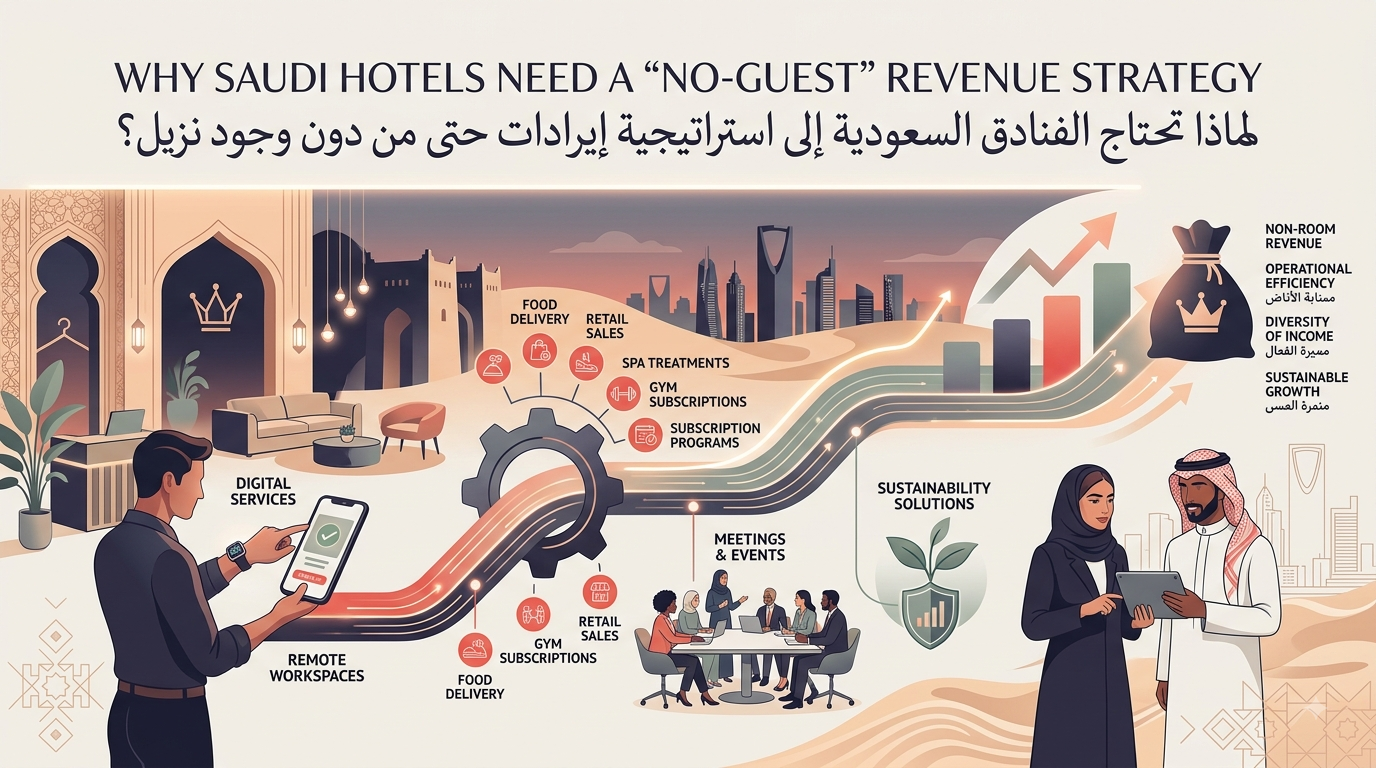
Unlock new profit streams beyond room nights. Discover why Saudi hotels must embrace "no-guest" revenue strategies to enhance profitability, diversify income, and boost guest loyalty in a competitive ...
Discover the ultimate factor influencing Saudi hotel bookings. Learn how online reviews, especially around service and culture, shape guest decisions and why they're crucial for your next stay. ...
Discover how NEOM hotels and Saudi mega projects create huge opportunities for cloud-based hotel management systems. Boost efficiency, guest experience & Vision 2030 readiness....
Explore the battle between Saudi hotels and short-term rentals for today's traveler. Discover which accommodation type offers the best experience, value, and authenticity for your next Saudi adventure...
Learn how hotels manage high demand during Riyadh Season with dynamic pricing, demand forecasting & smart strategies to maximize revenue without losses....
Discover how creating a single, highly photogenic "Instagram Room" can significantly boost hotel revenue through organic social media marketing, enhanced guest experience, and increased bookings. Lear...
How Saudi hotels are gearing up for the 2034 FIFA World Cup: capacity expansion, smart tech, sustainability, and Vision 2030 strategies to deliver world-class hospitality for millions of fans....
Prepare your hotel for Hajj 2027 with modern PMS systems, full Ministry of Hajj & Umrah compliance, and smart capacity management. Boost efficiency, pilgrim experience, and seasonal revenue....
Unlock more bookings without spending more. Discover expert strategies to optimize your hotel's online presence, enhance guest experience, and leverage existing resources for maximum revenue growth. ...
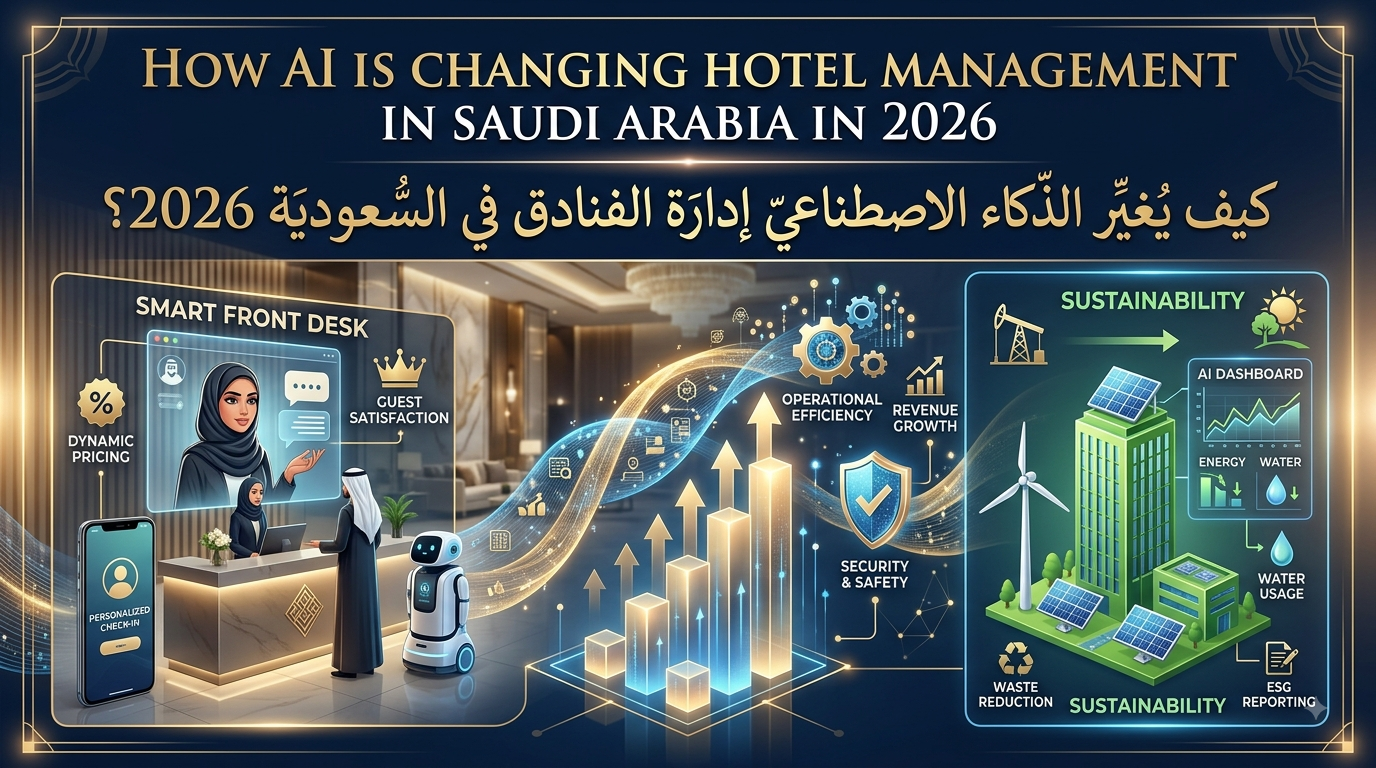
Discover how AI is revolutionizing hotel management in Saudi Arabia by 2026. Explore key trends, applications, and the strategic advantages AI offers in enhancing guest experience, optimizing operatio...
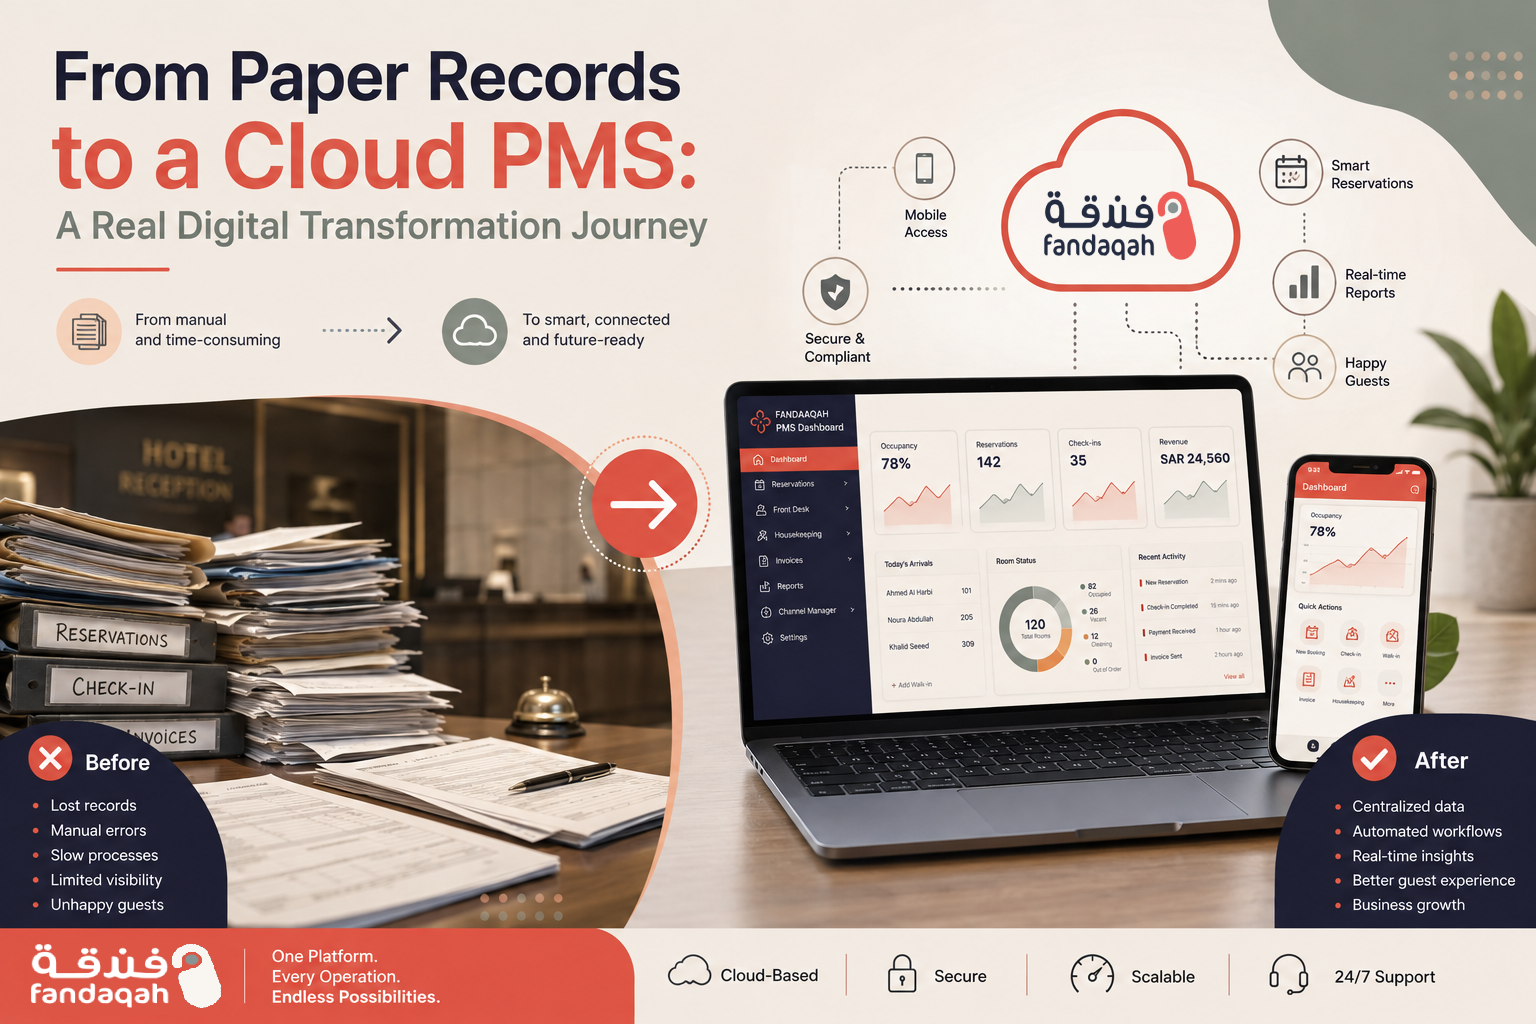
Discover how Saudi hotels move from paper records to a cloud PMS. Boost efficiency, guest experience & align with Vision 2030. Real benefits, comparison & FAQ....
Exclusive interview with Khalid Al-Shahri, Jeddah hotel GM, on how Fandaqah PMS eliminated double bookings, cut check-in to 3 min, and boosted occupancy to 78%....
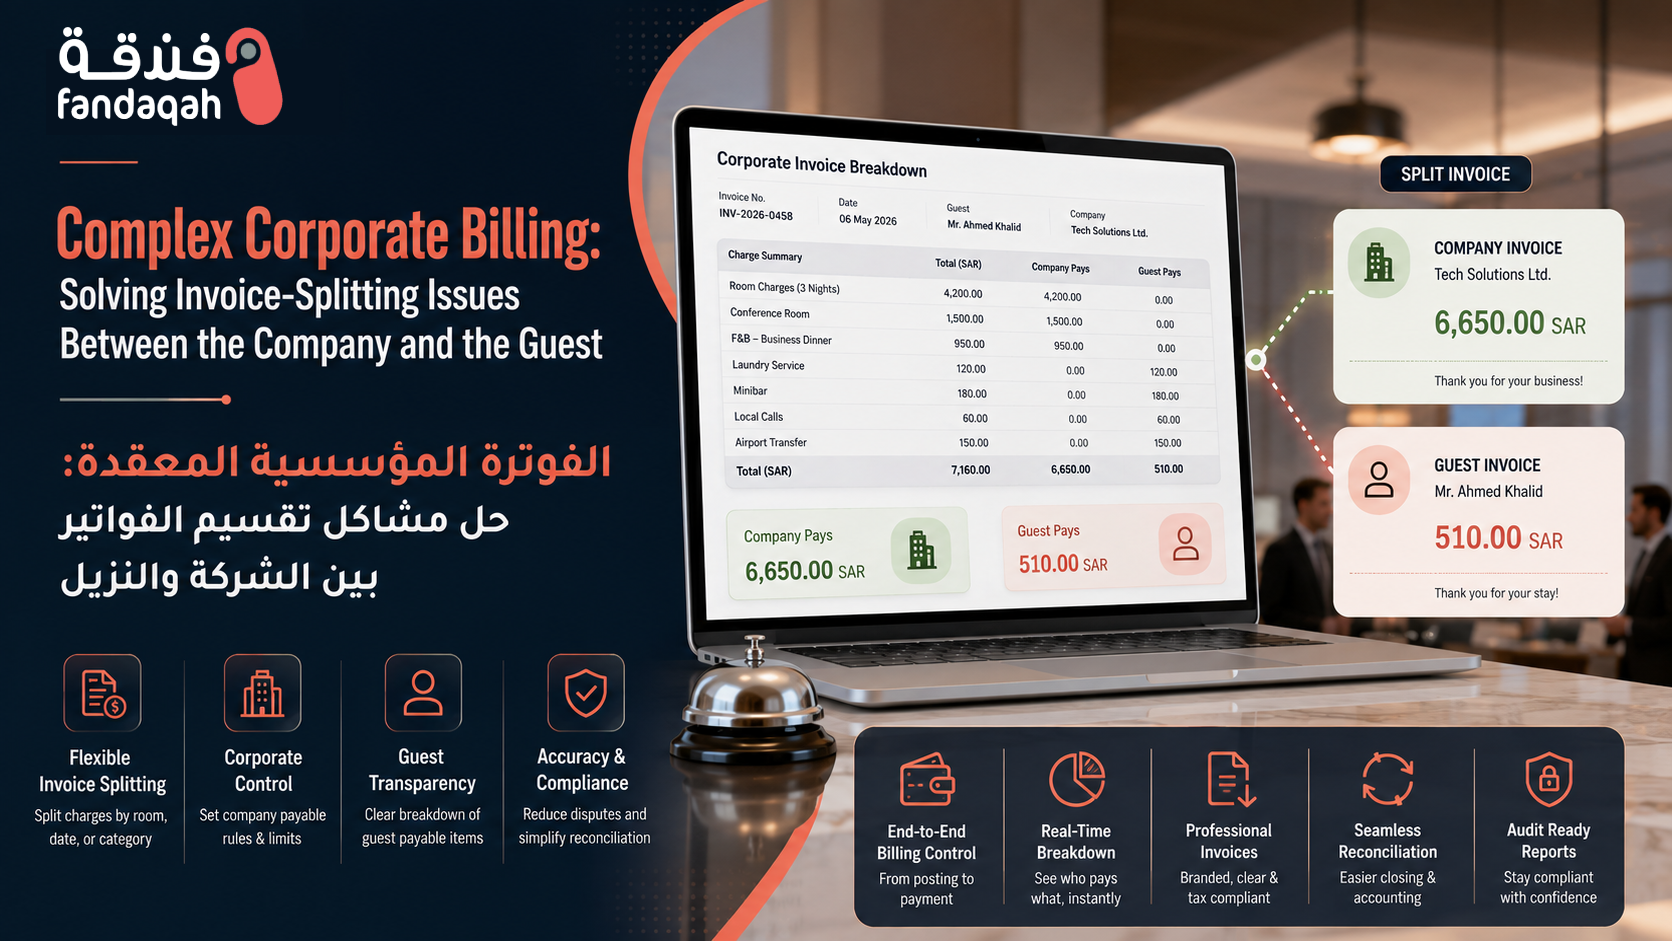
Master complex corporate billing & invoice splitting between company and guest. Automate ZATCA-compliant solutions for Saudi hotels & serviced apartments....
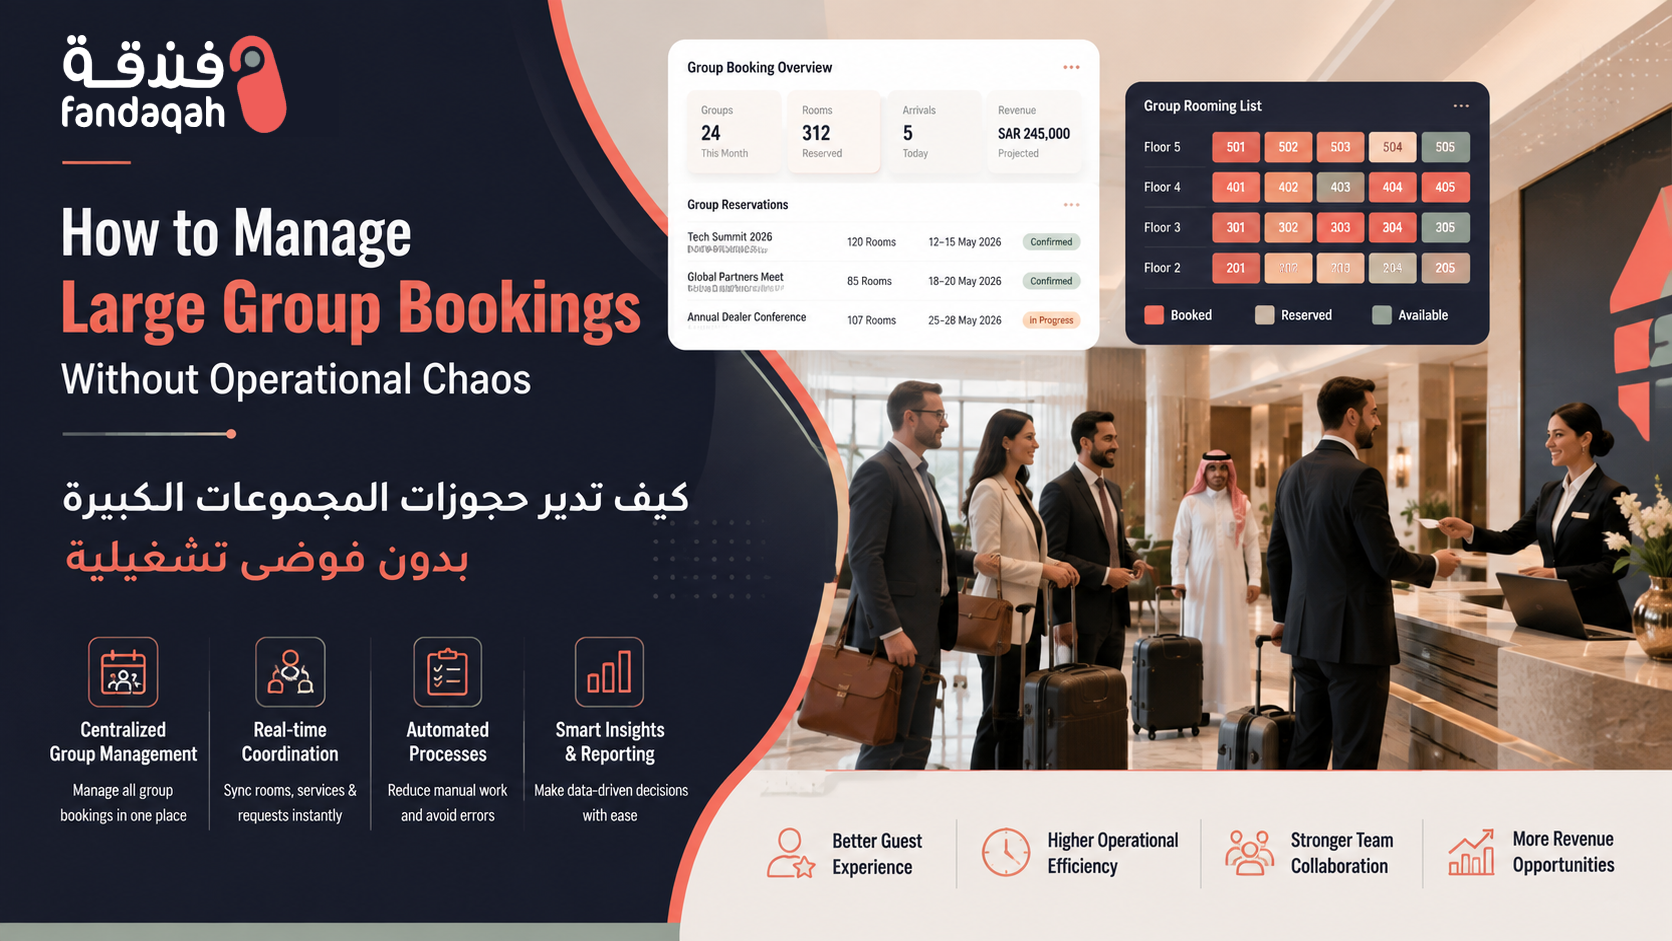
Master large group bookings in Saudi hospitality. Avoid operational chaos with proven strategies for hotels, restaurants & events during Hajj, Riyadh Season & Vision 2030....
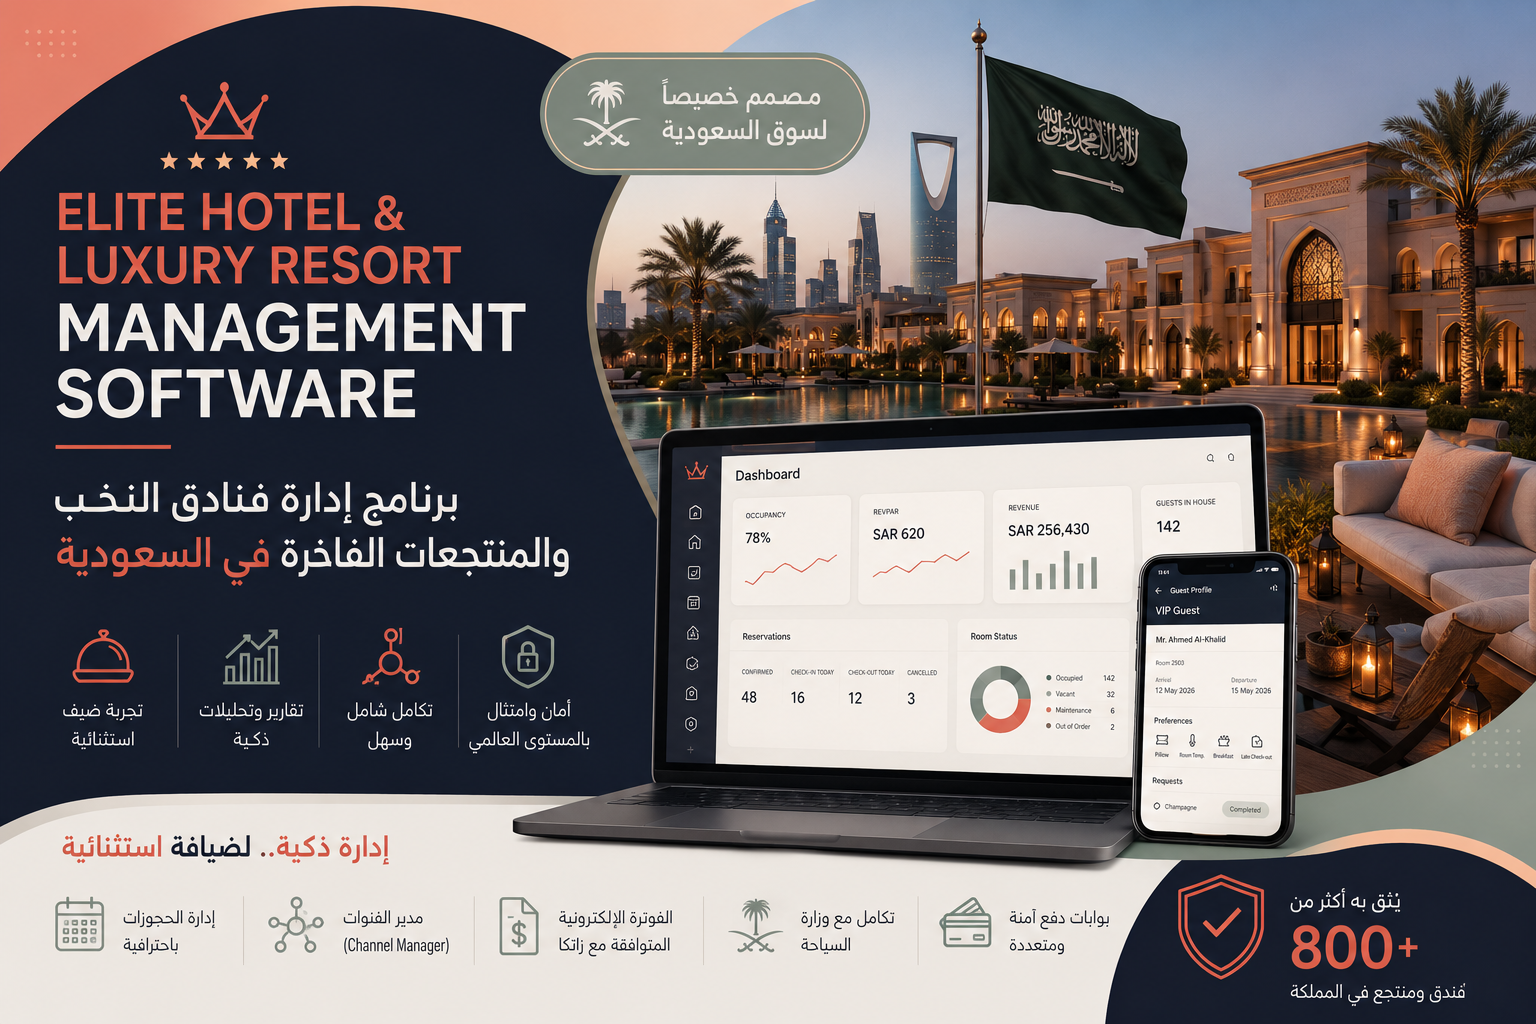
Discover the best cloud-based elite hotel & luxury resort management software (PMS) for Saudi Arabia. Boost guest experience, automate operations & align with Vision 2030....
Practical guide for independent boutique hotels in Saudi Arabia to compete with major chains on a limited budget. Leverage local hospitality, organic SEO/GEO, Vision 2030 opportunities, and smart part...
Explore the rise of AI receptionists in hotels. This expert analysis compares AI to human front desks, examining benefits, drawbacks, and the future of hospitality. Discover if AI is truly better for ...
Unlock the secrets to a fully booked hotel. Discover 50 actionable marketing ideas, from local SEO to immersive virtual tours, designed to skyrocket your bookings and boost revenue....
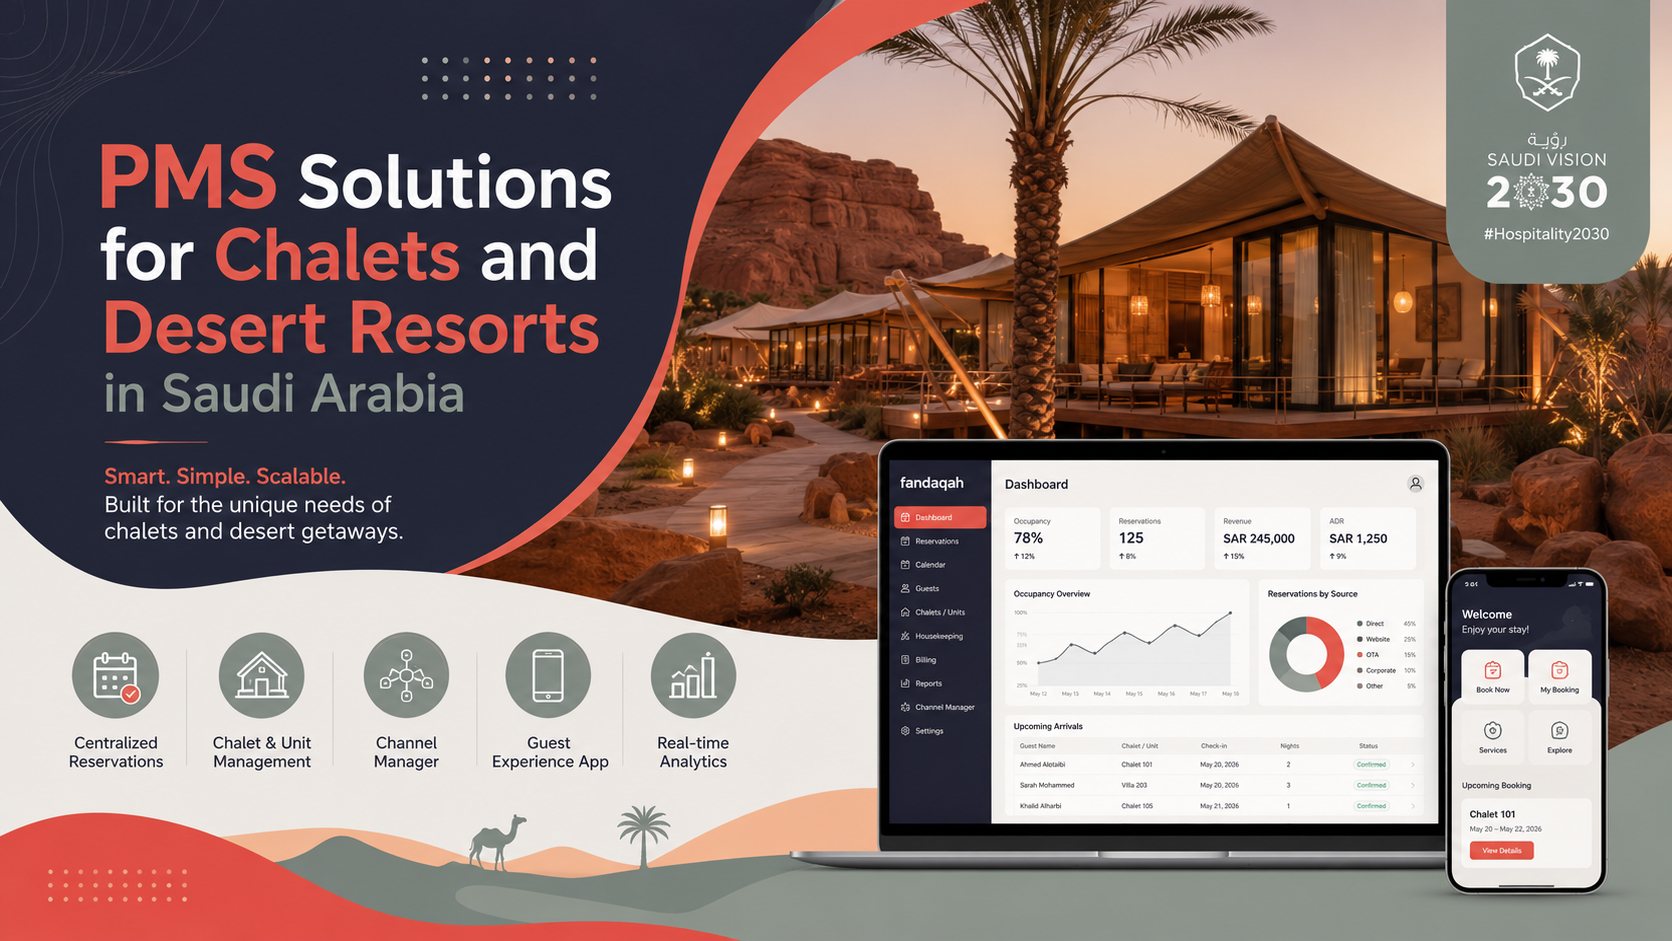
Discover how a modern PMS transforms chalet and desert resort management in Saudi Arabia. Boost bookings, automate operations, and align with Vision 2030 tourism goals....
ZATCA e-invoicing alone isn’t enough. Learn how Saudi hotels can secure guest payment data with PCI DSS, NCA controls, and Vision 2030-aligned strategies to prevent breaches and build trust....
Where should Saudi hotels store guest data? A practical guide to data sovereignty, PDPL compliance, local cloud storage, and protecting privacy under Vision 2030....
Secure hotel PMS accounts with passkeys. A practical guide for Saudi hotel owners on passwordless, phishing-resistant authentication, implementation, and recovery....
Learn how Saudi hotels can cut energy, water, and food waste costs while aligning with Vision 2030. Practical steps, KPIs, and a clear sustainability plan for better profits and guest experience....
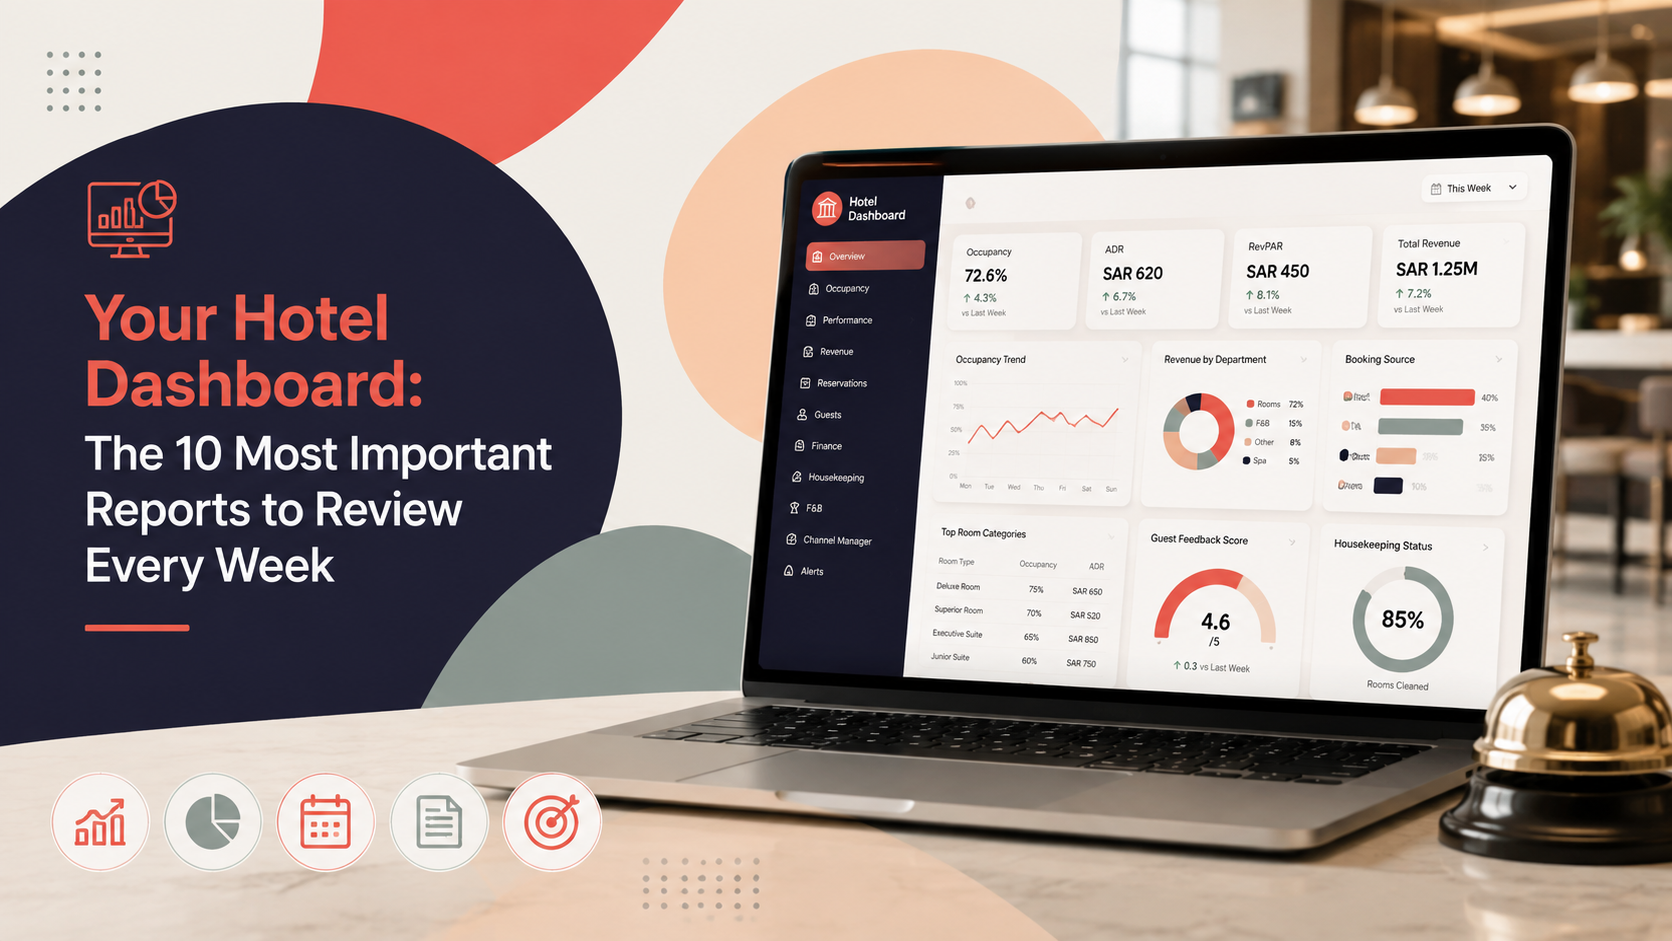
Discover the 10 essential hotel dashboard reports to review every week—occupancy, ADR, RevPAR, booking pace, channels, guest satisfaction & more—to boost revenue and performance in Saudi Arabia....
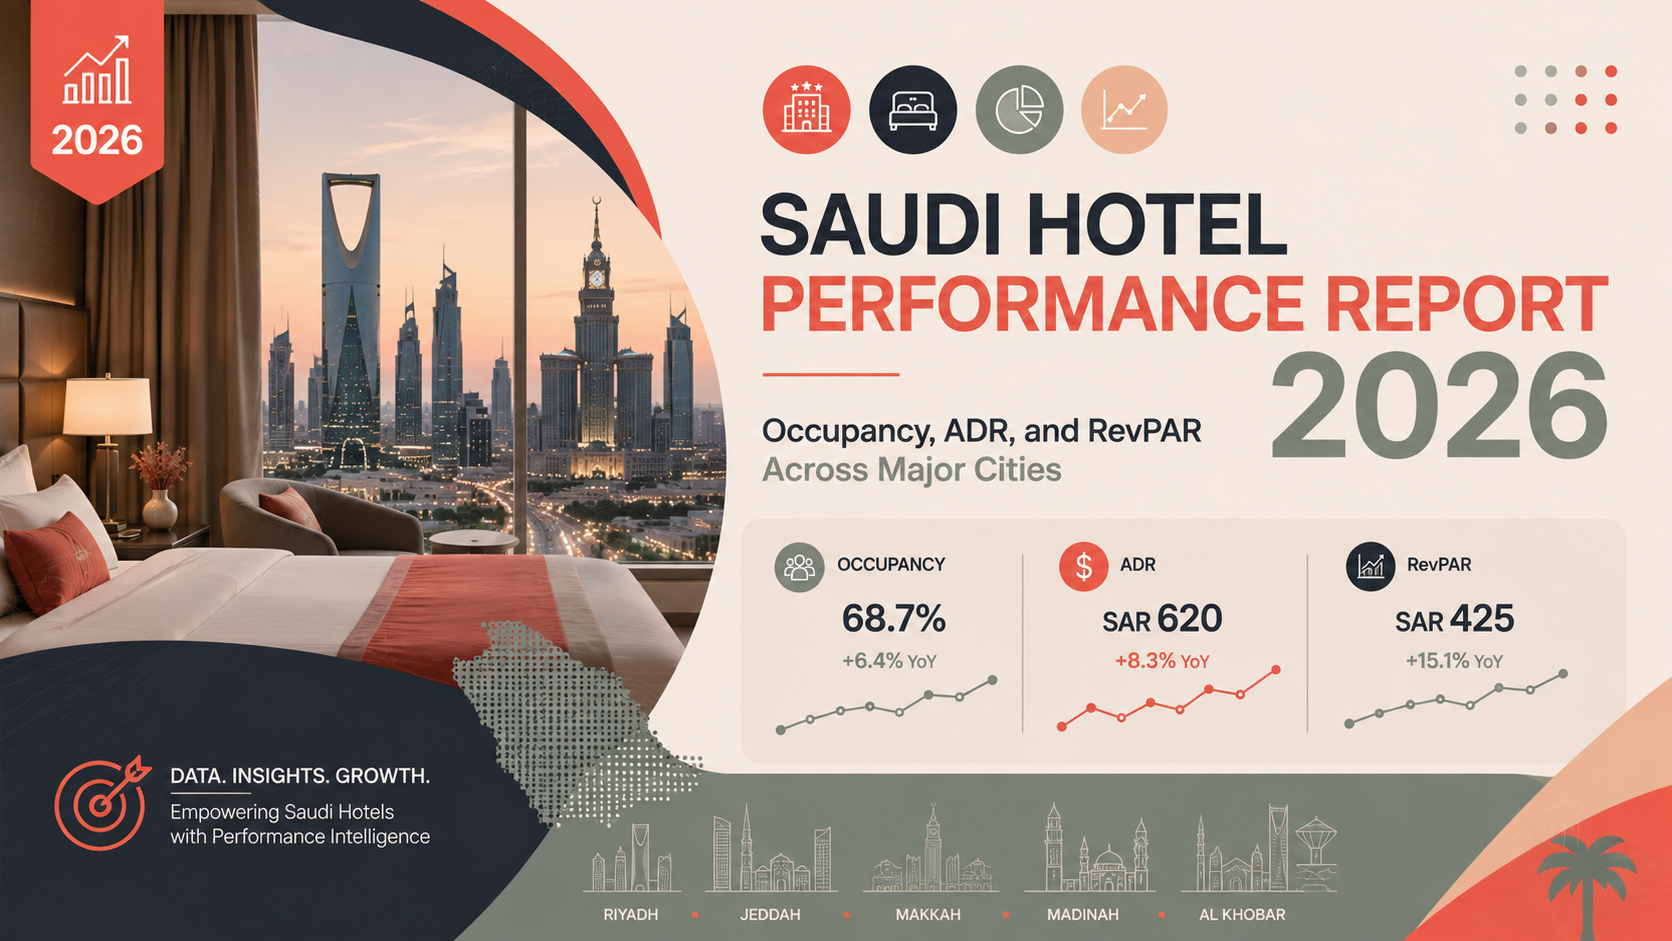
Discover the Saudi Hotel Performance Report 2026 with projected occupancy, ADR, and RevPAR for Riyadh, Jeddah, Makkah, Madinah, Dammam, and AlUla. Key insights for investors and operators aligned with...
Discover how Saudi hotels use big data analytics, dynamic pricing, and predictive tools to increase occupancy, raise RevPAR, and support Vision 2030 tourism goals....
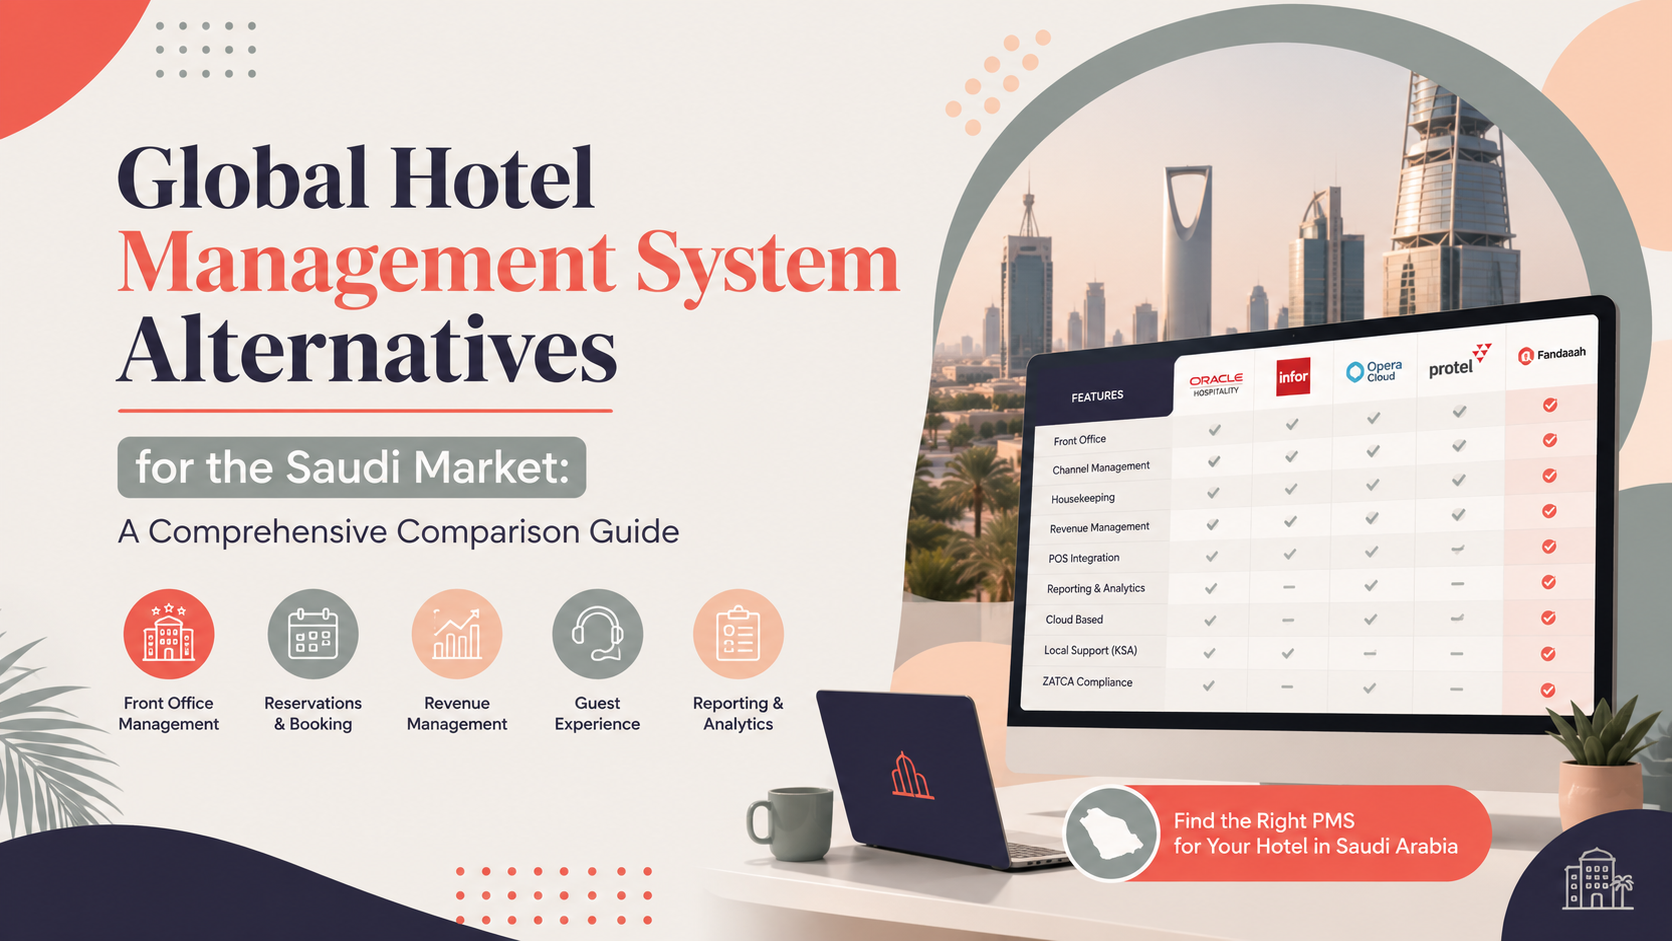
Compare the best hotel management system alternatives for Saudi hotels. Cloudbeds, Mews, Deyafa & more with full Fatoorah e-invoicing support, Arabic UI & Vision 2030 readiness....
Discover 7 warning signs your current hotel PMS is silently draining profits. Learn how upgrading boosts revenue, cuts costs & ensures Dyafa compliance in Saudi Arabia....
Compare Fandaqah vs SiteMinder for Saudi hotels. Discover which channel manager & booking engine wins on Arabic support, local OTAs, Mada payments, pricing & Vision 2030 fit....
Compare Fandaqah and Hotelogix for small & mid-sized hotels in Saudi Arabia and the Gulf. Arabic-first PMS, ZATCA compliance, local payments & more....
Ready-to-use PMS Request for Proposal (RFP) template for Saudi hotels. Compare vendors, define requirements, integrations, security & implementation for smarter hotel software selection....
Learn how to migrate your hotel data to a new PMS without risk. Discover the 2026 step-by-step migration checklist for Saudi hotels, including testing, security, and successful go-live planning....
Learn how a hotel PMS helps front office managers prevent room assignment mistakes, reduce billing errors, and improve guest satisfaction in Saudi hotels....
Learn how hotel sales managers in Saudi Arabia win corporate contracts and conference business with smarter outreach, pricing, and partnerships....
Learn how hotel IT managers choose secure, ZATCA-compliant systems, protect guest data, and ensure seamless PMS, POS, and e-invoicing integration. ...
Discover the hotel food and beverage manager’s core responsibilities, technology tools, and how they improve performance in Saudi hospitality....
Learn the hotel revenue manager's role, key tools, KPIs, and how a PMS helps maximize hotel profitability with dynamic pricing and revenue management....
Learn how a unified omnichannel guest experience improves hotel operations, guest satisfaction, loyalty, and direct bookings with modern hospitality technology....
Learn how Saudi hotels can attract bleisure travelers through smart hospitality strategies, better guest experiences, and Vision 2030 tourism opportunities....
Discover how a smart guest app improves hotel guest loyalty, increases direct bookings, enhances the guest experience, and supports digital hospitality in Saudi Arabia....
Learn how hotel wholesalers work, their benefits and risks, and how Saudi hotels can improve occupancy, revenue, and global distribution....
Learn how hotels in Saudi Arabia can maintain rate parity, monitor pricing across OTAs, protect revenue, and improve distribution strategy....
Learn how Saudi hotels can improve Google Hotel Ads visibility, price accuracy, direct bookings, and profitability without increasing ad costs....
Discover how Saudi hotels in Riyadh, Jeddah, Dammam, and beyond can use a Global Distribution System (GDS) to attract corporate bookings, increase weekday occupancy, and balance distribution channels....
Learn how dynamic pricing uses AI to automatically adjust hotel room rates in real-time. Maximize RevPAR during Hajj, Riyadh Season & Vision 2030 projects with proven strategies for Saudi hotels....
Discover what ghost bookings are, how they silently drain hotel revenue in Saudi Arabia, and practical strategies to prevent them — especially during Hajj, Umrah, and Riyadh Season — in line with ...
Discover the ultimate guide to hotel demand forecasting in Saudi Arabia. Learn smart strategies for dynamic pricing, revenue management, and maximizing occupancy during Hajj, Vision 2030 events, and p...
Discover how to choose the best Revenue Management System (RMS) for your Saudi hotel. Expert tips on dynamic pricing, forecasting, integrations, and maximizing RevPAR in line with Vision 2030....
Discover how Arab tourists, especially Saudis, are using AI tools like ChatGPT and Gemini to book hotels. Essential strategies for Saudi hoteliers to optimize for AI discovery and thrive under Vision ...
Discover the key difference between hotel automation and true autonomy. Learn how Saudi hotels can embrace AI-driven autonomous operations aligned with Vision 2030 for superior guest experiences and e...
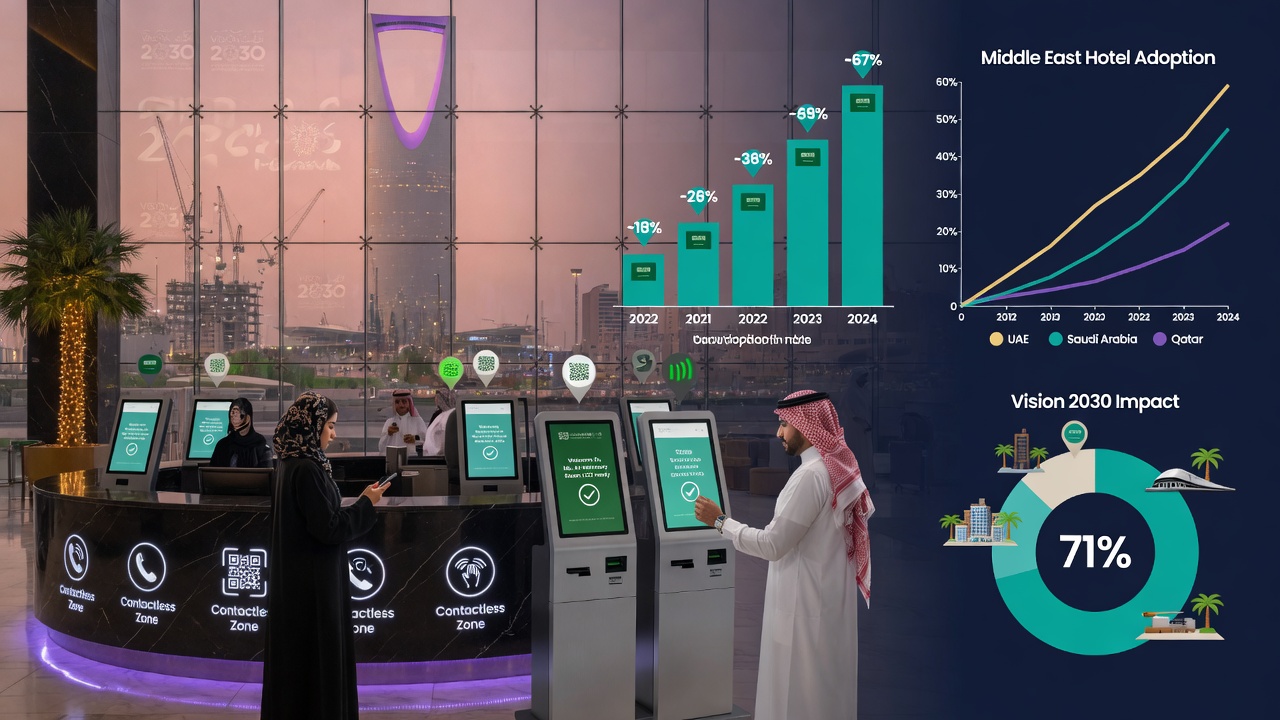
Fast-rising contactless check-in in Middle East hotels 2026. Saudi adoption at 68% thanks to Vision 2030. Benefits, cases & tips for hotel owners....
Discover the best free and affordable hotel PMS tools for 2026 in Saudi Arabia. Features ZATCA e-invoicing, channel manager, and Arabic support for budget hotels....
Complete guide to hotel distribution channels in the Arab world. Optimize OTAs, direct bookings, GDS & metasearch for Saudi hotels to grow revenue with Vision 2030 strategies....
Explore how modern unified payment platforms are simplifying cross-border hotel payments in the GCC. Saudi hotels can now achieve same-day settlements, multi-currency support, reduced fees, automated ...
Master Google Hotel Ads for Saudi hotels in 2026. Optimize your metasearch strategy to drive direct bookings, reduce OTA commissions, and leverage Vision 2030 tourism growth....
Compare Cloudbeds, Mews and Fandaqah PMS platforms for Saudi hotels in 2026. See which system wins on Arabic support, local payments (Mada/STC Pay), Hajj/Umrah peak handling, Vision 2030 readiness and...
Discover how to design a hotel loyalty program with reward points in Saudi Arabia. Boost guest retention, align with Vision 2030, and keep guests returning....
Discover the 12 essential questions Saudi hotels must ask before choosing a Hotel Management System (PMS), including ZATCA compliance, cloud PMS, and Hajj & Umrah operations....
Discover the best hotel management software for 2026 in Saudi Arabia. Compare features, pricing, ZATCA e-invoicing, and Vision 2030 readiness. Free consultation....
Discover how a serviced apartments operations program streamlines hospitality management in Saudi Arabia. Features, benefits & Vision 2030 insights inside....
Discover how hotel apartment software in Saudi Arabia automates accounting, boosts occupancy, ensures ZATCA compliance, and aligns with Vision 2030....
Discover how a hotel operating program (PMS) can streamline operations, boost revenue, and delight guests in Saudi Arabia's tourism sector....
Discover how serviced apartment management software streamlines Saudi hospitality, ensures Taskeen compliance, and boosts revenue. Complete guide....
Discover the best hotel software and PMS in Saudi Arabia. Our ultimate guide covers features, ZATCA compliance, Vision 2030 trends, and top picks for hotels of all sizes....
Discover Saudi Arabia’s Housing Allocation Program for government employees: eligibility, Sakani application process, and Vision 2030 homeownership goals in 2026....
Explore the best placement program for strategic talent deployment in KSA. Achieve Vision 2030 goals, enhance Saudization, streamline HR placement. Your guide....
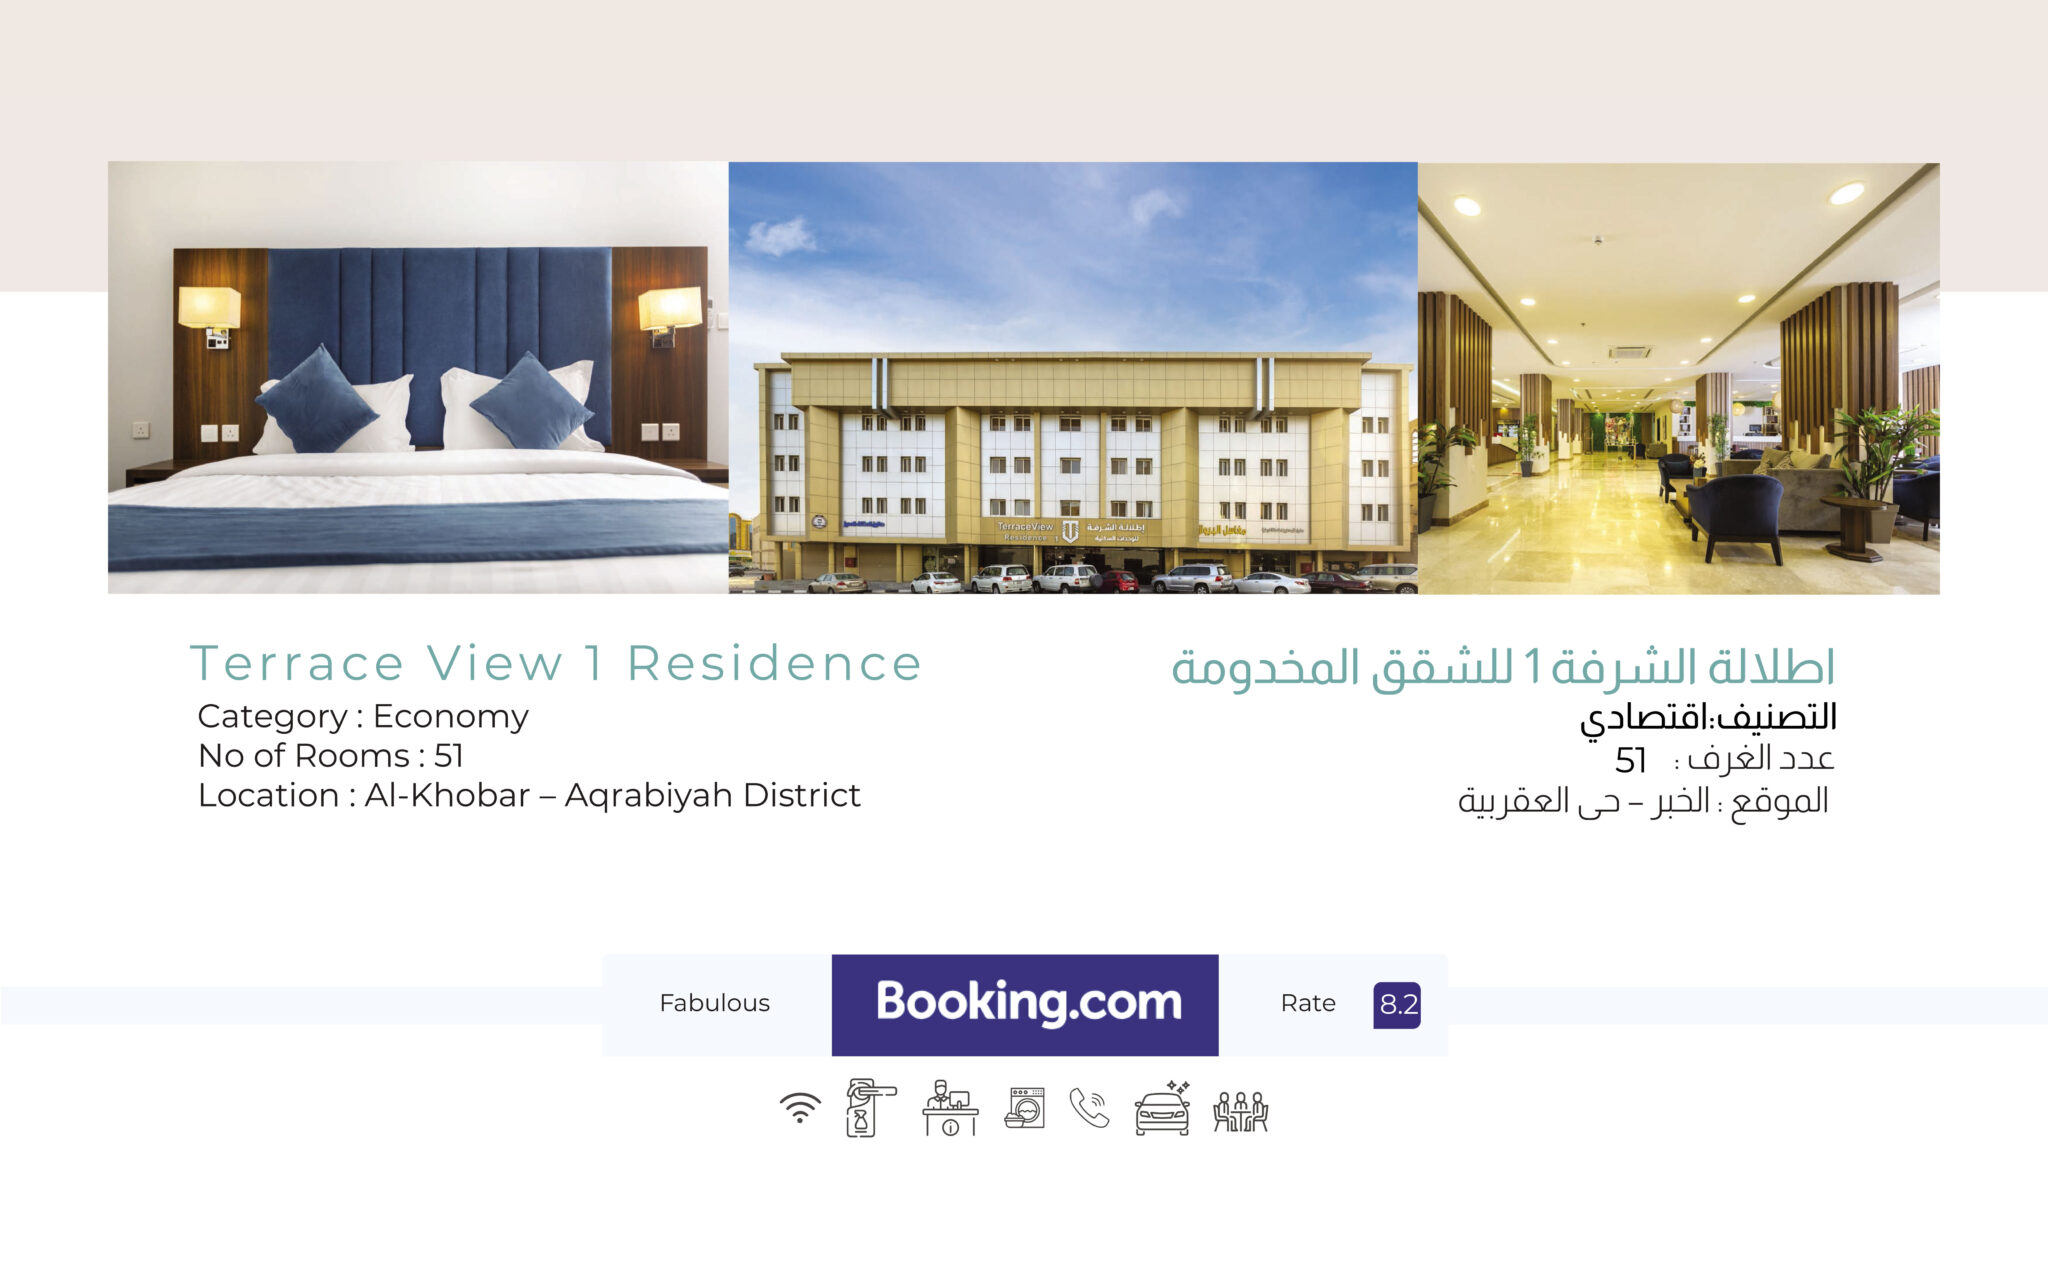
Terrace View 1 Residence, a cozy economy-class serviced apartment in Al-Khobar, faced operational hurdles that many growing hotels and apartments encounter: ...
Eco-Friendly Hotel in Saudi Arabia: Sustainability Guide for Vision 2030. Learn energy, water and waste savings to lower costs and attract eco guests with Fandaqah....
Learn how Saudi hotels can attract MICE tourism with event-ready facilities, smart marketing, group booking tools, and ZATCA-compliant operations....
Discover key principles of scalable hotel digital transformation for Saudi hotels, including cloud PMS, automation, ZATCA compliance, and guest experience....
7 friction points killing hotel Google ratings in Riyadh & Jeddah. Fix check-in, cleanliness, communication, noise, fees & tech to boost ratings & bookings....
Discover how guest personalization turns Saudi hotel visitors into loyal advocates. Learn strategies for tailored experiences and loyalty programs....
Complete guide to Personal Data Protection Law compliance for Saudi hospitality. Practical steps to protect guest data, build trust, and meet SDAIA requirements under Vision 2030...
Discover how to stop revenue leakage in Saudi hotels from tax, VAT, and service charge errors. Cloud PMS ensures ZATCA compliance and protects profitability....
Discover how staycation marketing helps Saudi hotels attract local residents and fill empty weeks. Actionable strategies for year-round occupancy....
Learn how Saudi hotels can win corporate RFPs and secure business travel bookings. Strategies for rates, PMS billing, and contract negotiation....
Increase hotel bookings & iftar sales during Ramadan 2026 in Saudi Arabia with targeted marketing strategies, iftar packages, Ramadan tents, and PMS automation....
Learn how WhatsApp Business enhances guest communication and direct bookings for Saudi hotels. Discover strategies, automation & Vision 2030 alignment....
Discover how to choose the best hotel channel manager for Saudi Arabia's hospitality sector in 2026. Boost occupancy, sync rates, and maximize revenue with our complete guide....
Guide to hotel sales manager skills, tools & strategies for corporate and pilgrimage sales in Saudi Arabia. Win with Vision 2030....
Learn to implement self-service & digital check-in in Saudi hotels seamlessly. Align with Vision 2030, cut wait times by 70%, and enhance guest experience....
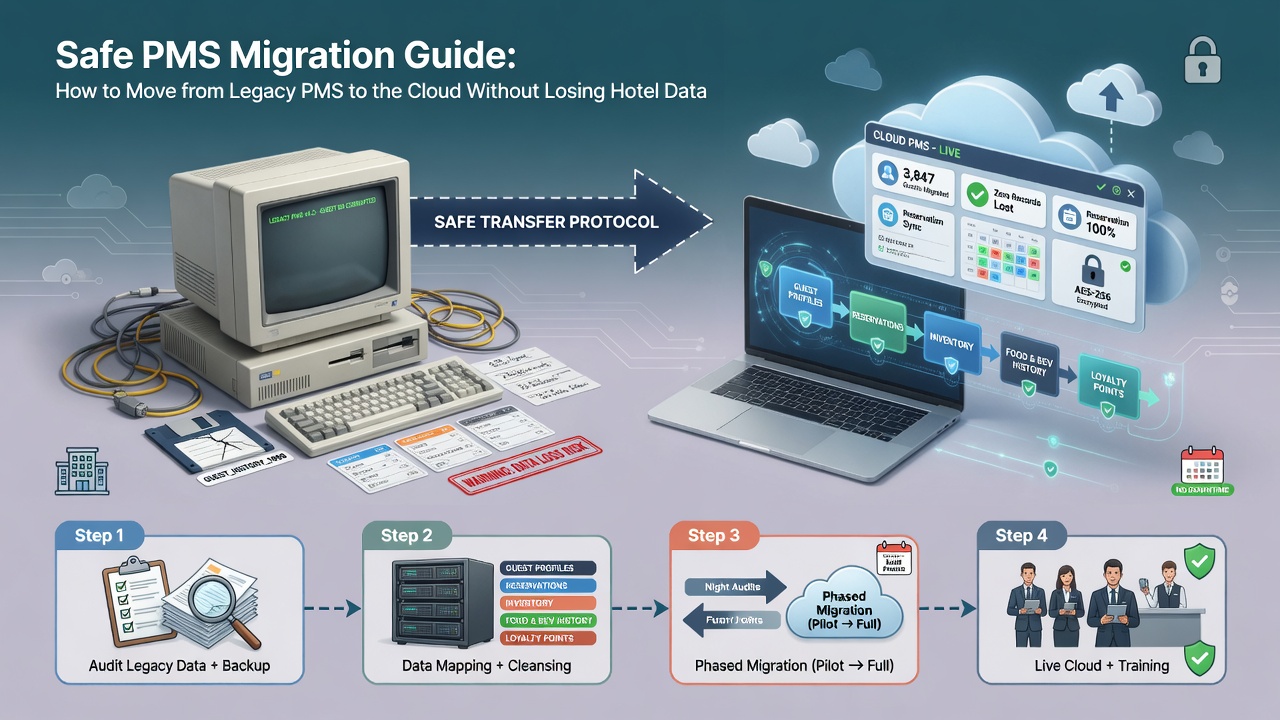
Step-by-step guide for Saudi hotels to safely migrate from legacy PMS to cloud. Protect guest data, reservations & finances. Learn best practices, avoid data loss...
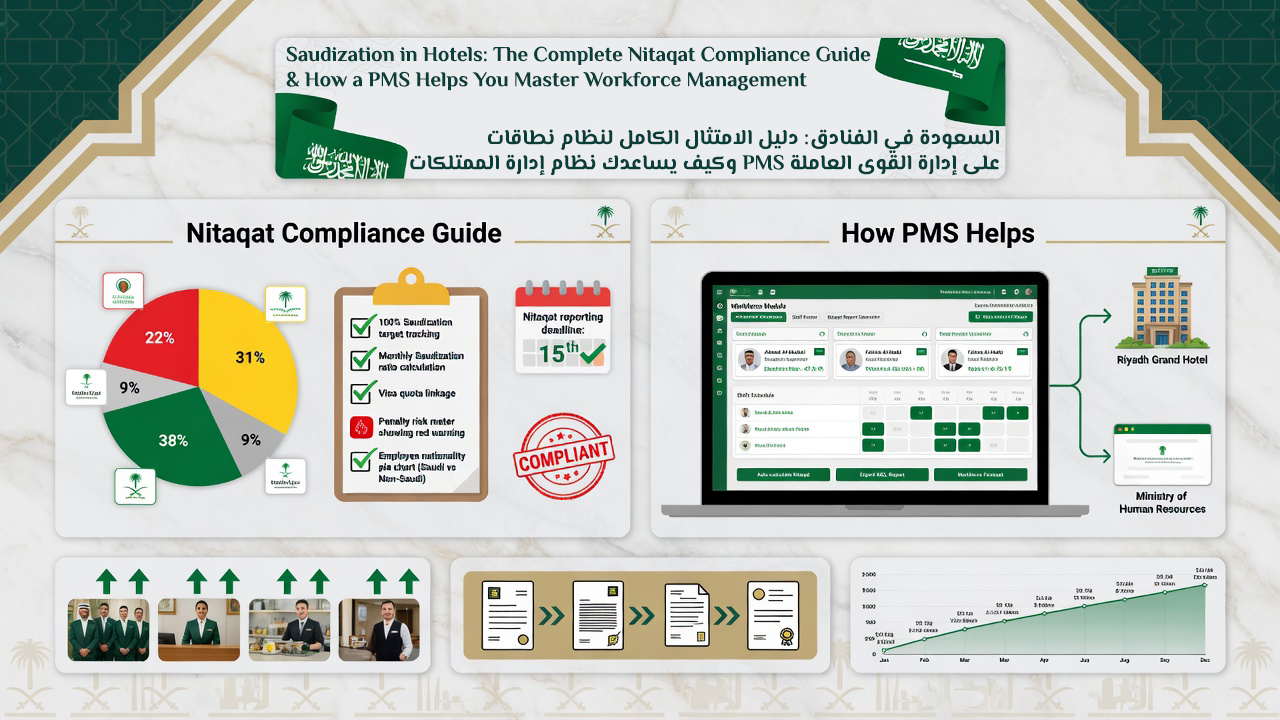
Complete guide to Saudization in hotels & Nitaqat compliance in KSA. Learn how a PMS helps manage workforce, achieve green band status, and avoid penalties. ...
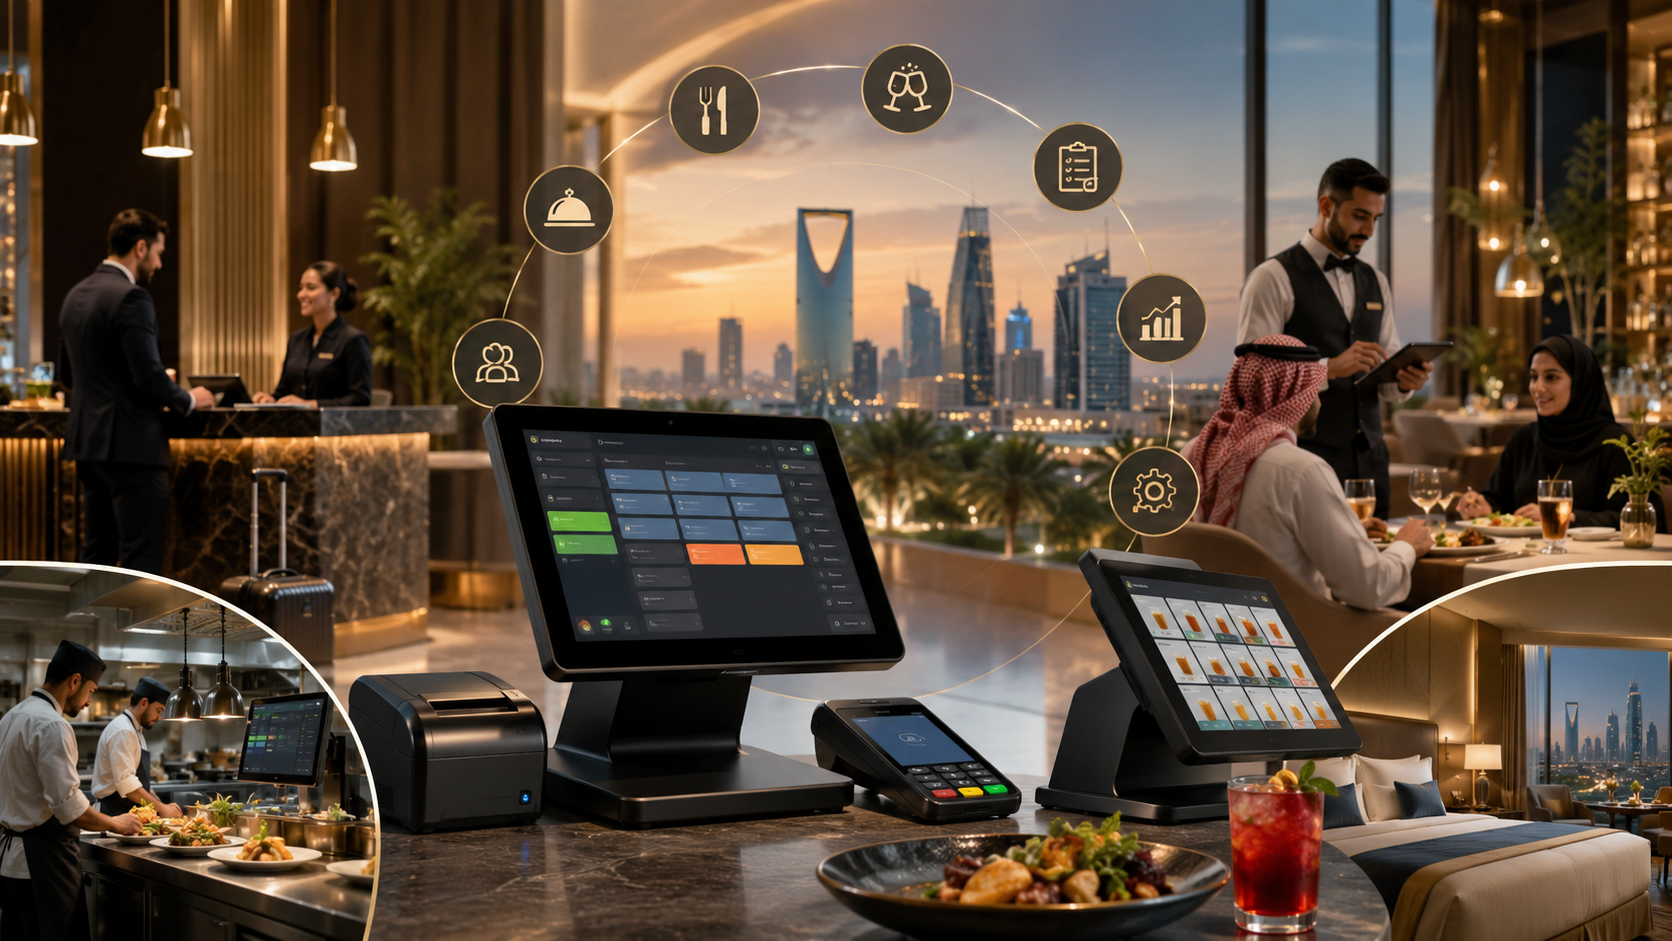
Master connecting hotel restaurant, café, and room service billing with your PMS — ZATCA-compliant, Mada, STC Pay ready. Guide for Saudi hotels Vision 2030....
Discover the best hotel PMS for serviced apartments and chalets in Saudi Arabia. Streamline operations, boost direct bookings, and ensure Shomoos compliance in 2026....
Compare top Saudi hotel payment gateways with Mada & STC Pay. Boost direct bookings with SAMA-compliant, ZATCA-ready solutions like HyperPay, PayTabs....
Streamline Umrah & Hajj pilgrim stays with automation. Bulk check‑ins, prayer‑aware services, Nusuk integration & Vision 2030 compliance for Saudi hotels....
Master cash flow management for small hotels in Saudi Arabia. Our 2026 guide covers seasonal planning, cost control, and profit optimization....
Safeguard guest data in Saudi hotels with our expert guide covering NCA, PDPL, PCI DSS compliance, ransomware prevention, and cybersecurity best practices....
Learn how to increase direct hotel bookings in Saudi Arabia, cut OTA commissions, and boost profit with direct booking engine, loyalty program & best-rate....
Discover how Cloud PMS technology accelerates Saudi Vision 2030 tourism goals. Improve hotel efficiency and guest experience with digital transformation in KSA....
Learn how AI in Saudi hotels boosts revenue through dynamic pricing, chatbots, and guest personalization. Start your smart hospitality transformation....
Master seasonal demand in Saudi Arabia. Learn how to optimize hotel revenue during Hajj and Umrah using automated PMS, dynamic pricing, and channel managers...
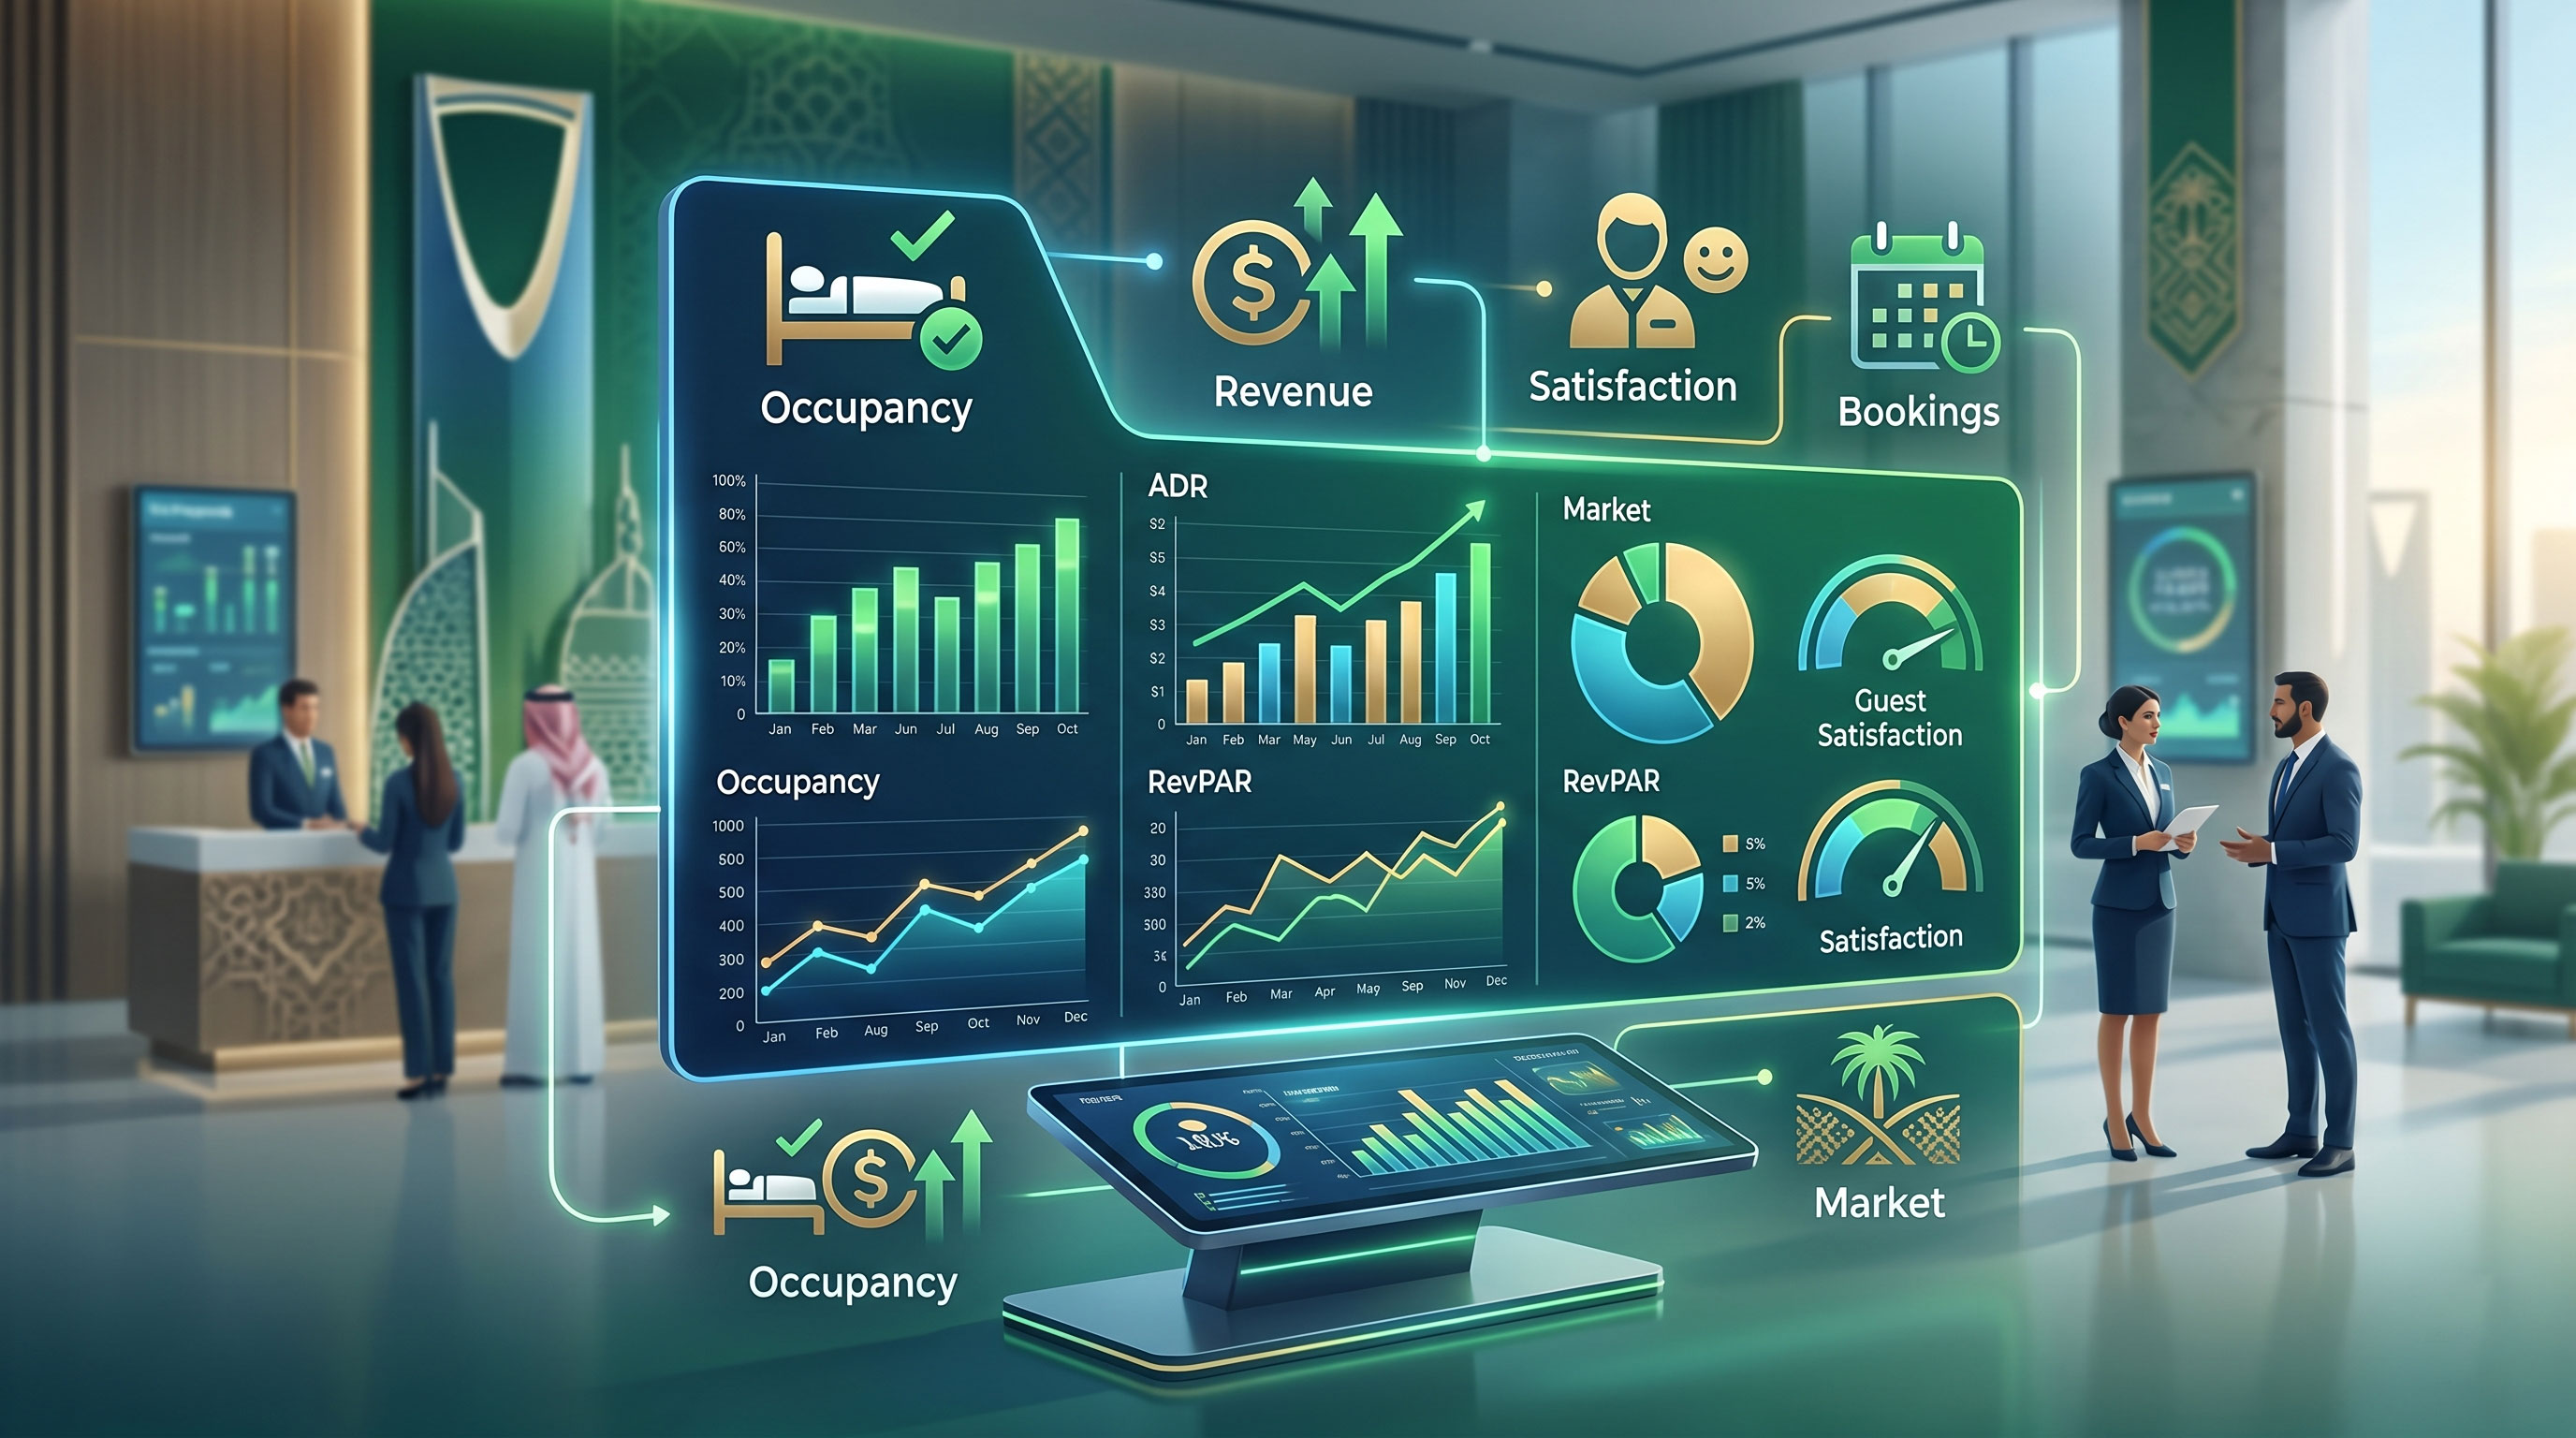
Discover essential daily KPIs every hotel owner in Saudi Arabia should track with a BI dashboard. Boost RevPAR, compliance, and profit with data-driven insights....
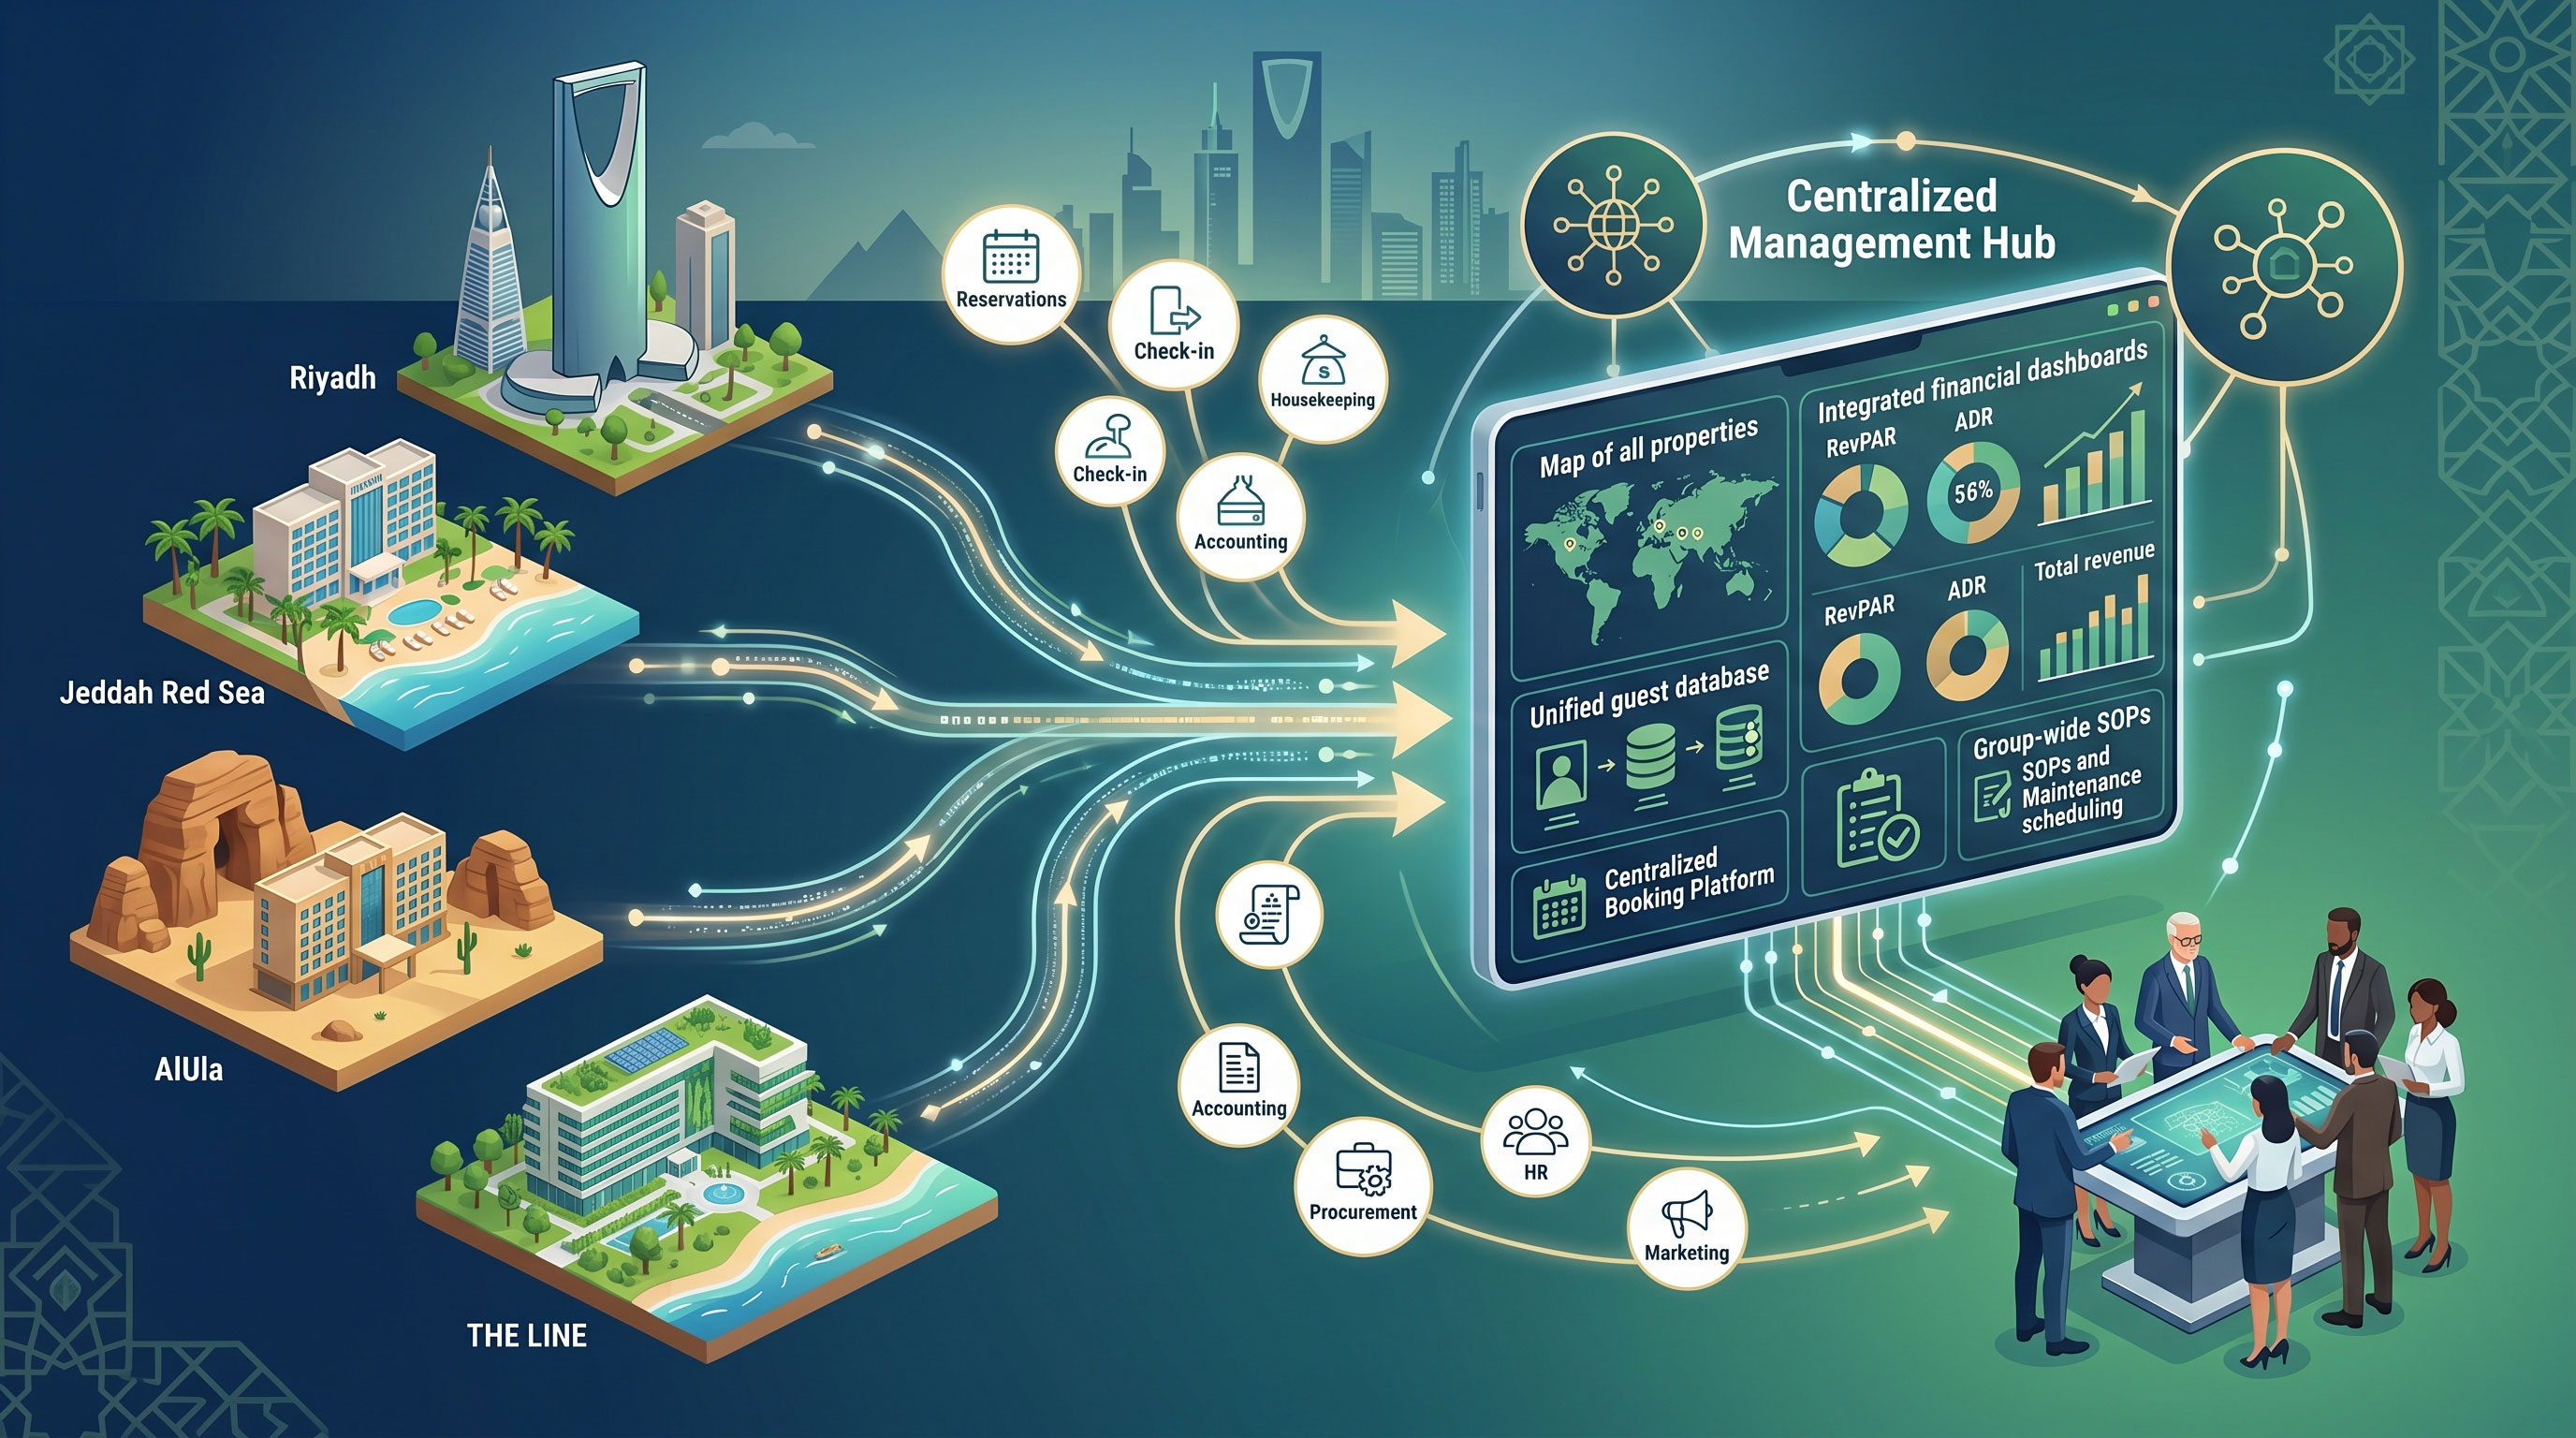
Centralize hotel operations in Saudi Arabia: multi-property management, unified reporting, revenue optimization, procurement, HR, and ZATCA compliance for Vision 2030 growth....
Compare what Saudi hotels need in 2026: cloud PMS, ZATCA e-invoicing, Shomoos, Ministry of Tourism, channel manager, booking engine, automation, and guest management....
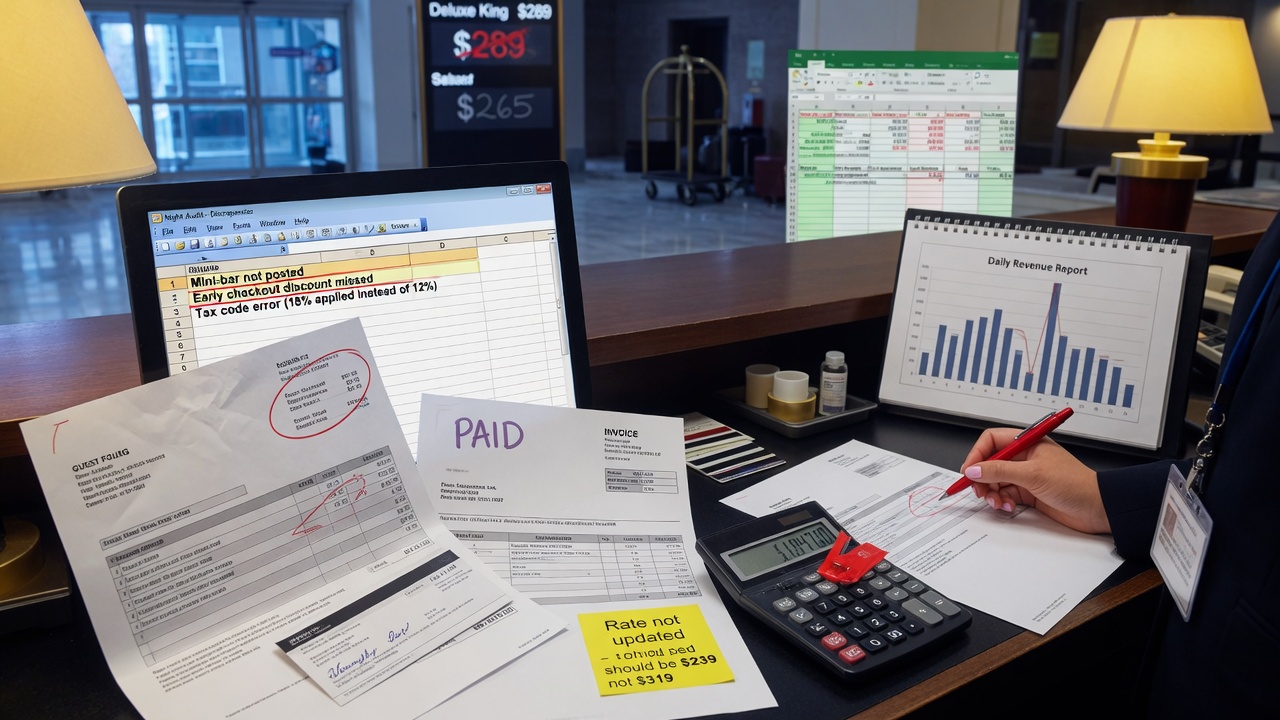
Top common hotel billing errors in Saudi hotels cost SAR 100K+ yearly via VAT & fee mistakes. Stop leakage with ZATCA PMS automation now....
Compare long stay vs short stay PMS for Saudi hospitality. Learn key differences, must‑have features, Ejar compliance, and Vision 2030 insights...
Compare what Saudi hotels need in 2026: cloud PMS, ZATCA e-invoicing, Shomoos, Ministry of Tourism, channel manager, booking engine, automation, and guest management....
Discover why hotel data management is essential for Saudi hotels. Learn how to leverage guest insights, ensure ZATCA & Shomoos compliance, and boost revenue with a modern PMS. Free demo from Fandaqah...
Vision 2030 is transforming vacation ownership in Saudi Arabia. Explore the hotel meets residential trend at Red Sea Global and NEOM for families and investors....
Saudi Arabia hotel keyless entry under Vision 2030: mobile keys, biometrics, guest benefits, hotel savings, Mövenpick Riyadh and Red Sea Global case studies....
Legacy PMS is silently costing Saudi hotels guests, direct bookings, and revenue through slow operations, poor personalization, and lost opportunities. Discover the true hidden costs of outdated hotel...
Saudi hotels lose tens of thousands of SAR yearly on manual receipt tracking. Discover hidden costs — wasted labor, VAT leakage, fraud & ZATCA risks — and how automated expense management software...
Discover how AI, IoT, and smart building tech are driving sustainable hotel operations in Saudi Arabia. Reduce costs, meet Vision 2030 goals, and enhance guest experience....
Discover what a channel manager is and why Saudi hotels need it. Automate OTA distribution, prevent overbookings, boost direct bookings, and stay compliant. Free demo from Fandaqah...

Reduce hotel check-in time from 15 minutes to under 3 minutes using automated Shomoos registration and passport scanning. Free demo for Saudi hotels...

Discover how smart room integration with hotel PMS in Saudi Arabia enhances guest experience, energy efficiency, and compliance with ZATCA & Shomoos. The future of Vision 2030 hospitality starts here....
Discover why Arabic interface and POS integration are essential for hotels in Saudi Arabia. Boost staff efficiency, guest satisfaction, and compliance with Fandaqah’s all-in-one PMS...
Try Fandaqah’s 30‑day free demo account for hotel PMS in Saudi Arabia. Experience ZATCA e‑invoicing, Shomoos integration, passport scanning, and check‑in automation – risk‑free. Start your...
Discover proven strategies to avoid empty rooms during low season in Saudi Arabia. Learn dynamic pricing, direct booking tactics, and how a hotel PMS Saudi Arabia can boost occupancy year‑round. Fre...
ZATCA Phase 2 deadline for hotels: March 31, 2026. Learn Wave 23 requirements, e-invoicing integration, penalties, and how a compliant hotel PMS ensures full compliance. Free demo from Fandaqah...
Complete guide to buying a hotel PMS in Saudi Arabia. Learn key features, compliance with ZATCA & Shomoos, ROI, and how to choose the best hotel management system KSA for your property...
Go paperless with hotel housekeeping and maintenance. Learn how digital checklists, real‑time updates, and integrated PMS boost efficiency, guest satisfaction, and compliance in Saudi Arabia...
Learn how hoteliers can build a business case for new technology. Show ROI, improve guest satisfaction, and ensure ZATCA & Shomoos compliance. Free demo for Saudi hotels...
Discover how gift cards for hotels can boost occupancy, increase revenue, and attract new guests. Learn to integrate with your hotel PMS Saudi Arabia for seamless automation....
Discover proven destination marketing ideas for hotels in Saudi Arabia. Attract more guests, leverage Vision 2030, and boost direct bookings. Free consultation inside....
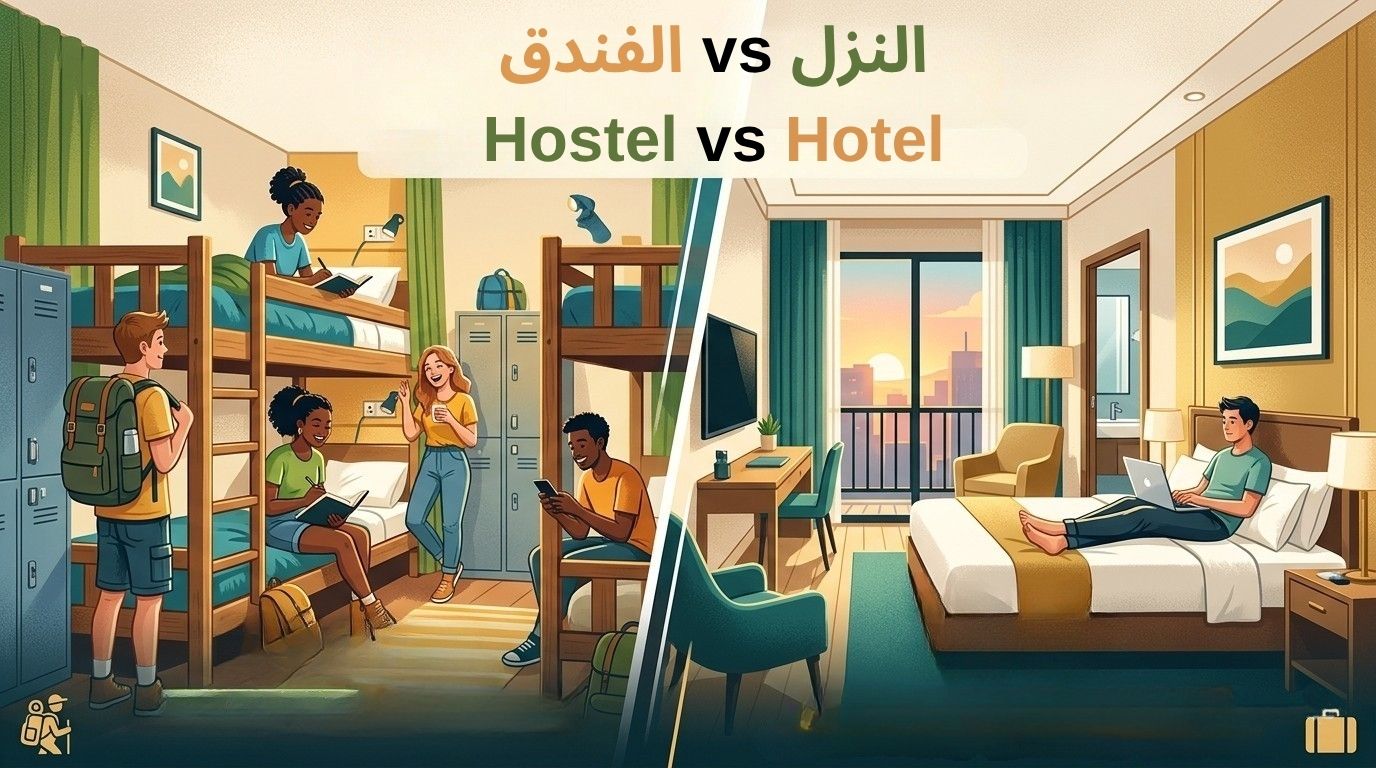
Hostel vs hotel – what's the difference? Compare cost, privacy, amenities, and social experience. Perfect for Saudi travelers and tourists under Vision 2030. Find your ideal stay....
Complete guide to lodging taxes for hotels in Saudi Arabia: VAT (15%), municipality fees, tourism tax, ZATCA e-invoicing compliance, and how to automate tax management. Essential for hoteliers....
Complete guide to PMS training for hotel staff in Saudi Arabia. Learn how to train your team on ZATCA e‑invoicing, Shomoos integration, passport scanning, and check‑in automation. Free demo from F...
Compare the best cloud PMS for serviced apartments in KSA: Fandaqah vs. legacy systems. Discover automation, ZATCA & Shomoos compliance, and why modern cloud PMS wins. Free demo...
Saudi Arabia’s hospitality sector is experiencing unprecedented growth, driven by Vision 2030. Success now requires more than just a prime location—it demands the smart use of hotel management too...
As part of Saudi Arabia’s digital transformation, e-invoicing has become a cornerstone in regulating the relationship between businesses and the Zakat, Tax and Customs Authority (ZATCA). With the ro...
Discover the Kingdom’s transformation through Vision 2030, where ancient spirituality meets modern adventure tourism. The Future of Hospitality Summit is driving regional change. Explore spiritual j...
Property management software Saudi Arabia by Fandaqah: ZATCA & Shomoos compliant, passport scanner, 85% faster check-in. Trusted by 850+ hotels. Demo now....
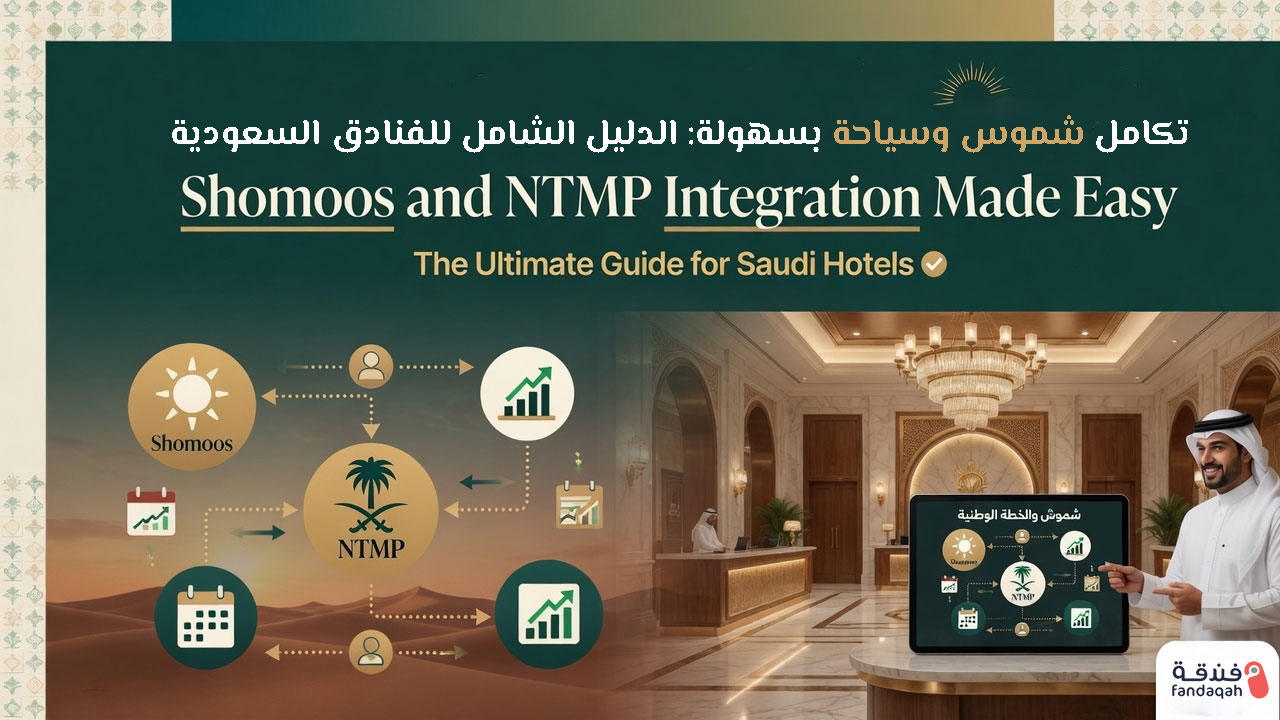
Complete guide to Shomoos and Siyaha integration for Saudi hotels. Learn how to automate guest registration, avoid fines, and streamline operations with a modern hotel PMS. Free demo from Fandaqah...
Complete guide to hotel PMS cost in Saudi Arabia. Understand pricing models, hidden fees, ZATCA & Shomoos compliance costs, and how to choose the right hotel management system KSA for your budget...
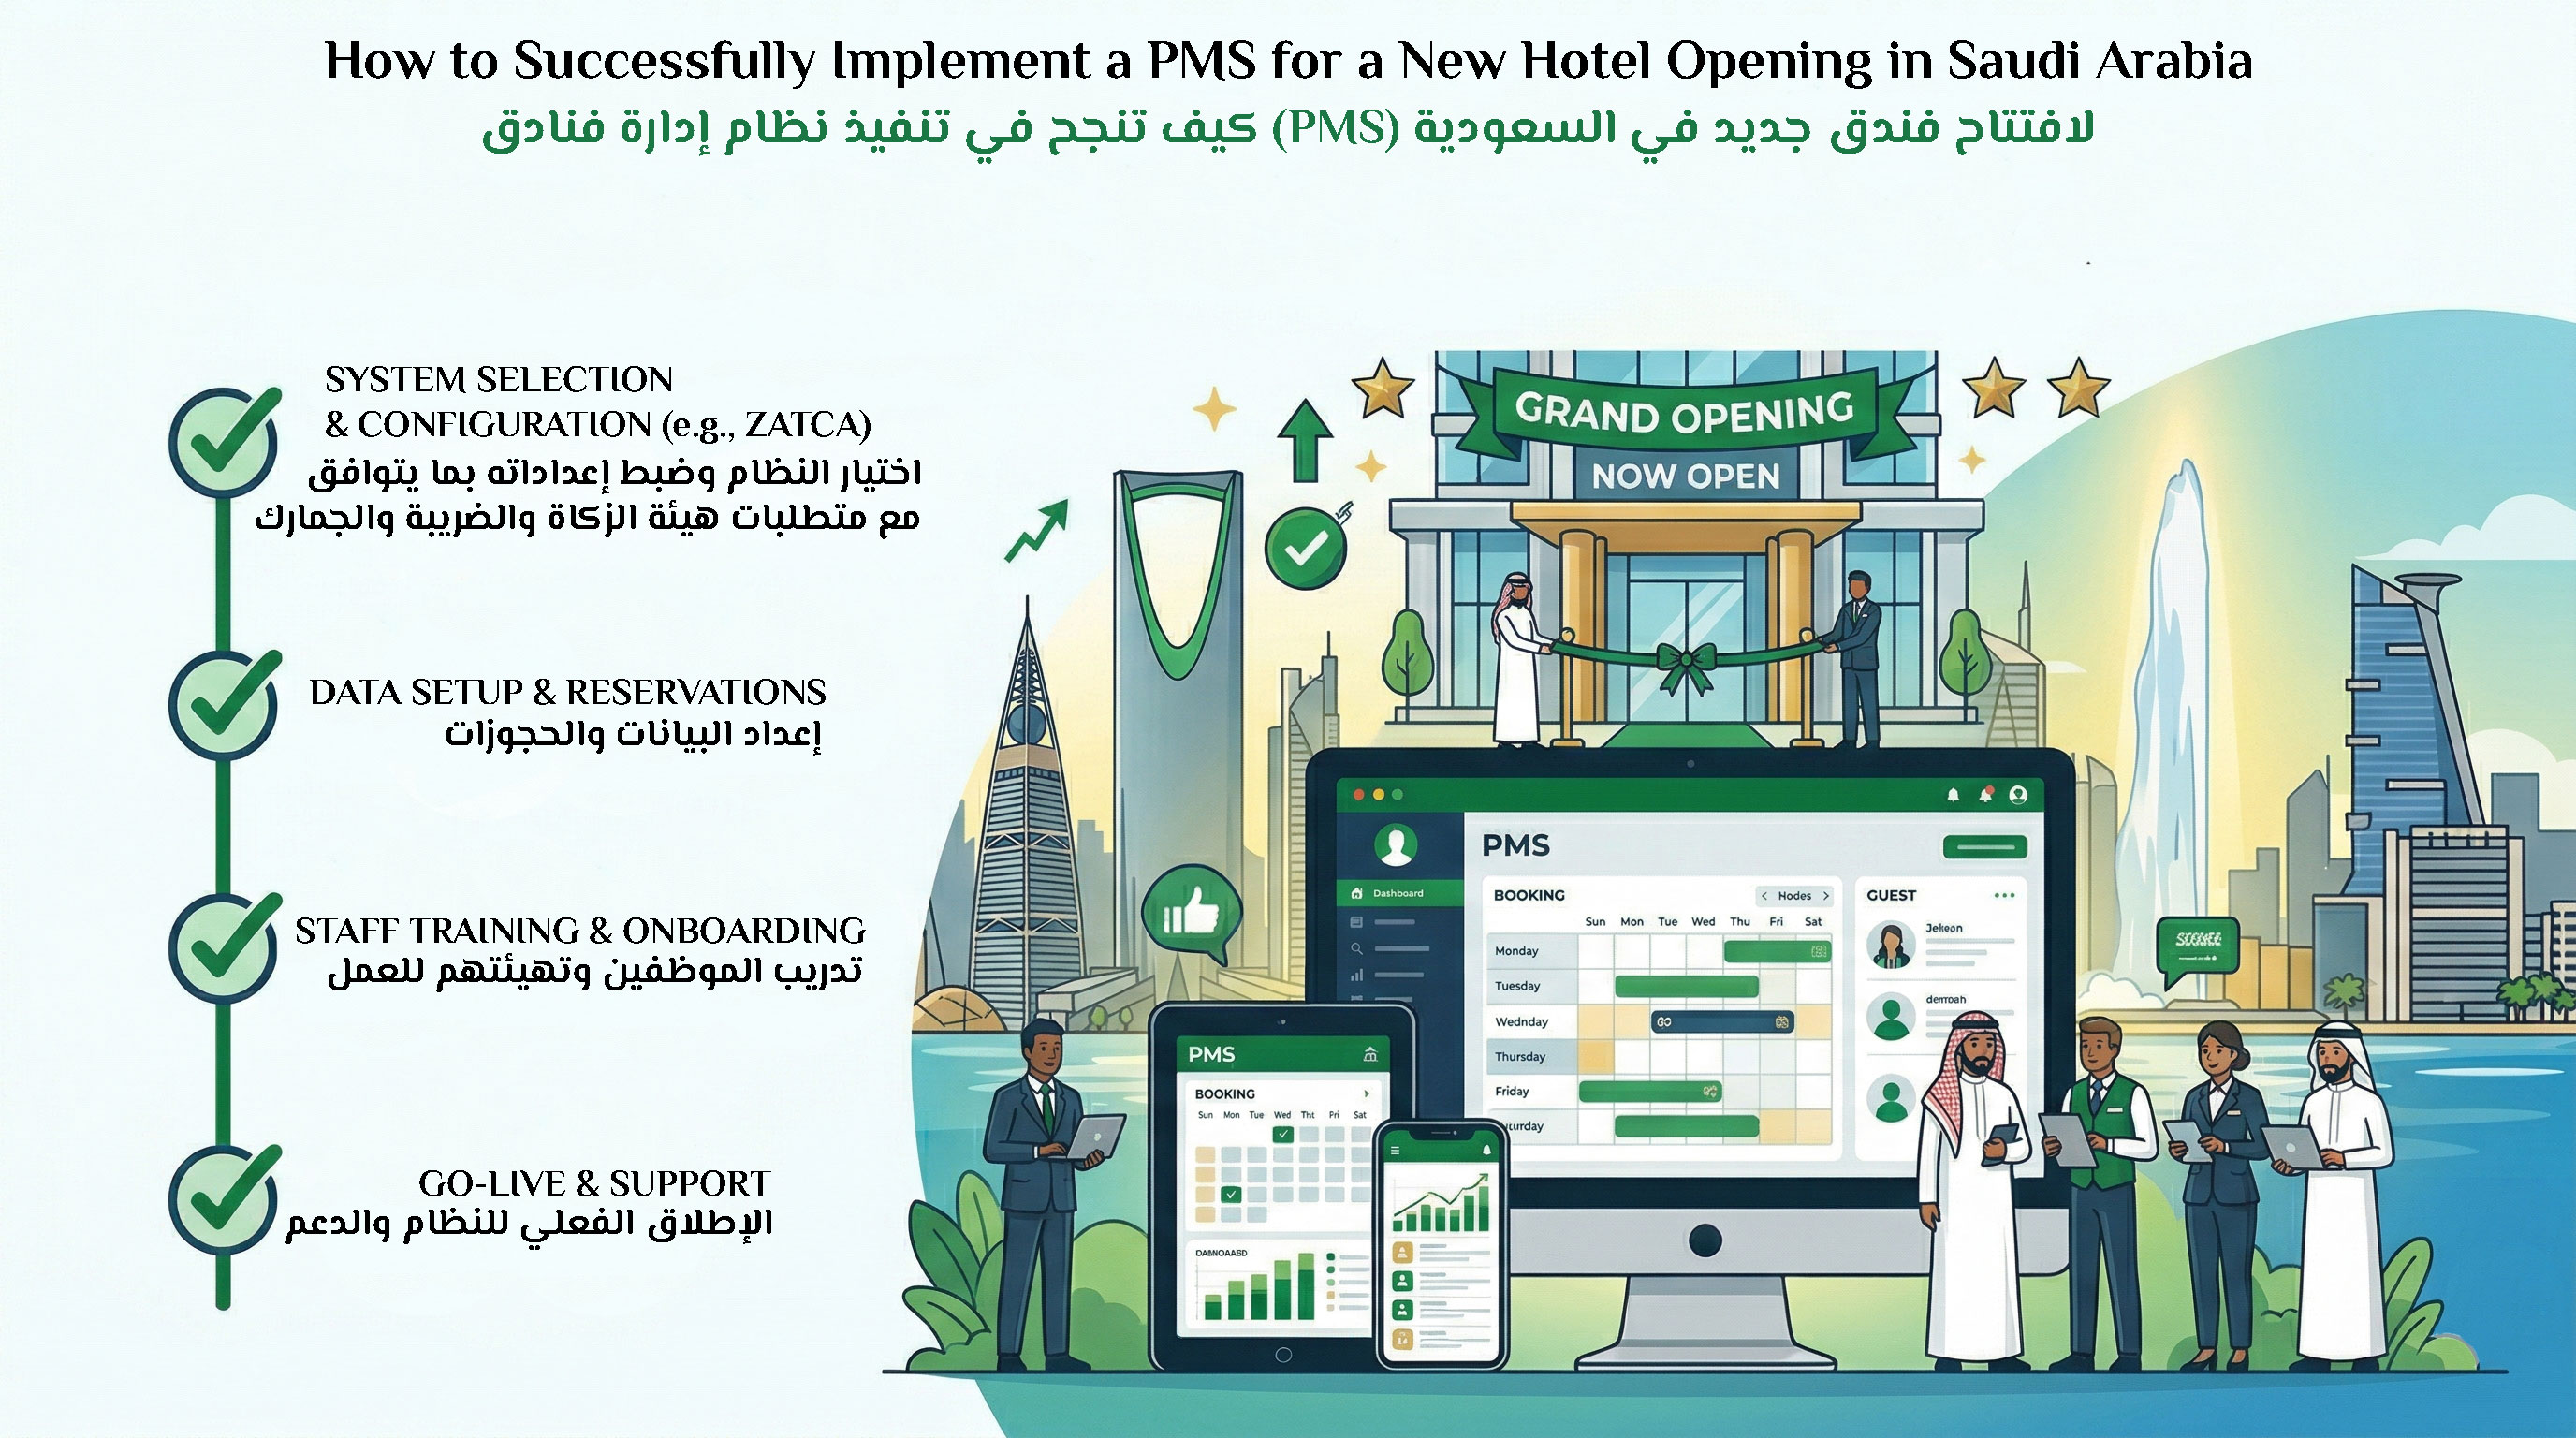
Step‑by‑step guide to implementing a PMS for a new hotel opening in Saudi Arabia. Covering ZATCA, Shomoos, check‑in automation, and best practices for a successful launch. Free demo from Fandaqa...

Discover why a local PMS vendor in Riyadh or Jeddah is the smart choice for your hotel. Faster support, ZATCA & Shomoos compliance, Arabic interface, and data residency. Free demo from Fandaqah...
Discover the best PMS for serviced apartments in Saudi Arabia. Automate check-in, manage multiple units, ensure ZATCA & Shomoos compliance, and boost revenue. Free demo for property managers...
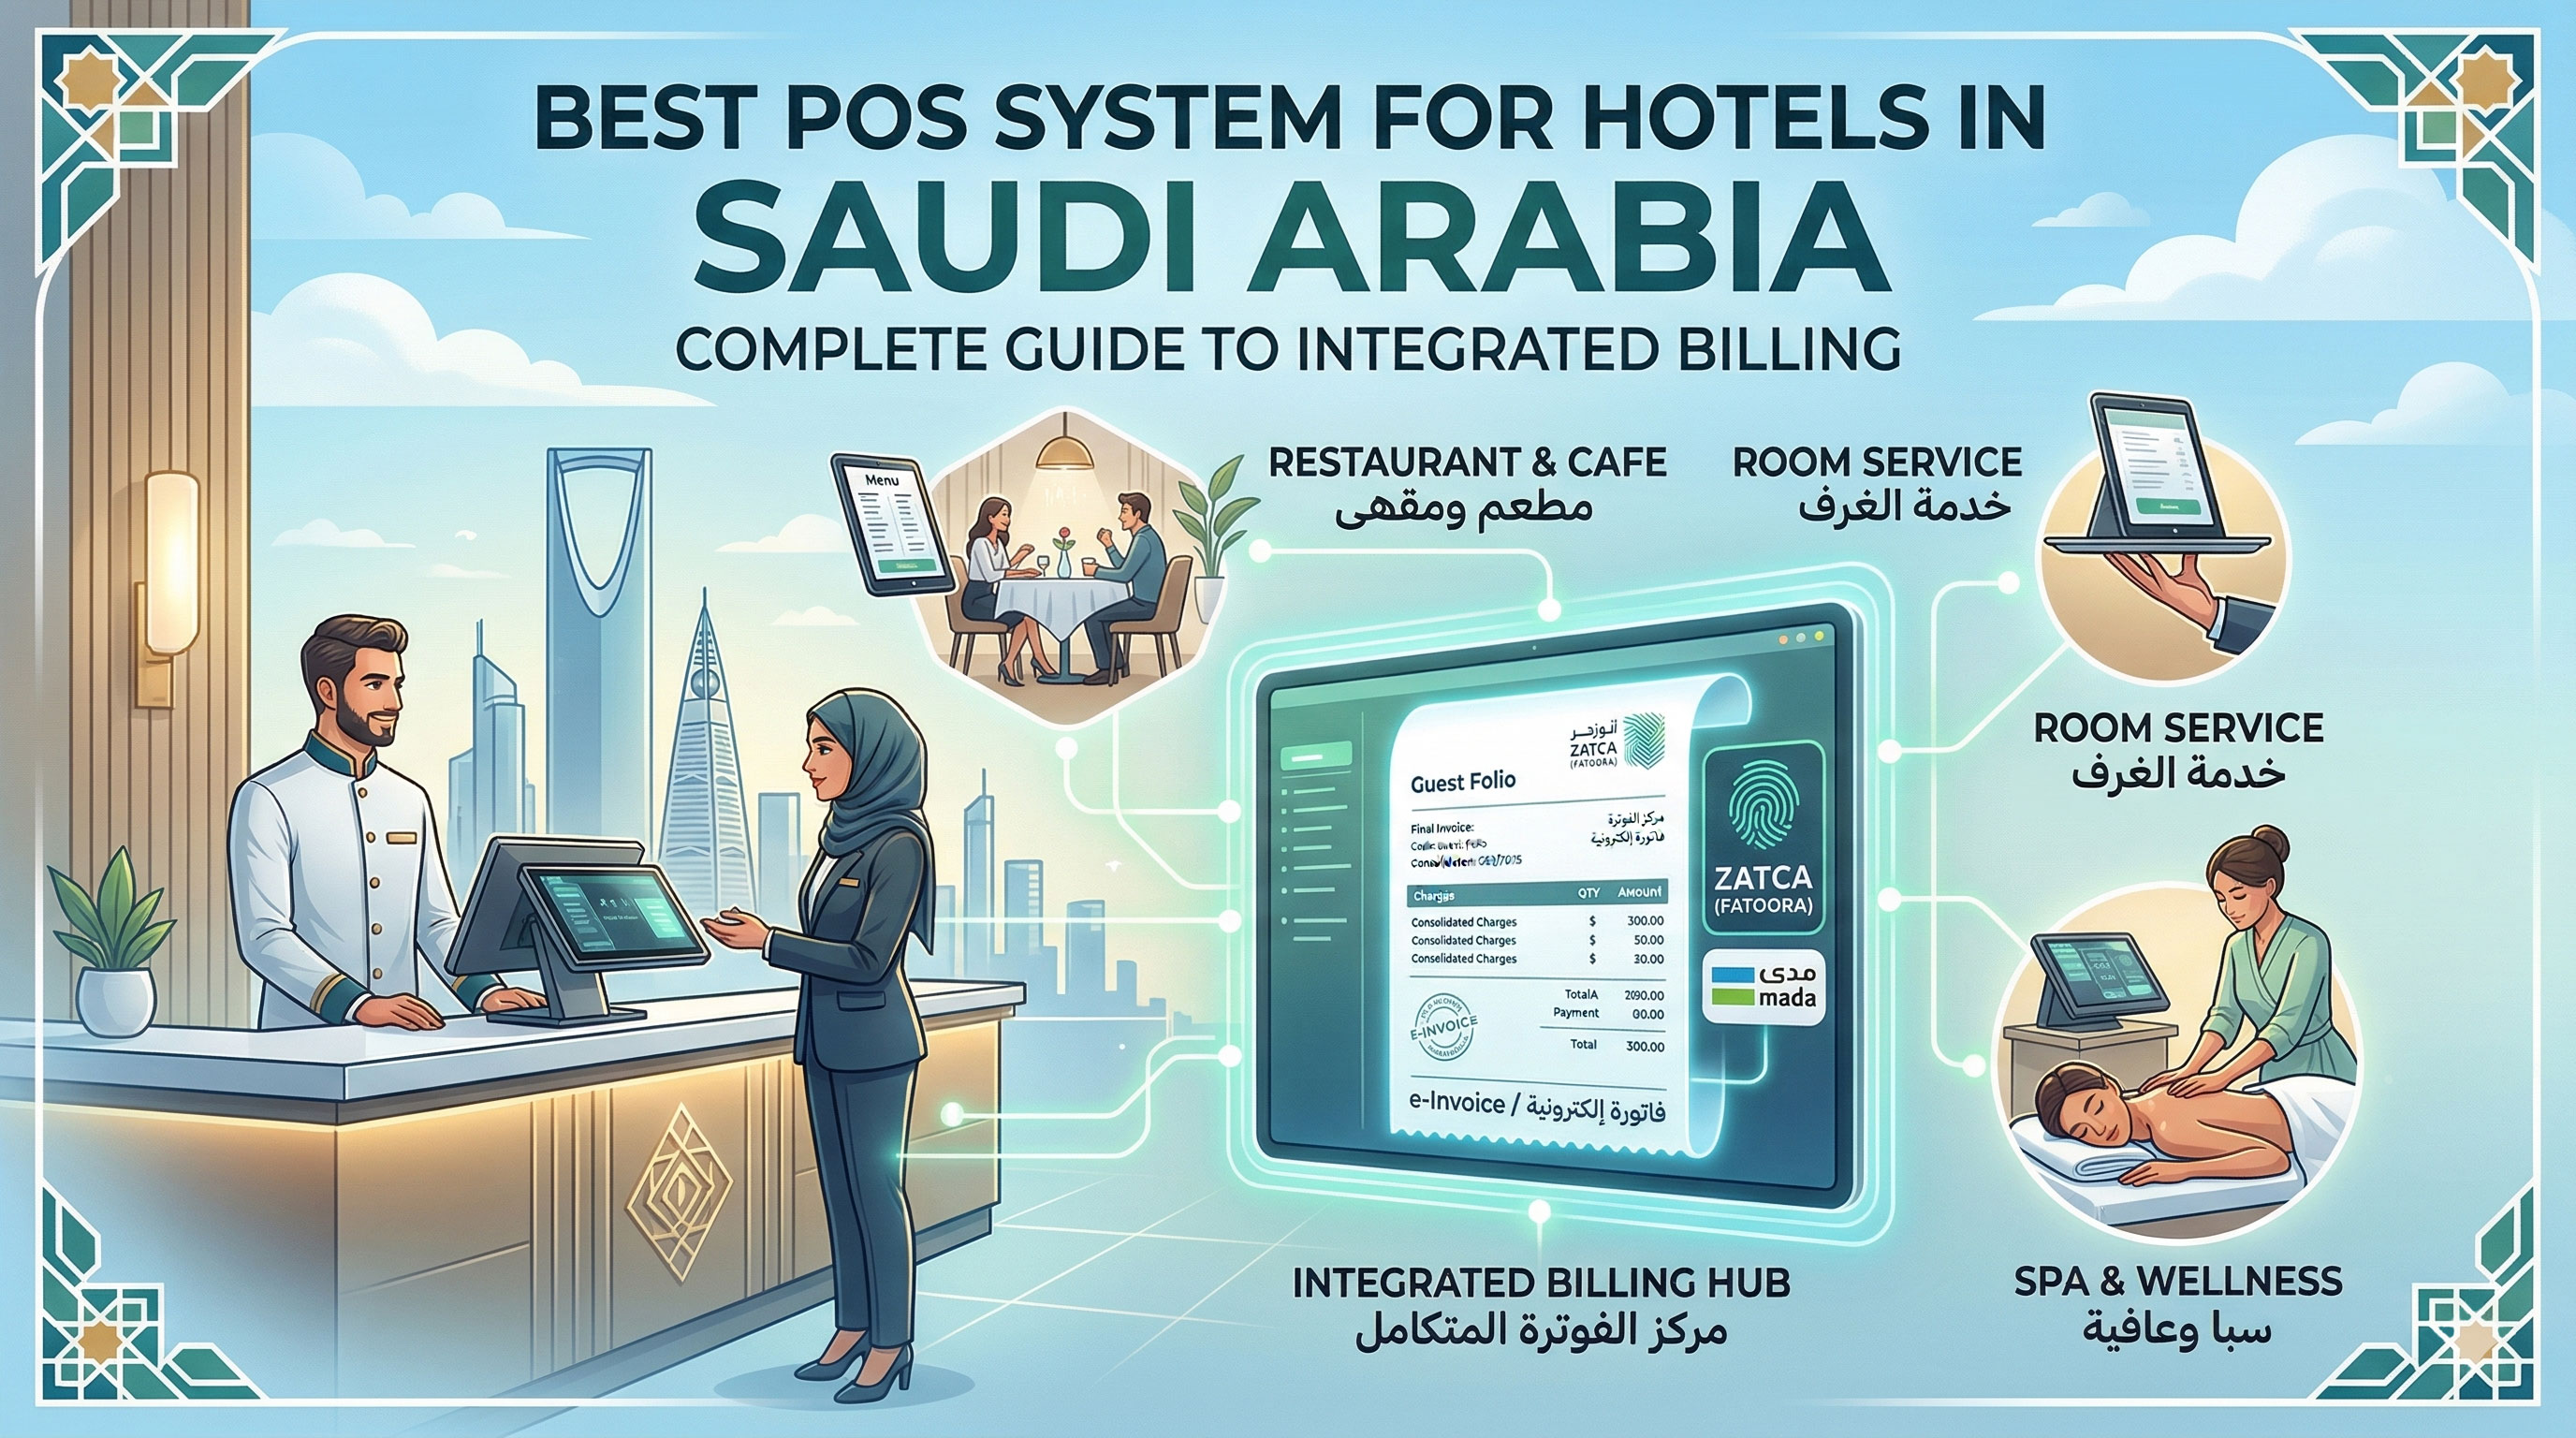
Discover the best POS system for hotels in Saudi Arabia. Integrate F&B, spa, and retail billing with your hotel PMS. ZATCA compliant, Shomoos ready. Free demo for hoteliers...
Fandaqah is Saudi Arabia's leading hotel management software. ZATCA, Shomoos & Ministry of Tourism compliant. PMS, booking engine & channel manager in one platform....
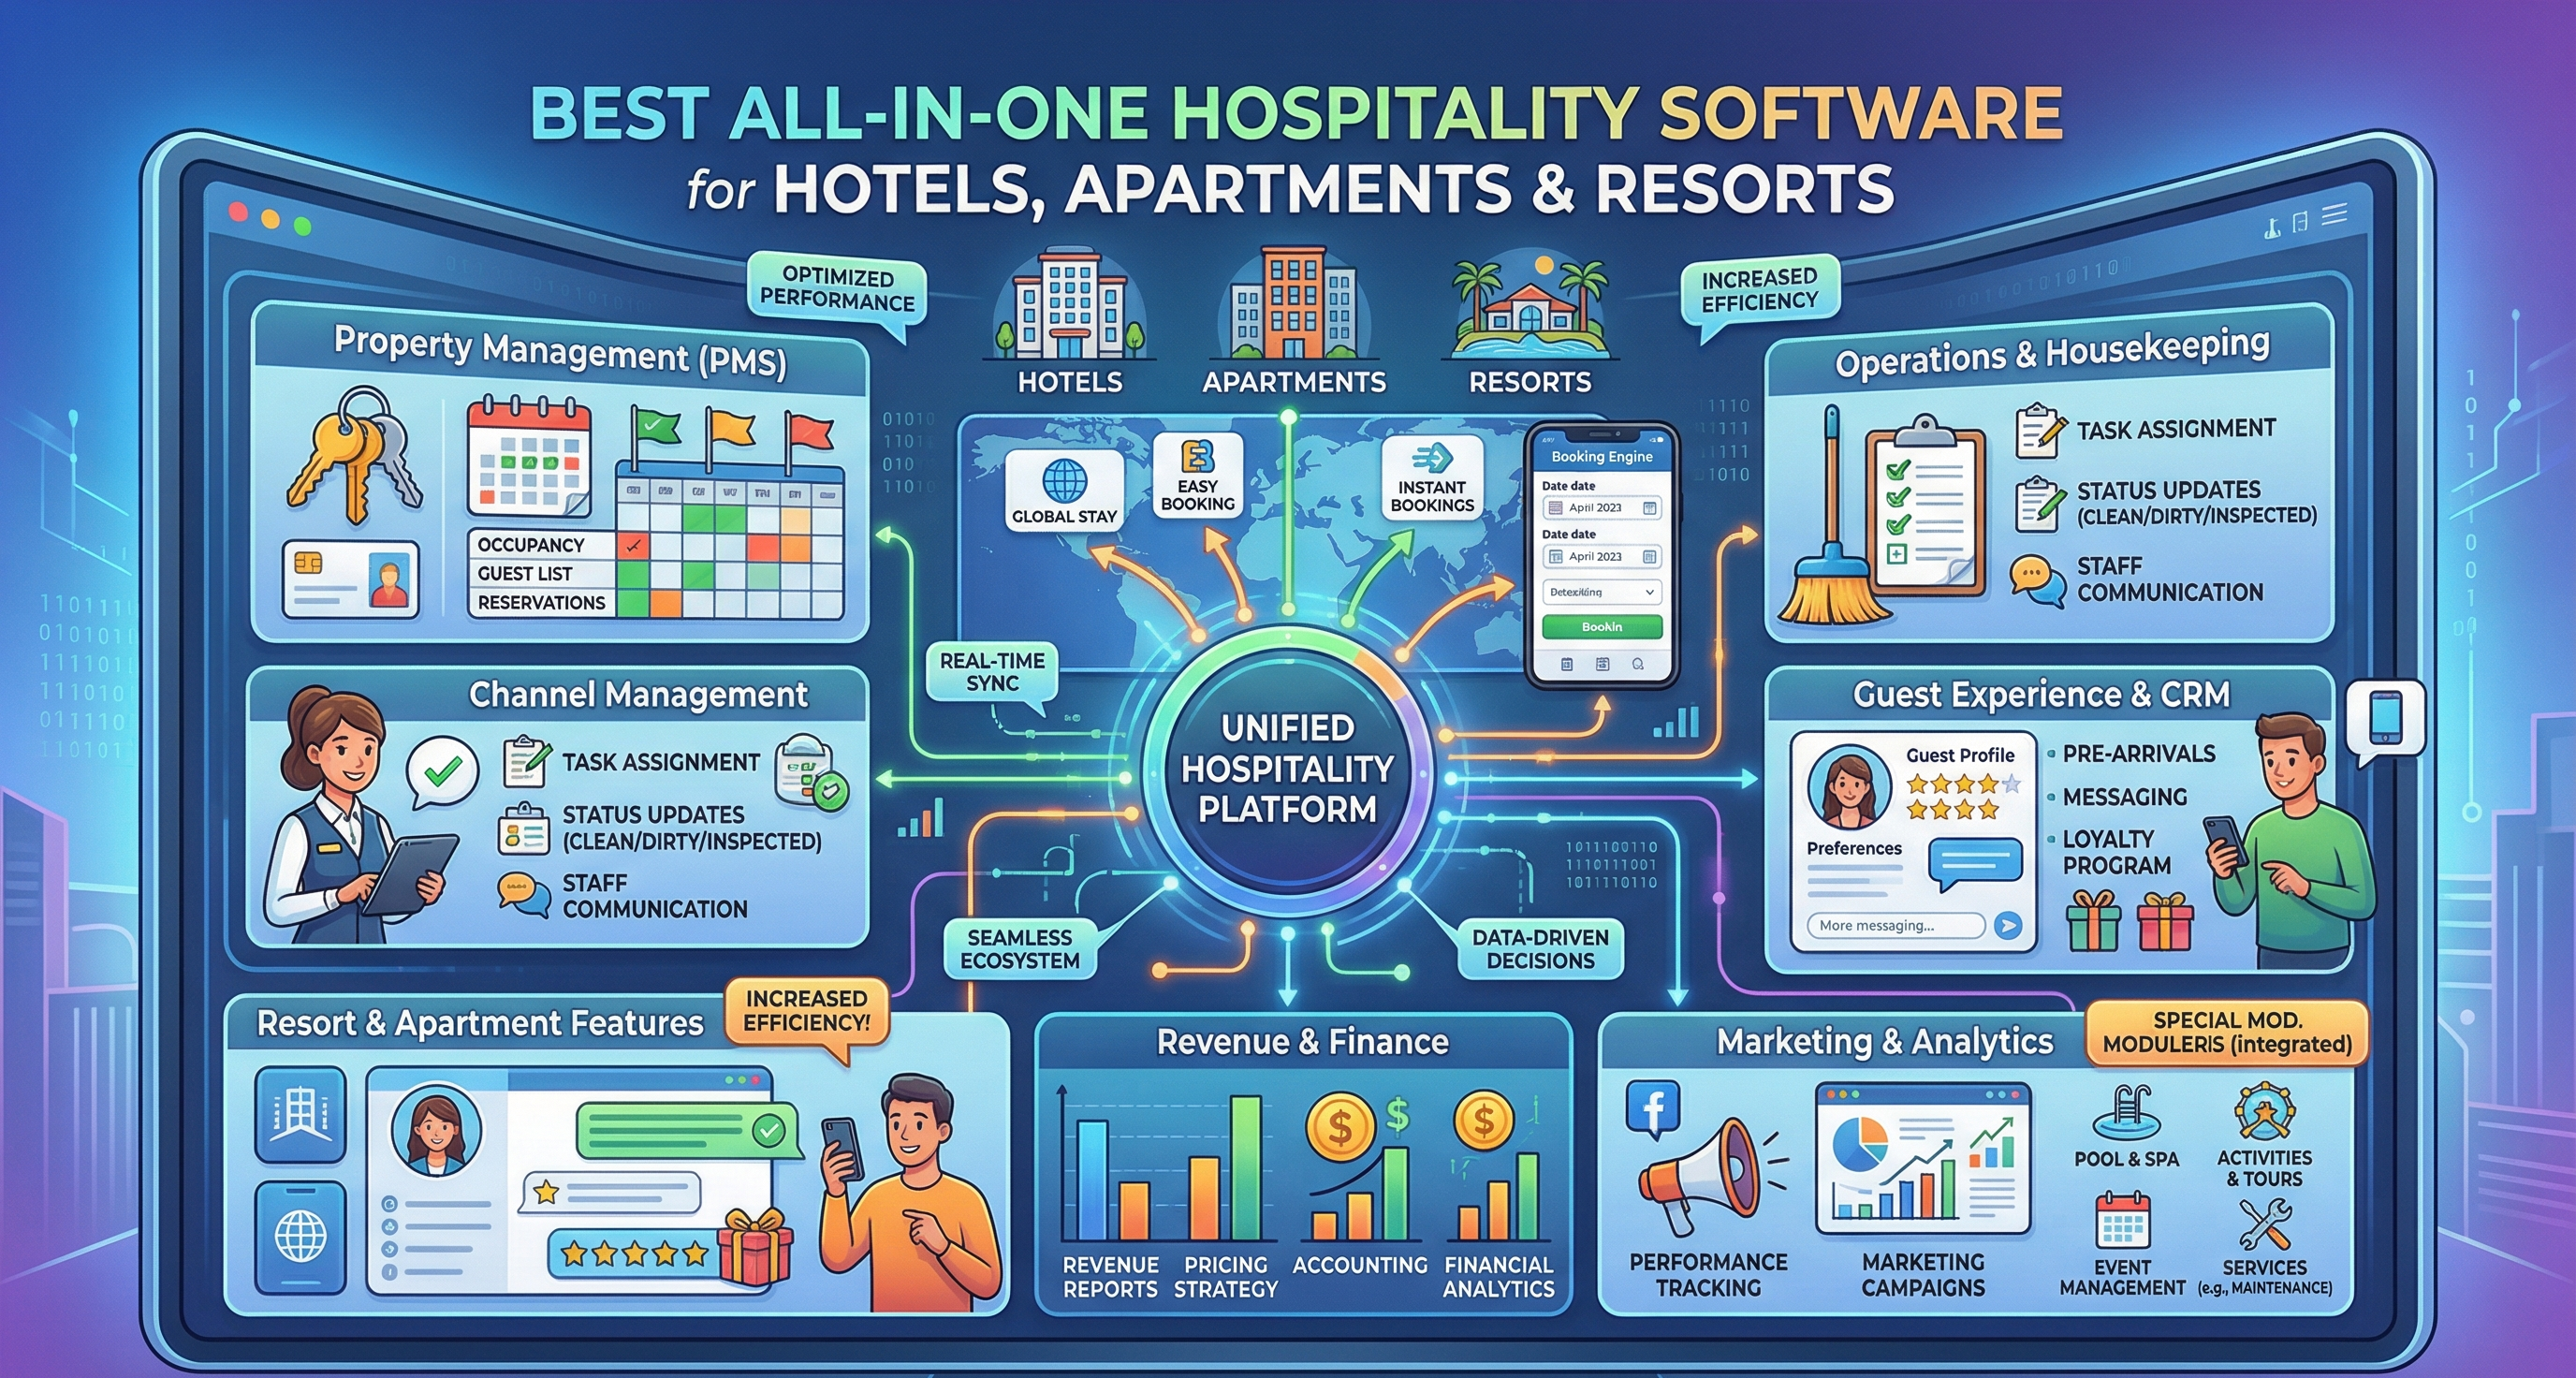
Discover Fandaqah trusted property management software for hotels, apartments & resorts. ZATCA, Shomoos & Tourism compliant. Request your free trial today!...
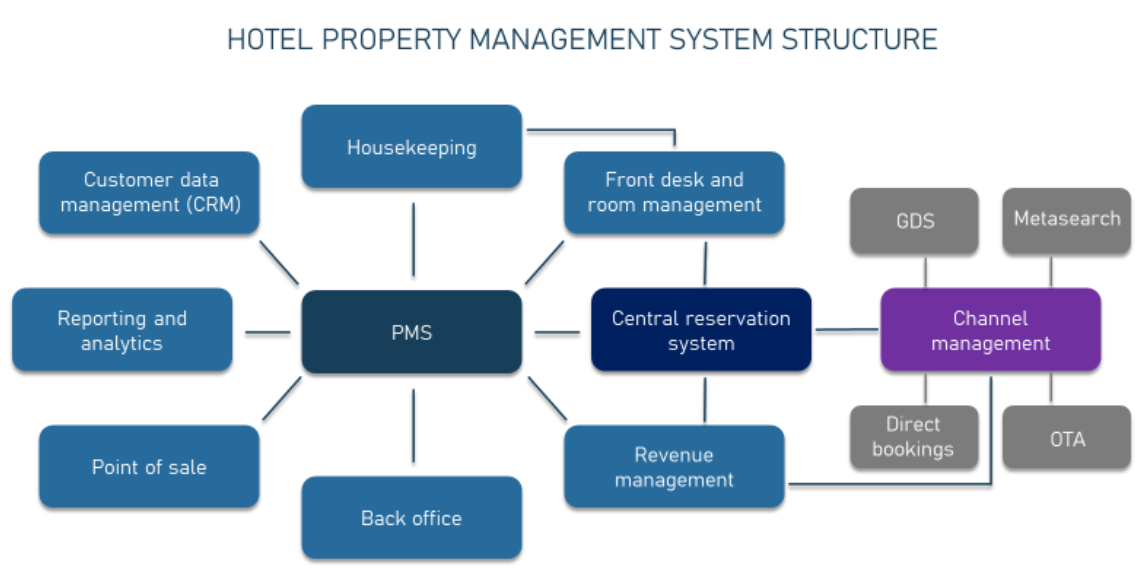
Fandaqah PMS automates hotel check‑in, ensures ZATCA Phase 2 e‑invoicing & Shomoos integration. 85% faster, trusted by 850+ Saudi properties. Start your free trial....
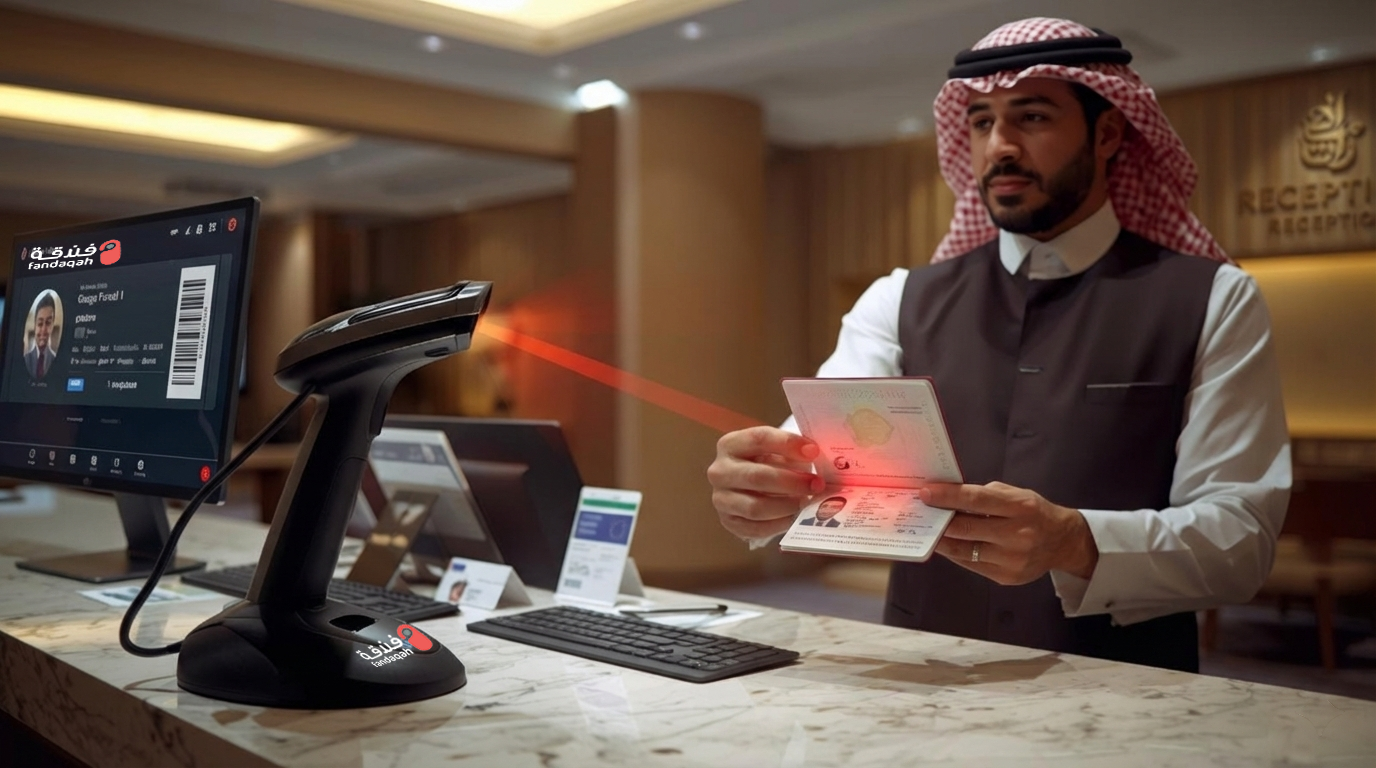
Automate hotel check-in Saudi Arabia with passport scanning. ZATCA compliant, Shomoos integrated. Reduce waiting time 70%. Free demo!...
Join Fandaqah's partner program for hotel management software Saudi Arabia. Earn 200 SAR per referral, ZATCA compliant. 800+ hotels trusted!...
Complete guide to analyzing guest feedback and improving hotel performance in Saudi Arabia. Learn about KPIs, technology, ZATCA & Shomoos compliance, and strategies to increase revenue and guest satis...
Discover how Fandaqah Channel Manager helps Saudi hotels manage and streamline rates across all OTA platforms. Increase direct bookings, automate distribution, ensure ZATCA & Shomoos compliance, and b...
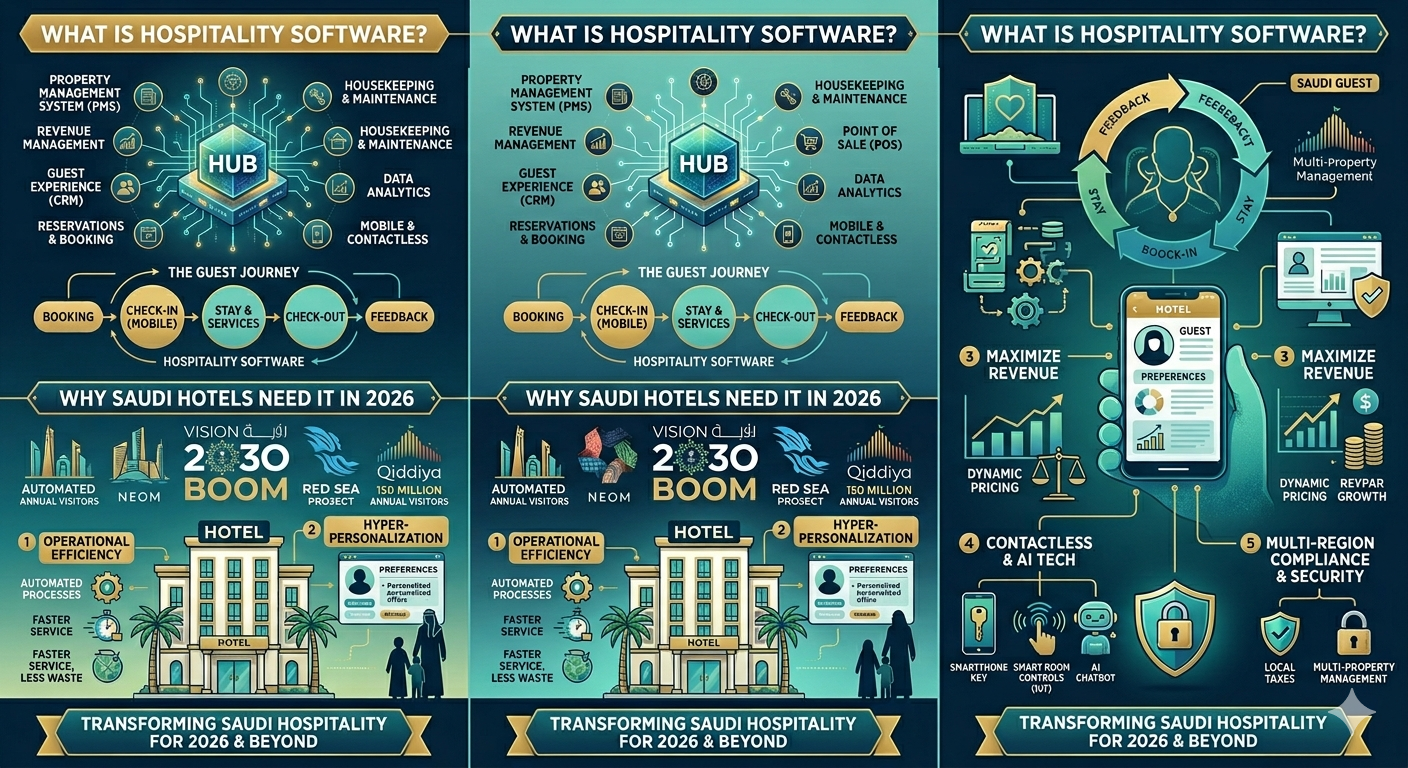
Discover what hospitality software is and why Saudi hotels need it in 2026. Complete guide to hotel management systems, check-in automation, ZATCA & Shomoos compliance, and guaranteed ROI. Fandaqah so...
Complete guide to OTA channel manager for hotel distribution in Saudi Arabia. Learn how to increase bookings, automate distribution, comply with ZATCA & Shomoos, and boost revenue. Fandaqah solutions....

Complete hotel audit guide for 2026: learn about night audit procedures, financial reports, compliance with ZATCA & Shomoos, and how automated audits improve accuracy and efficiency for Saudi hotels....
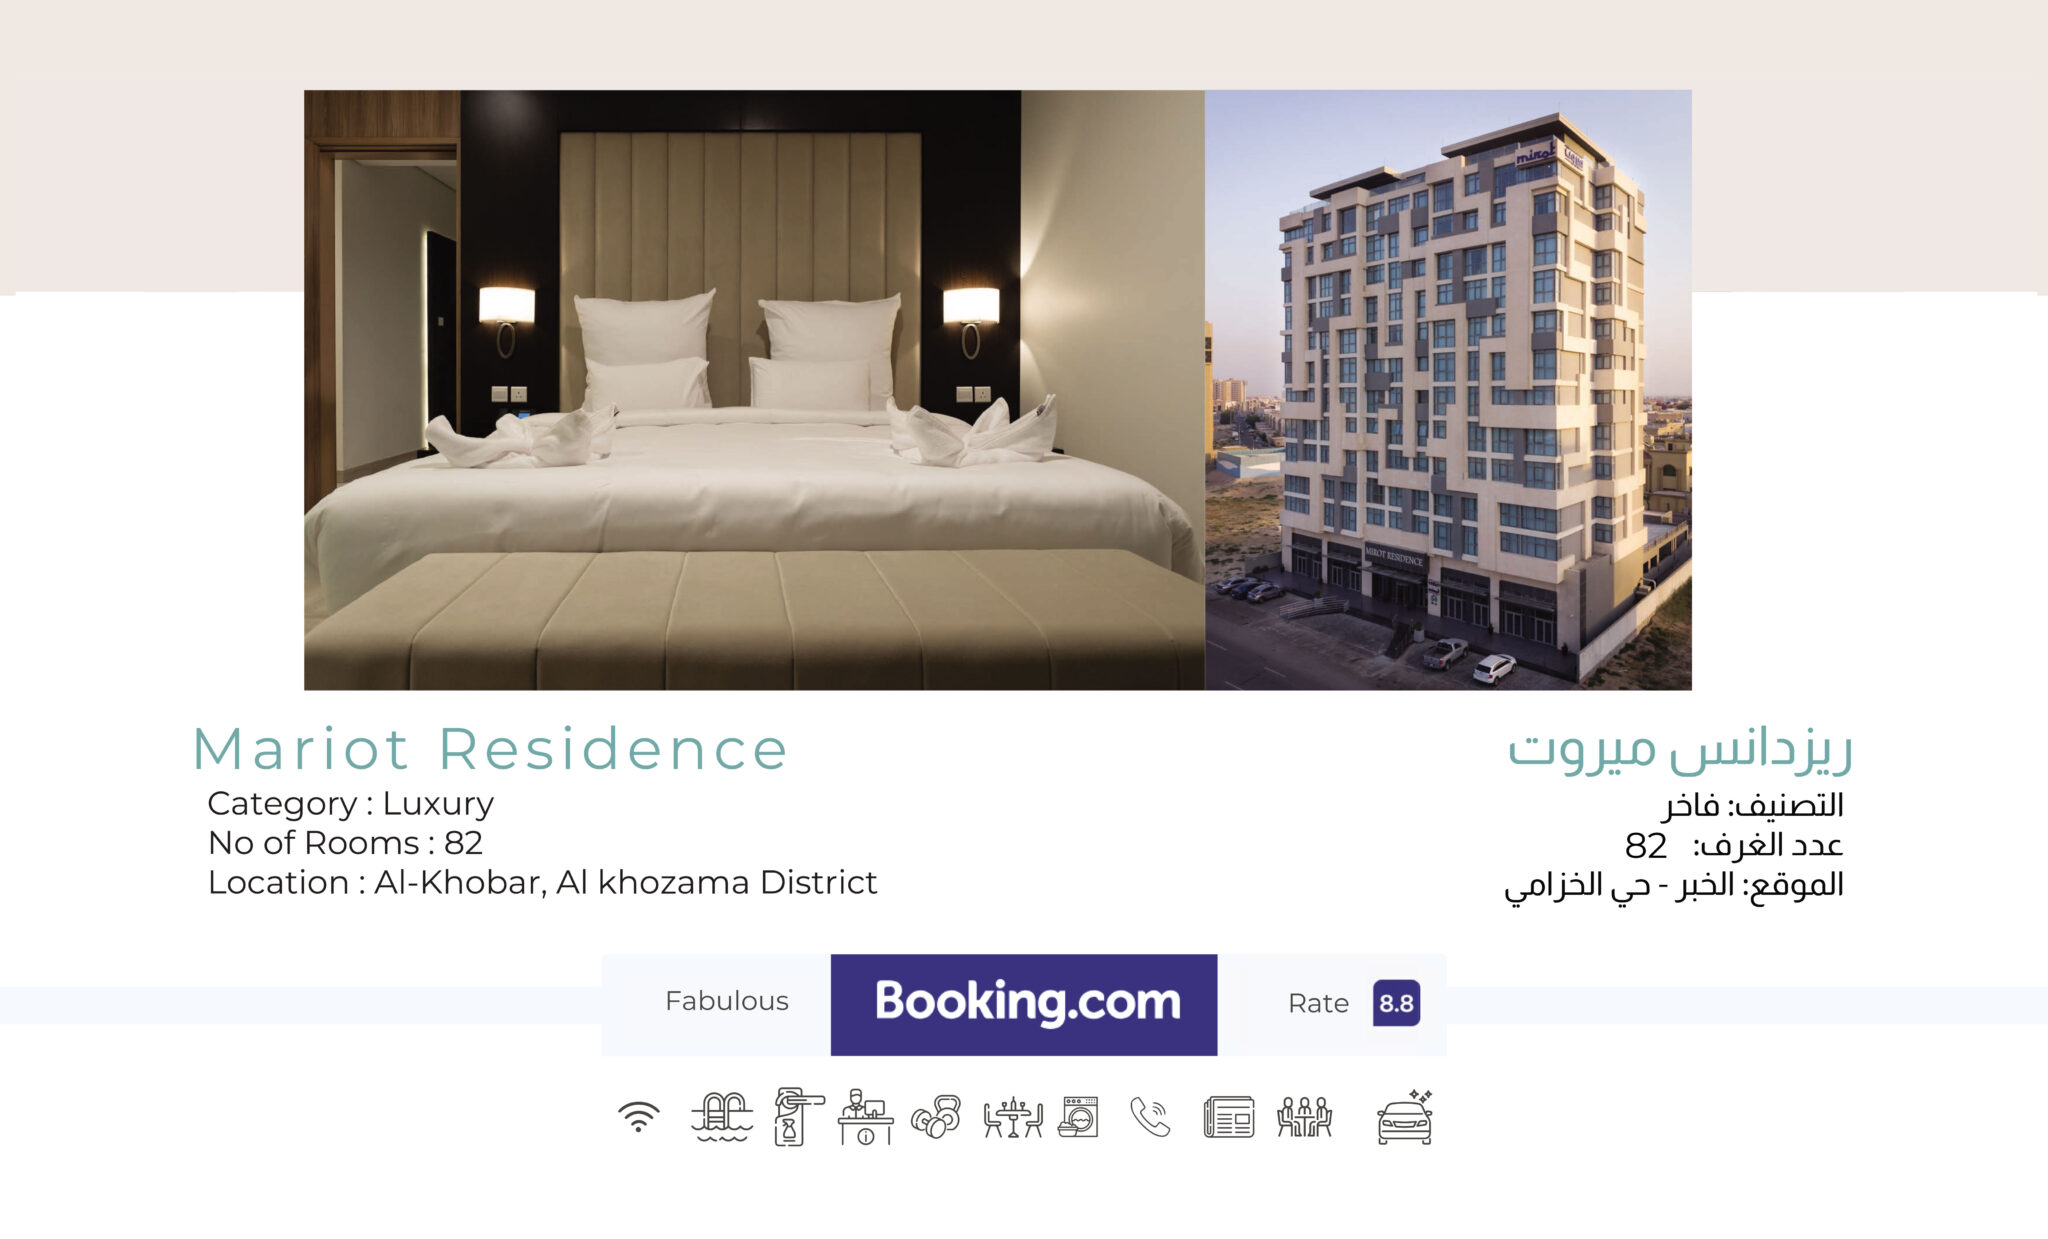
Mariot Residence began as a modest 1-star property with: Limited digital infrastructure Manual operations Basic amenities Difficulty attracting guests and maintaining service quality...

In the hospitality industry, room pricing isn’t just a number on a screen—it’s a strategic decision that directly impacts revenue, occupancy, and guest satisfaction....
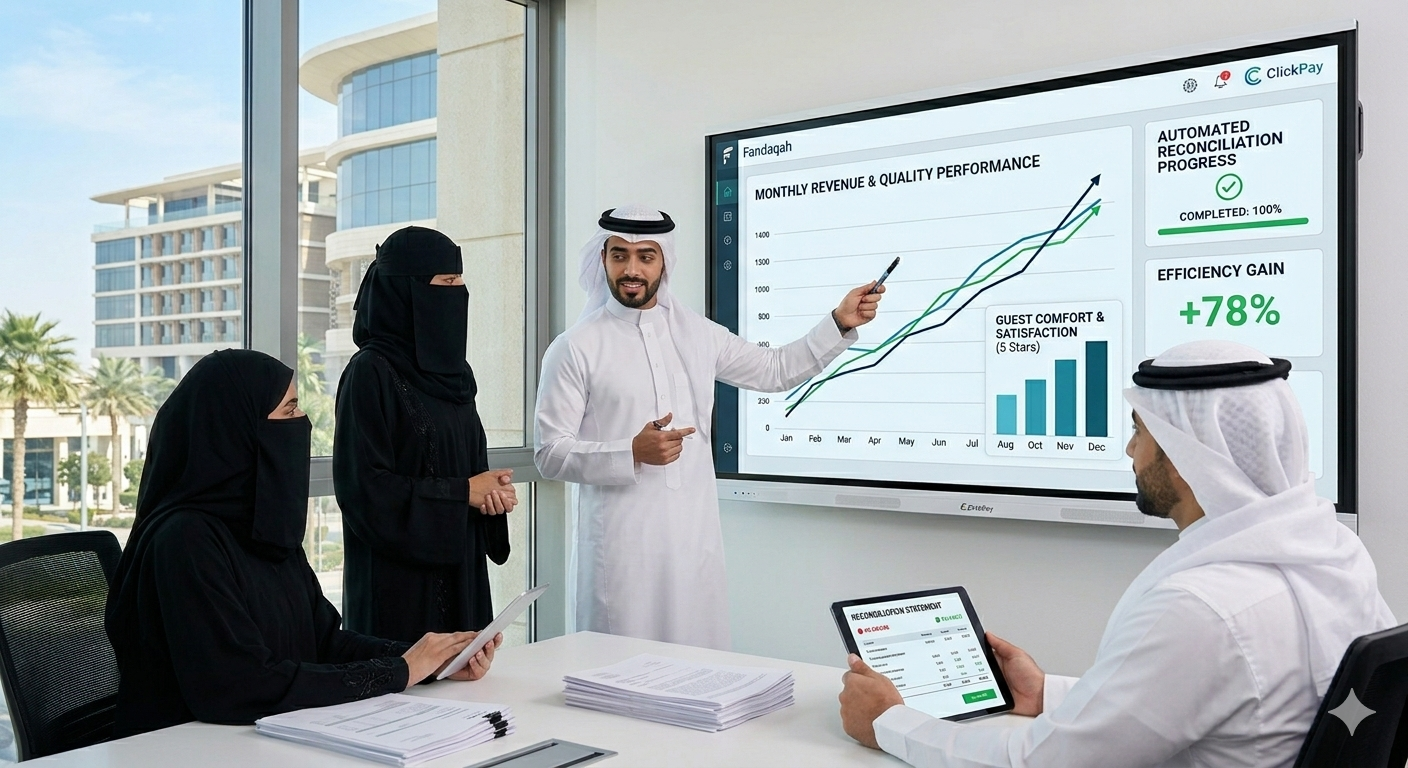
In hospitality, every moment matters. From the first greeting at the front desk to the final checkout, hotels strive to offer a seamless and comfortable experience for every guest. Yet, one aspect oft...
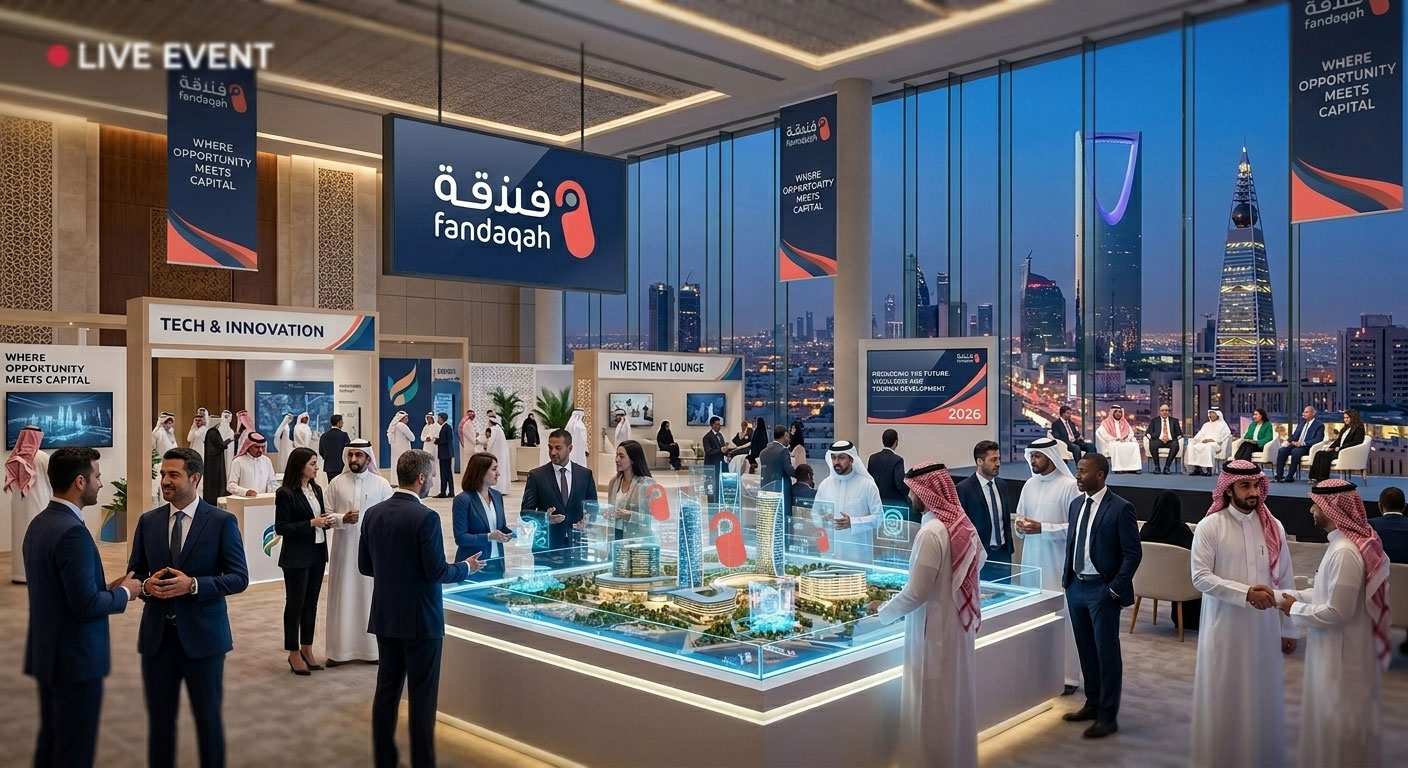
The complete guide to the Saudi Future Hospitality Summit 2026: dates, venue, speakers, investment opportunities, technology, and ZATCA & Shomoos compliance. Join 1,500+ industry leaders in Riyadh....
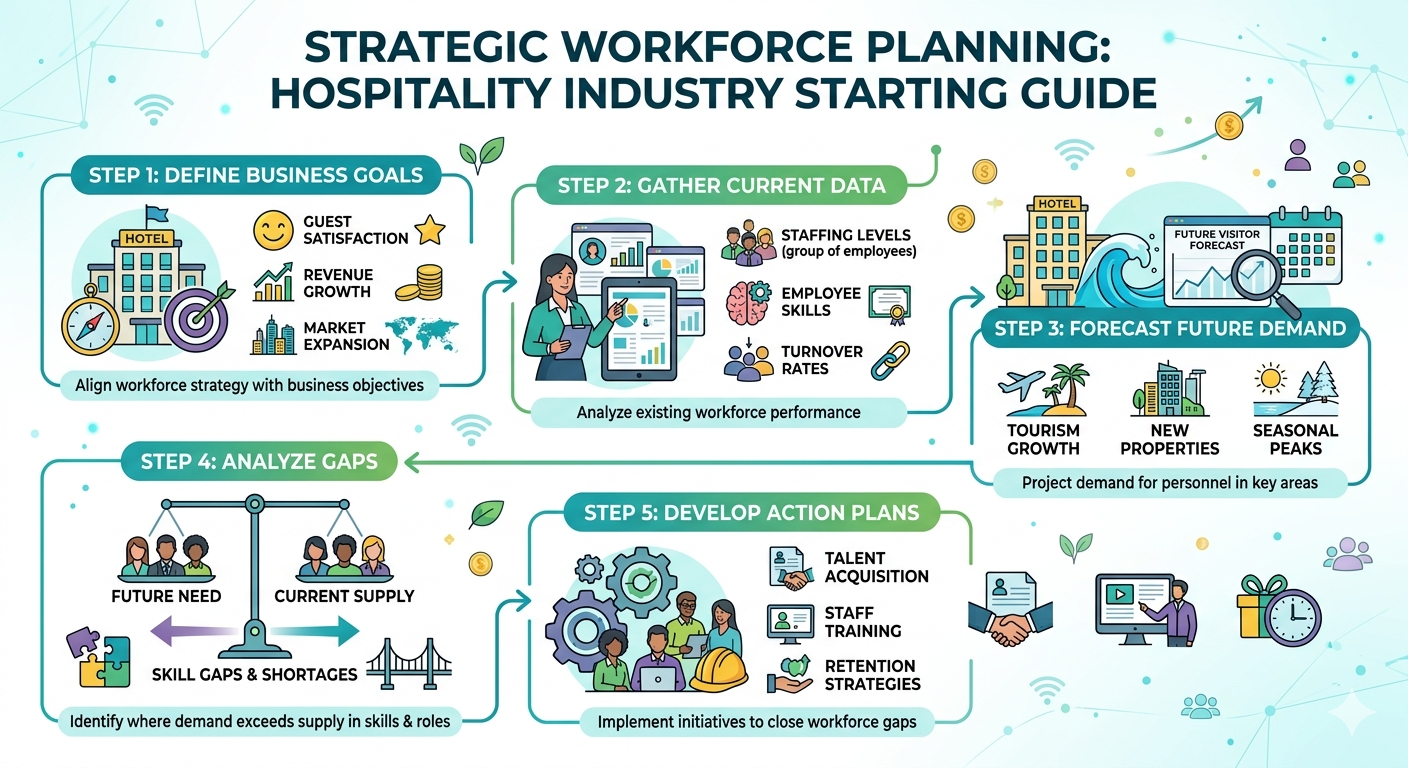
Master strategic workforce planning for Saudi hospitality. Achieve Nitaqat compliance, reduce turnover, and build Vision 2030-ready teams with expert strategies...
In line with Saudi Vision 2030, the tourism sector is undergoing an unprecedented digital transformation. One of the most impactful tools driving this change is the National Tourism Monitoring Platfor...
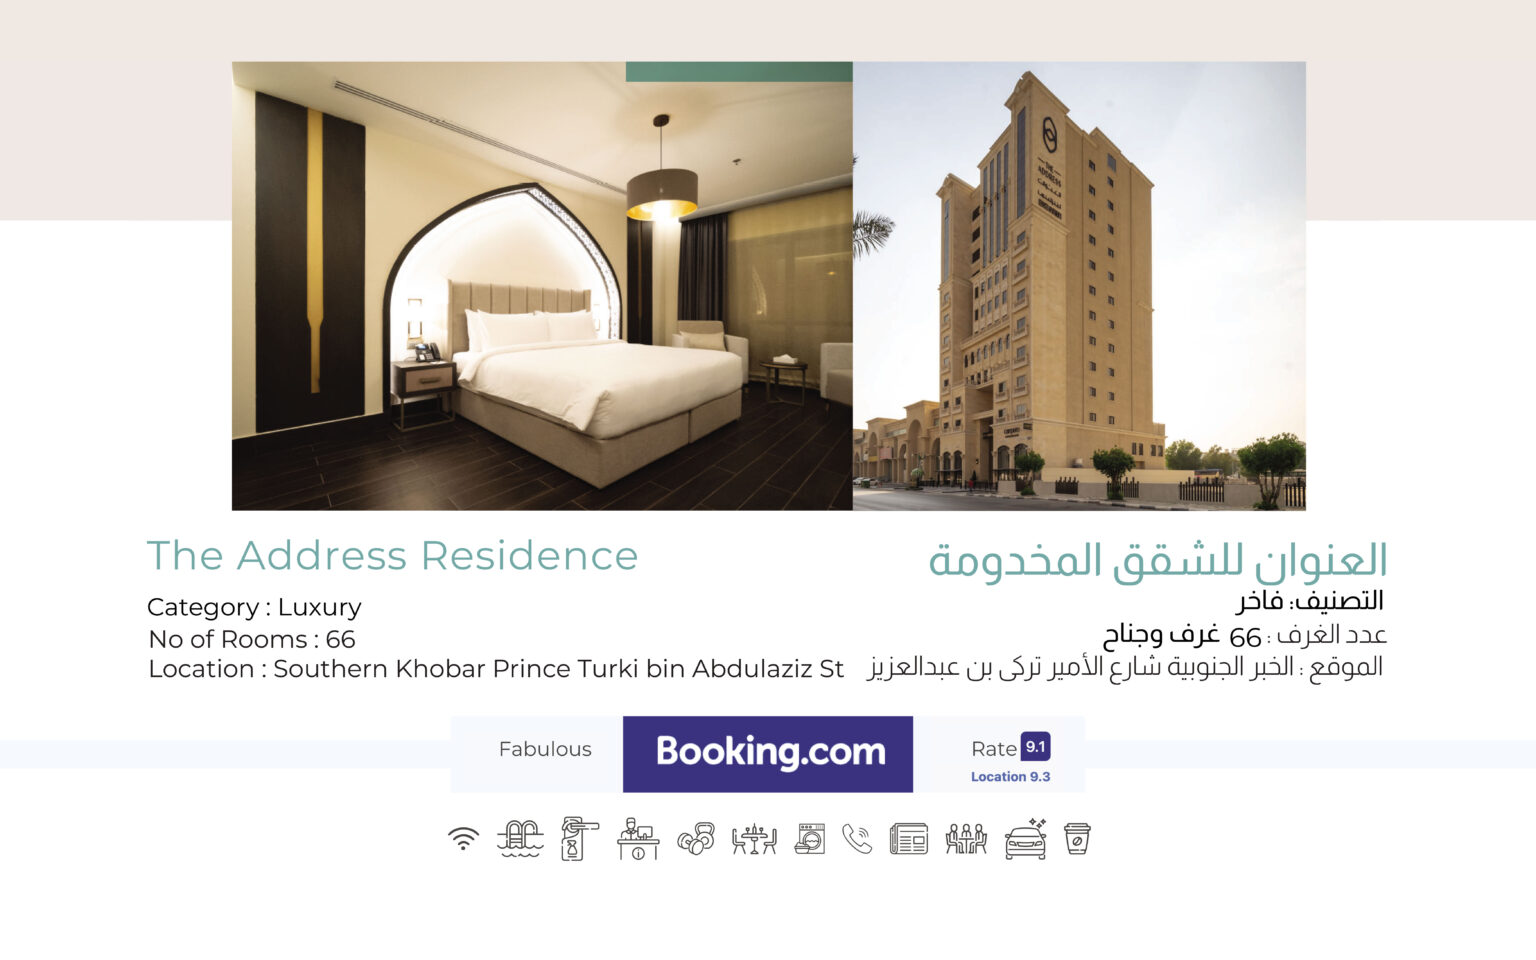
The management adopted Fandaqah PMS, a Saudi-built property management system designed for operational efficiency and government compliance. The result? A complete transformation across operations, gu...
In today’s hospitality landscape, competition is no longer just about location or star ratings. Success now hinges on how effectively a hotel leverages smart technologies to streamline operations an...